- Choose DNSRazzle when you want a free Apache-2.0 CLI that fuzzes brands with dnstwist, captures viewport screenshots, and scores them against the original with SSIM. 1–9
- Choose Have I Been Squatted to detect malicious domains and their infrastructure from a hosted service, with no scanner on your host, and to respond through rules, blocks and managed Takedowns. 7–8,10–20
- Use both if you want a local DNSRazzle pass with screenshot scoring, while Have I Been Squatted monitors the brand on a schedule, raises alerts and requests Takedowns. 3,7–9,11–12,19–22
At a glance#
| Have I Been Squatted | DNSRazzle | |
|---|---|---|
| What you run | ||
| What you run | Hosted malicious-domain detection and response10 | Local Python CLI for lookalike discovery and screenshot comparison1–2 |
| How you get it | ||
| How you get it | Open source and free; install from Git1–6 | |
| Lookalike discovery | ||
| Lookalike discovery | dnstwist permutations of one or many domains, then DNS resolve1–2 | |
| Cadence | ||
| Cadence | Scheduled lookups after you add a domain21 | |
| Page similarity | ||
| Page similarity | Favicon fingerprints and shared identifiers7–8 | |
| After a finding | ||
| After a finding | ||
| Mail probe | ||
| Mail probe | ||
| Deeper recon | ||
| Deeper recon | Port signals in enrichment7 | |
A local scan versus continuous monitoring#
DNSRazzle is a pure Python command-line tool for finding and comparing typosquatting, bitsquatting and homoglyph domains for brand impersonation. Install it from Git to run lookalike discovery on your own host without an account. You control when each scan runs and keep its CSV files and screenshots locally. No contractual scan quota appears in the README or the CLI. 1–2,5–6,23–24,28–29,32
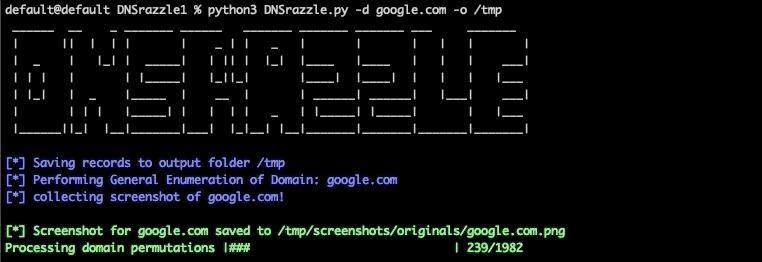
A run generates permutations with the pinned dnstwist engine, resolves them, screenshots non-original names that have a usable A record, and writes CSV and PNG output. Pass a single domain, a comma-separated list or a file of domains to cover many brands at once. DNSRazzle also adds a url-encoded-slash permutation that puts 2f in front of the name, aimed at links that hide an encoded slash (%2F). 1–3,8,23,28–29,33–34
Have I Been Squatted is a hosted platform. Domain Monitoring combines generated lookalikes with certificate transparency and newly registered domains. Have I Been Squatted states that lookups run at least once every 24 hours after you add a domain. Ad-hoc Typosquat and Analyze lookups cover one-off checks without standing up a scanner. 11–12,21,35–37
Picture a security engineer who needs a Friday lookalike pass on three brands. With DNSRazzle they install the tool and its browser, point -d or -f at those names, and leave with CSV files and screenshot pairs on disk. With Have I Been Squatted they add the three domains once. Lookups then repeat on a schedule, and new matches arrive as alerts. 1–3,11–12,21–23,28–29,32
Screenshots, similarity and active probes#
DNSRazzle's distinctive check is visual. Playwright captures a 1920×1080 viewport of the original site and of each discovered lookalike with an A record. VisionUtil then computes structural similarity (SSIM) between the converted images. Console labels mark a pair identical at 1.00, similar at 0.90 or above, or different below that, and scores land in domain_similarity.csv. Have I Been Squatted matches favicon fingerprints and shared identifiers such as tag manager IDs. It does not score screenshot similarity against the original site. 1–3,7–9
A scan that resolves lookalikes also contacts their servers. DNSRazzle sends an HTTP request to port 80 of each lookalike with an A record. For each lookalike with an MX record, it reads the mail server's greeting, and the mx-spy check connects to the lookalike's mail server and sends a real test email through it. No flag turns these probes off without editing the code. Only the -g dry run, which prints permutations without DNS lookups, avoids them. Run scans from a host where that contact is acceptable. 1–2,23,28–31
Optional flags go deeper. -n and -r run nmap -A -sV and a dnsrecon-style report on permutations selected by the screenshot path. A -b blocklist writes IPs and hosts for lookalikes at or above a similarity threshold you set. Screenshot navigation starts from an http:// URL, and DNSRazzle does not try HTTPS first. 2–3,28,31
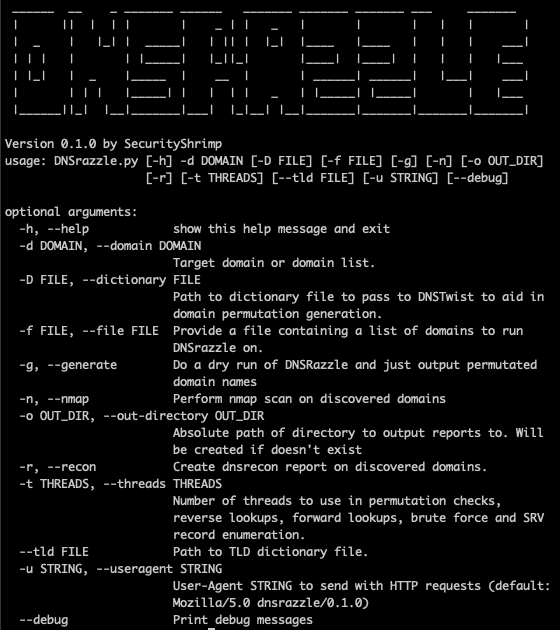
Have I Been Squatted brings DNS records, RDAP registration data, hosting details, MX records and SMTP banners, open-port signals, redirects and page content, and screenshots into the hosted result. Use the isolated browser to inspect a live page. A first-party model classifies each result as legitimate, parked or phishing, with a confidence score, and rules decide which findings alert your team. The hosted service collects this evidence, so your team runs no scanner on its own host. 7–8,11–13,21,36,38–44
Domain protection
Detect adversary infrastructure while it is being staged.
Have I Been Squatted helps security teams detect lookalike domains, certificate and DNS changes, and staging infrastructure, investigate the evidence, and coordinate takedowns.
What happens after the scan#
DNSRazzle ends when the process exits. Output is files under -o: CSV rows, optional blocklist and recon files, and PNG screenshots. The -e flag can email those CSV files through an SMTP server you configure. No public documentation of a scheduler, run history, suppression list, case status, webhooks, SIEM connectors or managed takedowns was found for DNSRazzle. 1–2,23–24,28–29,45
Have I Been Squatted keeps the workflow after discovery. Rules from a maintained library or your own logic can raise an alert, deliver a finding to a SIEM, push a domain to Network Enforcement or request a Takedown. Connectors cover named SIEMs, gateways, mail filters, Slack, webhooks and an MCP server. An analyst reviews every managed Takedown and reports the domain to its host and registrar. 11,13–20,25,35,37,46–49
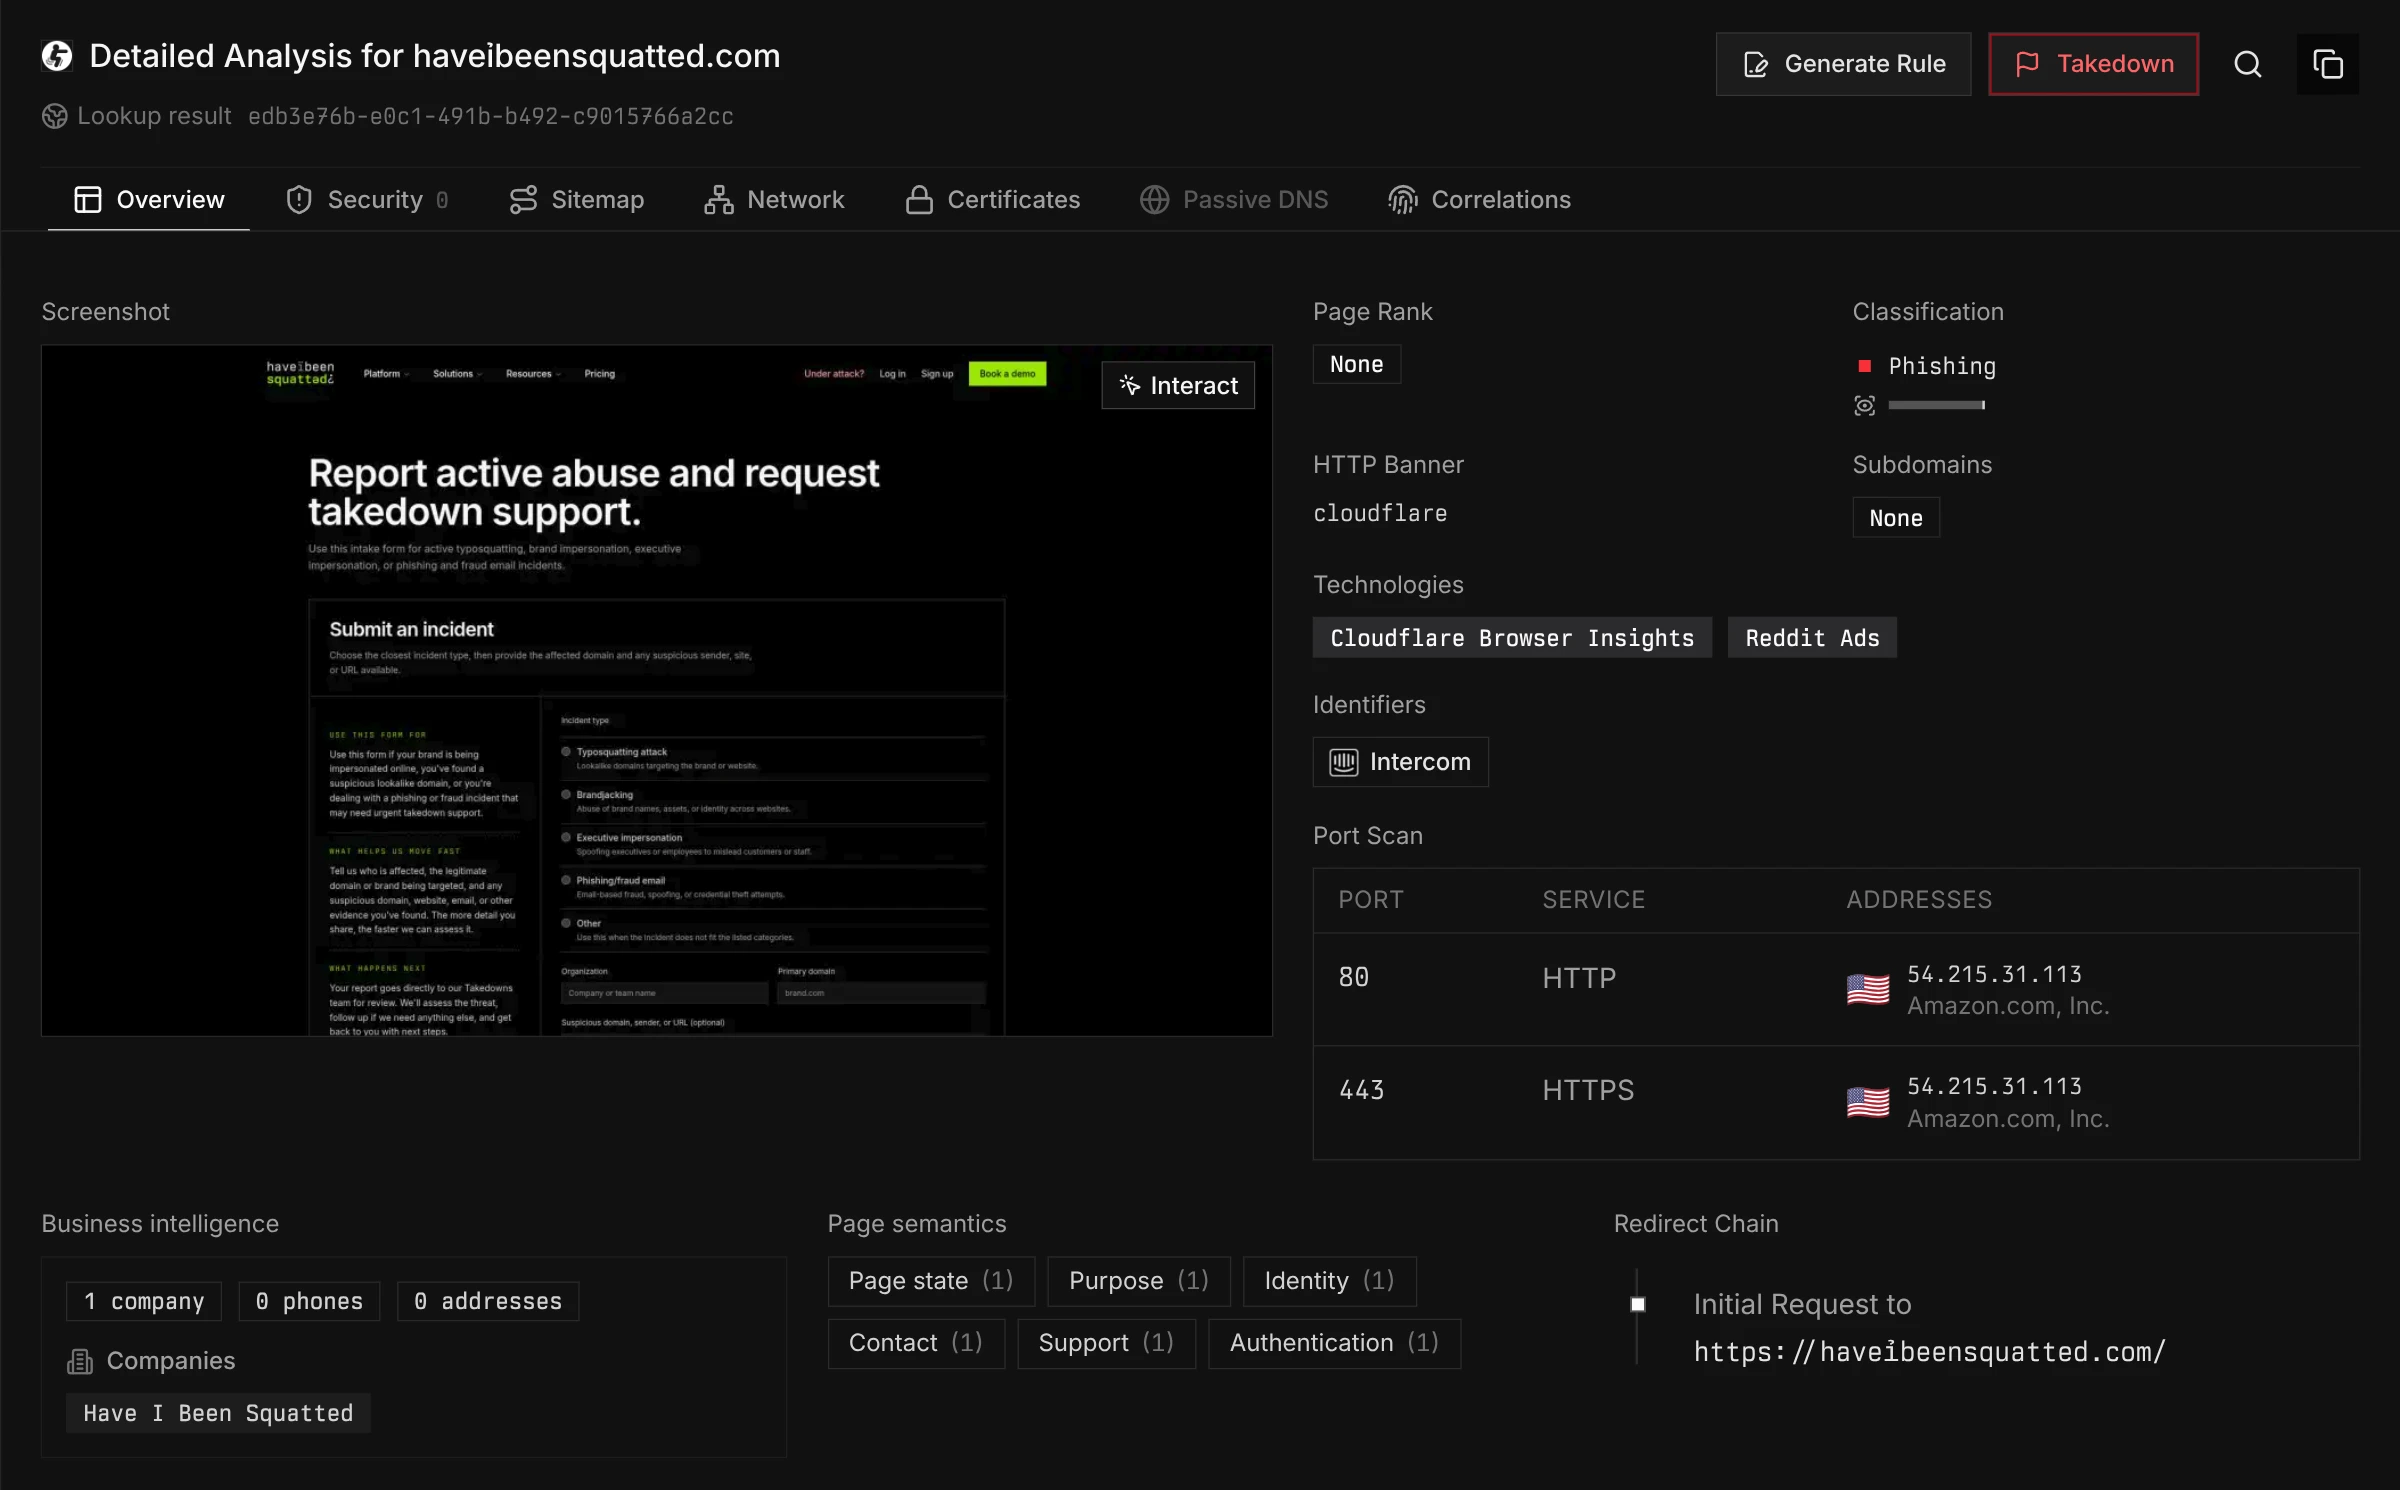
Say a lookalike of your login host appears with a page that looks like yours. In DNSRazzle, a high screenshot-similarity score can put that lookalike into a blocklist file for your own response workflow. In Have I Been Squatted, a domain that matches a configured rule can raise an alert, go to a gateway feed or start a Takedown request. Choose based on whether you want to maintain that response workflow yourself. 2,9,13–20,25
Where DNSRazzle is the better choice#
DNSRazzle fits when cost, control and a focused local workflow matter more than a hosted queue. Choose it when you want to inspect or change the scanner's code and keep its output in your own workflow. It is free and licensed under Apache-2.0. Conference talks from Baxter Healthcare and Health-ISAC show an enterprise team using it for brand impersonation detection. 1–6,50–51
Pick it when you want SSIM scores on viewport screenshots, optional nmap and dnsrecon depth, a blocklist file with a set threshold, or many brands in one local run. It also runs an mx-spy probe that connects to each lookalike's mail server, sends a test message and flags the servers that accept it. The results stay on disk, which suits operators who want local files and already manage scheduling and follow-up. 1–3,7–9,23,28–31
Where Have I Been Squatted is the better choice#
Choose Have I Been Squatted when you want to detect malicious domains and the infrastructure behind them without sending probes to lookalike servers from your own network. The hosted service gathers DNS records, RDAP registration data, hosting, MX records and SMTP banners, open ports, redirects and screenshots for each lookalike, where available. A first-party model labels each result legitimate, parked or phishing. When a lookalike serves a page, an analyst can open it in a live, isolated browser session instead of a local browser. 7–8,10,12–13,21,36,42–44
Discovery and follow-up keep running after the first pass. Domain Monitoring watches each domain you add continuously and adds certificate transparency and newly registered domains to generated permutations. Alert statuses record what your team has already reviewed. Rules from the maintained library, or your own in the Upsilon query language, can notify Slack or a webhook, send the finding to a SIEM, block the domain or request an analyst-reviewed Takedown. 7–8,11–14,19,21–22,25–27
Your own systems add evidence that no name scan sees. Site Canaries flag a copy of your site when one of its pages loads on an unrecognized hostname. Rule-flagged domains can go to Network Enforcement or a hosted domain feed for blocking. Network Intelligence reads Microsoft Defender and Cloudflare Gateway traffic counts, so you can see whether devices on your network connected to a flagged domain. 14–16,52–54
A team that scripts its checks can call the Public API, which streams lookalike, unregistered-name, analysis and certificate transparency search results as NDJSON under scoped API keys, with a Python SDK. Monitoring, hunting tools, rules and alerts are self-serve with a free trial, so a small team can start without installing Python, Playwright and nmap. Takedowns and the blocking, email and SIEM products are added through sales. 7,11,21,35–37,54–56
Have I Been Squatted does not suit a buyer whose decision rests on SSIM screenshot scores, or who wants the scanner and its output to stay on their own host. DNSRazzle does that job for free. A buyer who only needs an occasional check can use the free Analyzer and the ad-hoc Typosquat and Analyze lookups without a subscription. 1–3,5–9,11,35–37,56–57
FAQ#
Only if you build the surrounding system yourself. DNSRazzle runs once per invocation, writes files and can send an optional email report through your own SMTP server. Have I Been Squatted schedules lookups and drives alerts, connector deliveries and Takedown requests from rules. 2,12–14,21–23,25,45
Version 2.0.0 is the final feature release, and later work is limited to bug fixes. Choose DNSRazzle for the checks it runs today. Its pinned dnstwist engine dates from 2020 and has no cyrillic or plural fuzzer. SecurityShrimp names Highlander, a separate commercial product with scheduled scans, as the replacement. This page does not compare Highlander. 1,24,30,33
Sources and corrections
Each numbered marker on this page links to its sources below. Each source shows the date it was last checked. If a fact is wrong or out of date, send a correction. A correction is checked against the source and the page is updated.
- 1.SecurityShrimp (`f8al`). “DNSRazzle README.” Accessed . https://github.com/f8al/DNSrazzle/blob/1cf41837574610d42418fd078c51903b52fb850b/docs/README.md
- 2.SecurityShrimp (`f8al`). “DNSrazzle.py (CLI options, output, blocklist).” Accessed . https://github.com/f8al/DNSrazzle/blob/1cf41837574610d42418fd078c51903b52fb850b/DNSrazzle.py#L54
- 3.SecurityShrimp (`f8al`). “dnsrazzle/BrowserUtil.py.” Accessed . https://github.com/f8al/DNSrazzle/blob/1cf41837574610d42418fd078c51903b52fb850b/dnsrazzle/BrowserUtil.py#L104
- 4.SecurityShrimp (`f8al`). “setup.py.” Accessed . https://github.com/f8al/DNSrazzle/blob/1cf41837574610d42418fd078c51903b52fb850b/setup.py
- 5.GitHub. “GitHub repository metadata.” Accessed . https://api.github.com/repos/f8al/DNSrazzle
- 6.SecurityShrimp / Apache Software Foundation. “Apache License 2.0, full repository license.” Accessed . https://raw.githubusercontent.com/f8al/DNSrazzle/1cf41837574610d42418fd078c51903b52fb850b/LICENSE
- 7.Have I Been Squatted. “Changelog.” Accessed . https://haveibeensquatted.com/changelog
- 8.Have I Been Squatted. “Domain signals.” Accessed . https://docs.haveibeensquatted.com/reference/signals/domain/
- 9.SecurityShrimp (`f8al`). “dnsrazzle/VisionUtil.py.” Accessed . https://github.com/f8al/DNSrazzle/blob/1cf41837574610d42418fd078c51903b52fb850b/dnsrazzle/VisionUtil.py#L65
- 10.Have I Been Squatted. “Homepage (footer tagline).” Accessed . https://haveibeensquatted.com/
- 11.Have I Been Squatted. “Pricing.” Accessed . https://haveibeensquatted.com/pricing
- 12.Have I Been Squatted. “Domain monitoring guide.” Accessed . https://docs.haveibeensquatted.com/features/domain-monitoring/
- 13.Have I Been Squatted. “Rules engine guide.” Accessed . https://docs.haveibeensquatted.com/guides/rules-engine/
- 14.Have I Been Squatted. “Network Intelligence guide.” Accessed . https://docs.haveibeensquatted.com/features/network-intelligence/
- 15.Have I Been Squatted. “Network Enforcement.” Accessed . https://haveibeensquatted.com/platform/network-enforcement
- 16.Have I Been Squatted. “Domain feed integration.” Accessed . https://docs.haveibeensquatted.com/integrations/domain-feed/
- 17.Have I Been Squatted. “CrowdStrike Falcon integration.” Accessed . https://docs.haveibeensquatted.com/integrations/crowdstrike-falcon/
- 18.Have I Been Squatted. “Microsoft Defender for Endpoint integration.” Accessed . https://docs.haveibeensquatted.com/integrations/microsoft-defender-endpoint/
- 19.Have I Been Squatted. “Takedowns.” Accessed . https://haveibeensquatted.com/platform/takedowns
- 20.Have I Been Squatted. “Takedowns guide.” Accessed . https://docs.haveibeensquatted.com/features/takedowns/
- 21.Have I Been Squatted. “Domain Monitoring FAQ.” Accessed . https://haveibeensquatted.com/platform/monitoring
- 22.Have I Been Squatted. “Administration guide.” Accessed . https://docs.haveibeensquatted.com/guides/administration/
- 23.SecurityShrimp (`f8al`). “dnsrazzle/DnsRazzle.py (fuzzing, scanner options, screenshot loop).” Accessed . https://github.com/f8al/DNSrazzle/blob/1cf41837574610d42418fd078c51903b52fb850b/dnsrazzle/DnsRazzle.py#L108
- 24.SecurityShrimp. “Products.” Accessed . https://www.securityshrimp.com/products.html
- 25.Have I Been Squatted. “Integrations.” Accessed . https://haveibeensquatted.com/platform/integrations
- 26.Have I Been Squatted. “Alert digest guide.” Accessed . https://docs.haveibeensquatted.com/guides/digest/
- 27.Have I Been Squatted. “Connectors.” Accessed . https://docs.haveibeensquatted.com/integrations/
- 28.SecurityShrimp (`f8al`). “dnsrazzle/NetUtil.py (RDAP call, nmap, reconDNS).” Accessed . https://github.com/f8al/DNSrazzle/blob/1cf41837574610d42418fd078c51903b52fb850b/dnsrazzle/NetUtil.py#L87
- 29.SecurityShrimp (`f8al`). “dnsrazzle/IOUtil.py (CSV columns).” Accessed . https://github.com/f8al/DNSrazzle/blob/1cf41837574610d42418fd078c51903b52fb850b/dnsrazzle/IOUtil.py#L112
- 30.elceef (Marcin Ulikowski). “dnstwist.py at tag 20201228 (`DomainFuzz`, `DomainThread`).” Accessed . https://github.com/elceef/dnstwist/blob/20201228/dnstwist.py#L506
- 31.SecurityShrimp (`f8al`). “reconDNS `general_enum` (fork of darkoperator/dnsrecon; PyPI `reconDNS` 0.0.3).” Accessed . https://github.com/f8al/dnsrecon/blob/HEAD/recondns/recondns.py#L653
- 32.PyPI. “PyPI JSON API for DNSrazzle.” Accessed . https://pypi.org/pypi/DNSrazzle/json
- 33.SecurityShrimp (`f8al`). “requirements.txt.” Accessed . https://github.com/f8al/DNSrazzle/blob/1cf41837574610d42418fd078c51903b52fb850b/requirements.txt
- 34.SecurityShrimp (`f8al`). “Release v2.0.0 "Culminating Capybara" (all releases via `api.github.com/repos/f8al/DNSrazzle/releases`).” Accessed . https://github.com/f8al/DNSrazzle/releases/tag/v2.0.0
- 35.Have I Been Squatted. “Agents.” Accessed . https://haveibeensquatted.com/platform/agents
- 36.Have I Been Squatted. “Access control reference.” Accessed . https://docs.haveibeensquatted.com/reference/access-control/
- 37.Have I Been Squatted. “MCP server.” Accessed . https://docs.haveibeensquatted.com/ai/mcp/
- 38.Have I Been Squatted. “Passive DNS guide.” Accessed . https://docs.haveibeensquatted.com/features/passive-dns/
- 39.Spamhaus. “Spamhaus passive DNS endpoint, unauthenticated probe.” Accessed . https://beta-pdns.spamhaus.com/api/v3/login
- 40.Have I Been Squatted. “Atlas investigations.” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/
- 41.Have I Been Squatted. “Atlas investigations (add domains and indicators).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#steer-an-investigation
- 42.Have I Been Squatted. “Atlas observations: registration data by TLD.” Accessed . https://mcp.haveibeensquatted.com/mcp
- 43.Have I Been Squatted. “Platform.” Accessed . https://haveibeensquatted.com/platform
- 44.Have I Been Squatted. “Rule field catalog (classification fields).” Accessed .
- 45.SecurityShrimp (`f8al`). “dnsrazzle/MailUtil.py (also `etc/mail_config.conf.sample`).” Accessed . https://github.com/f8al/DNSrazzle/blob/1cf41837574610d42418fd078c51903b52fb850b/dnsrazzle/MailUtil.py#L145
- 46.Have I Been Squatted. “Webhooks.” Accessed . https://docs.haveibeensquatted.com/integrations/webhooks/
- 47.Have I Been Squatted. “Slack app.” Accessed . https://docs.haveibeensquatted.com/ai/slack/
- 48.Have I Been Squatted. “Reports guide.” Accessed . https://docs.haveibeensquatted.com/features/reports/
- 49.Have I Been Squatted. “MCP server (OAuth scopes).” Accessed . https://docs.haveibeensquatted.com/ai/mcp/#oauth-scopes
- 50.InfoconDB. “Detecting Brand Impersonation with Computer Vision and DNSRazzle (Kernelcon 2022).” Accessed . https://infocondb.org/con/kernelcon/kernelcon-2022/detecting-brand-impersonation-with-computer-vision-and-dnsrazzle
- 51.Health-ISAC. “Detecting Brand Impersonation with DNSRazzle and Computer Vision.” Accessed . https://health-isac.org/archive/detecting-brand-impersonation-with-dnsrazzle-and-computer-vision
- 52.Have I Been Squatted. “Site Canaries.” Accessed . https://haveibeensquatted.com/platform/site-canaries
- 53.Have I Been Squatted. “Site Canaries guide.” Accessed . https://docs.haveibeensquatted.com/features/site-canaries/
- 54.Have I Been Squatted. “Network Intelligence.” Accessed . https://haveibeensquatted.com/platform/network-intelligence
- 55.Have I Been Squatted. “API.” Accessed . https://docs.haveibeensquatted.com/guides/api/
- 56.Have I Been Squatted. “API: Analyze a URL.” Accessed . https://docs.haveibeensquatted.com/guides/api/analyze/#analyze-a-url
- 57.Have I Been Squatted. “Tools: Analyze (URL analysis note, served without sign-in).” Accessed . https://haveibeensquatted.com/app/tools?mode=analyze