- Choose Axur for Brand Protection across social profiles, apps, paid search, dark-web channels and credential exposure, with automated notices to hosts, registrars and platforms. 1–11
- Choose Have I Been Squatted to detect malicious domains, including lookalikes from certificate transparency, inspect them in a live, isolated browser session, and block them in Zscaler, Cloudflare Zero Trust or Microsoft Defender for Endpoint. 12–22
- Use both if Axur runs your wider brand and takedown program and your security team also wants domain evidence, rules and gateway response inside its own stack. 1–2,15,19–25
At a glance#
| Have I Been Squatted | Axur | |
|---|---|---|
| What you get | ||
| What you get | Detection and response for malicious domains12 | External threat platform with Brand Protection workspaces1 |
| Lookalike discovery | ||
| Lookalike discovery | Permutations, certificate transparency, newly registered domains, business context13–14 | Smart Monitoring: TLD-squat, homoglyph, typosquat, combosquat26–27 |
| Evidence for investigation | ||
| Evidence for investigation | ||
| Delivery to security tools | ||
| Delivery to security tools | SIEM connectors, Slack, Tines and webhooks28–29 | |
| Blocking | ||
| Blocking | Gateways, endpoints, mail quarantine, hosted domain feed19–22 | Through Infoblox Threat Defense34–35 |
| Managed takedowns | ||
| Managed takedowns | Domains, to host and registrar, with escalation36–39 | |
| Beyond domains | ||
| Beyond domains | Not covered: social, apps, dark web, credentials40–41 | Social, apps, ads, dark web, credentials, executives1–5 |
| How you buy | ||
| How you buy | ||
Coverage beyond lookalike domains#
Axur suits teams that investigate brand abuse across social profiles, apps and paid search as well as domains. Brand Protection covers fake mobile apps, malware, similar domain names, fake social profiles, phishing, branding in paid search and fraudulent trademark use. Other workspaces cover online piracy, data leakage, the deep and dark web, and executives, and Axur also sells Cyber Threat Intel and External Attack Surface Management. 1–5,43
Axur states that Deep and Dark Web monitoring covers more than three thousand channels, including WhatsApp, Telegram and Discord groups. Threat Hunting lets analysts search credentials, cards, URLs and domains in the same data lake, so a leaked password and a phishing domain can sit in one investigation. 1–2,4,44
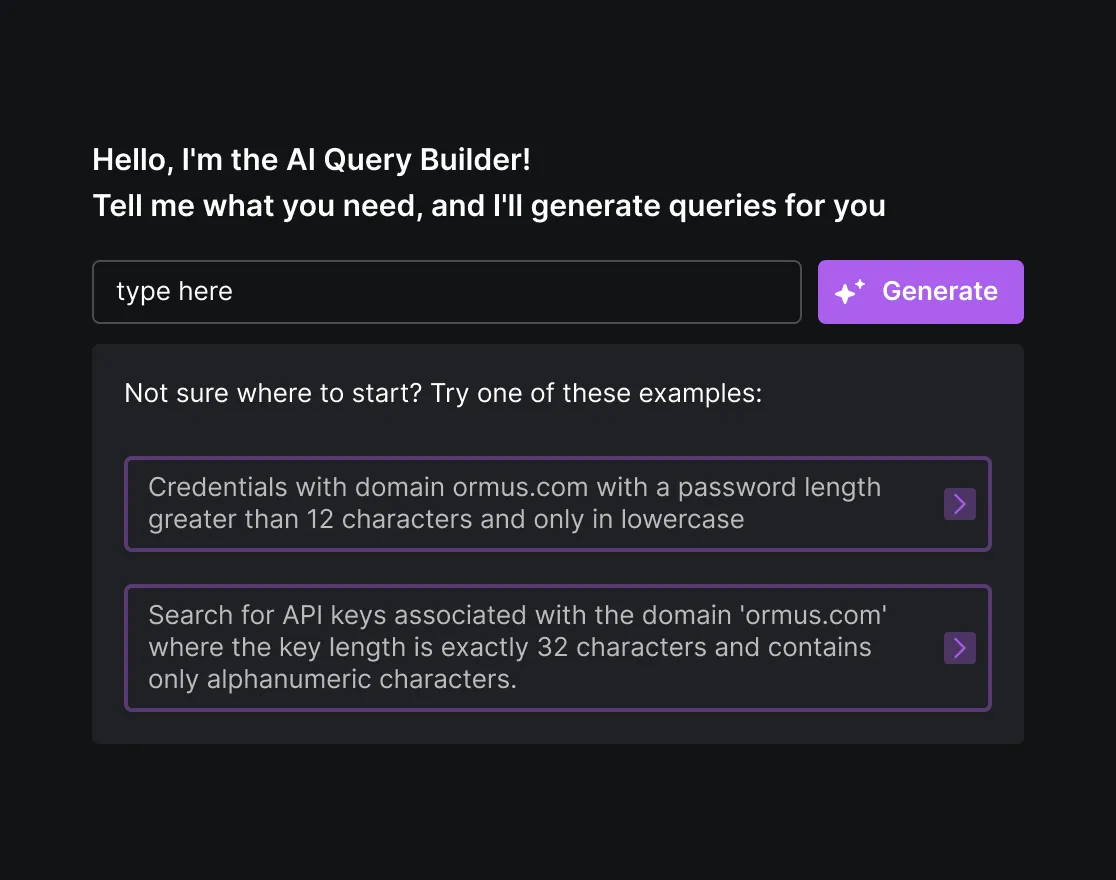
Have I Been Squatted concentrates on domains and the threats built on them. Domain Monitoring generates lookalikes and watches certificate transparency and newly registered domains. Email Intelligence adds mail telemetry from Microsoft 365 and Google Workspace, and Site Canaries flag copies of your own pages. Have I Been Squatted does not monitor social media, app stores, the dark web, ads or leaked credentials. 13–14,39–41,45–47
How each product finds and inspects a lookalike#
Axur's Smart Monitoring of Similar Domains stays active without a manual setup step. The default rule combines TLD-squat and homoglyph matching. Customers can refine Lucene queries for typosquats and combosquats, filter to domains with an active MX record, and simulate the query in Threat Hunting. Axur's help center places subdomain detections, such as a brand label on a hosting subdomain, outside that monitoring. Infoblox now runs this detection in one pipeline with the lookalike detection from Infoblox Threat Defense. 11,26–27,44,48–50
Tickets attach a screenshot, the HTML and a WHOIS file. Similar-domain and phishing tickets also list the hosting provider, ASN, DNS records and SSL certificate details, and analysts can jump from those fields into Threat Hunting. Clair supplies visual fields such as logo detection, brand mismatch, threat category and an AI risk score. 2–5,10–11,49,51–53
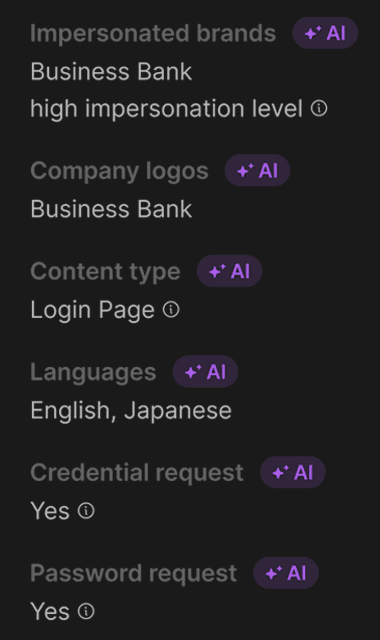
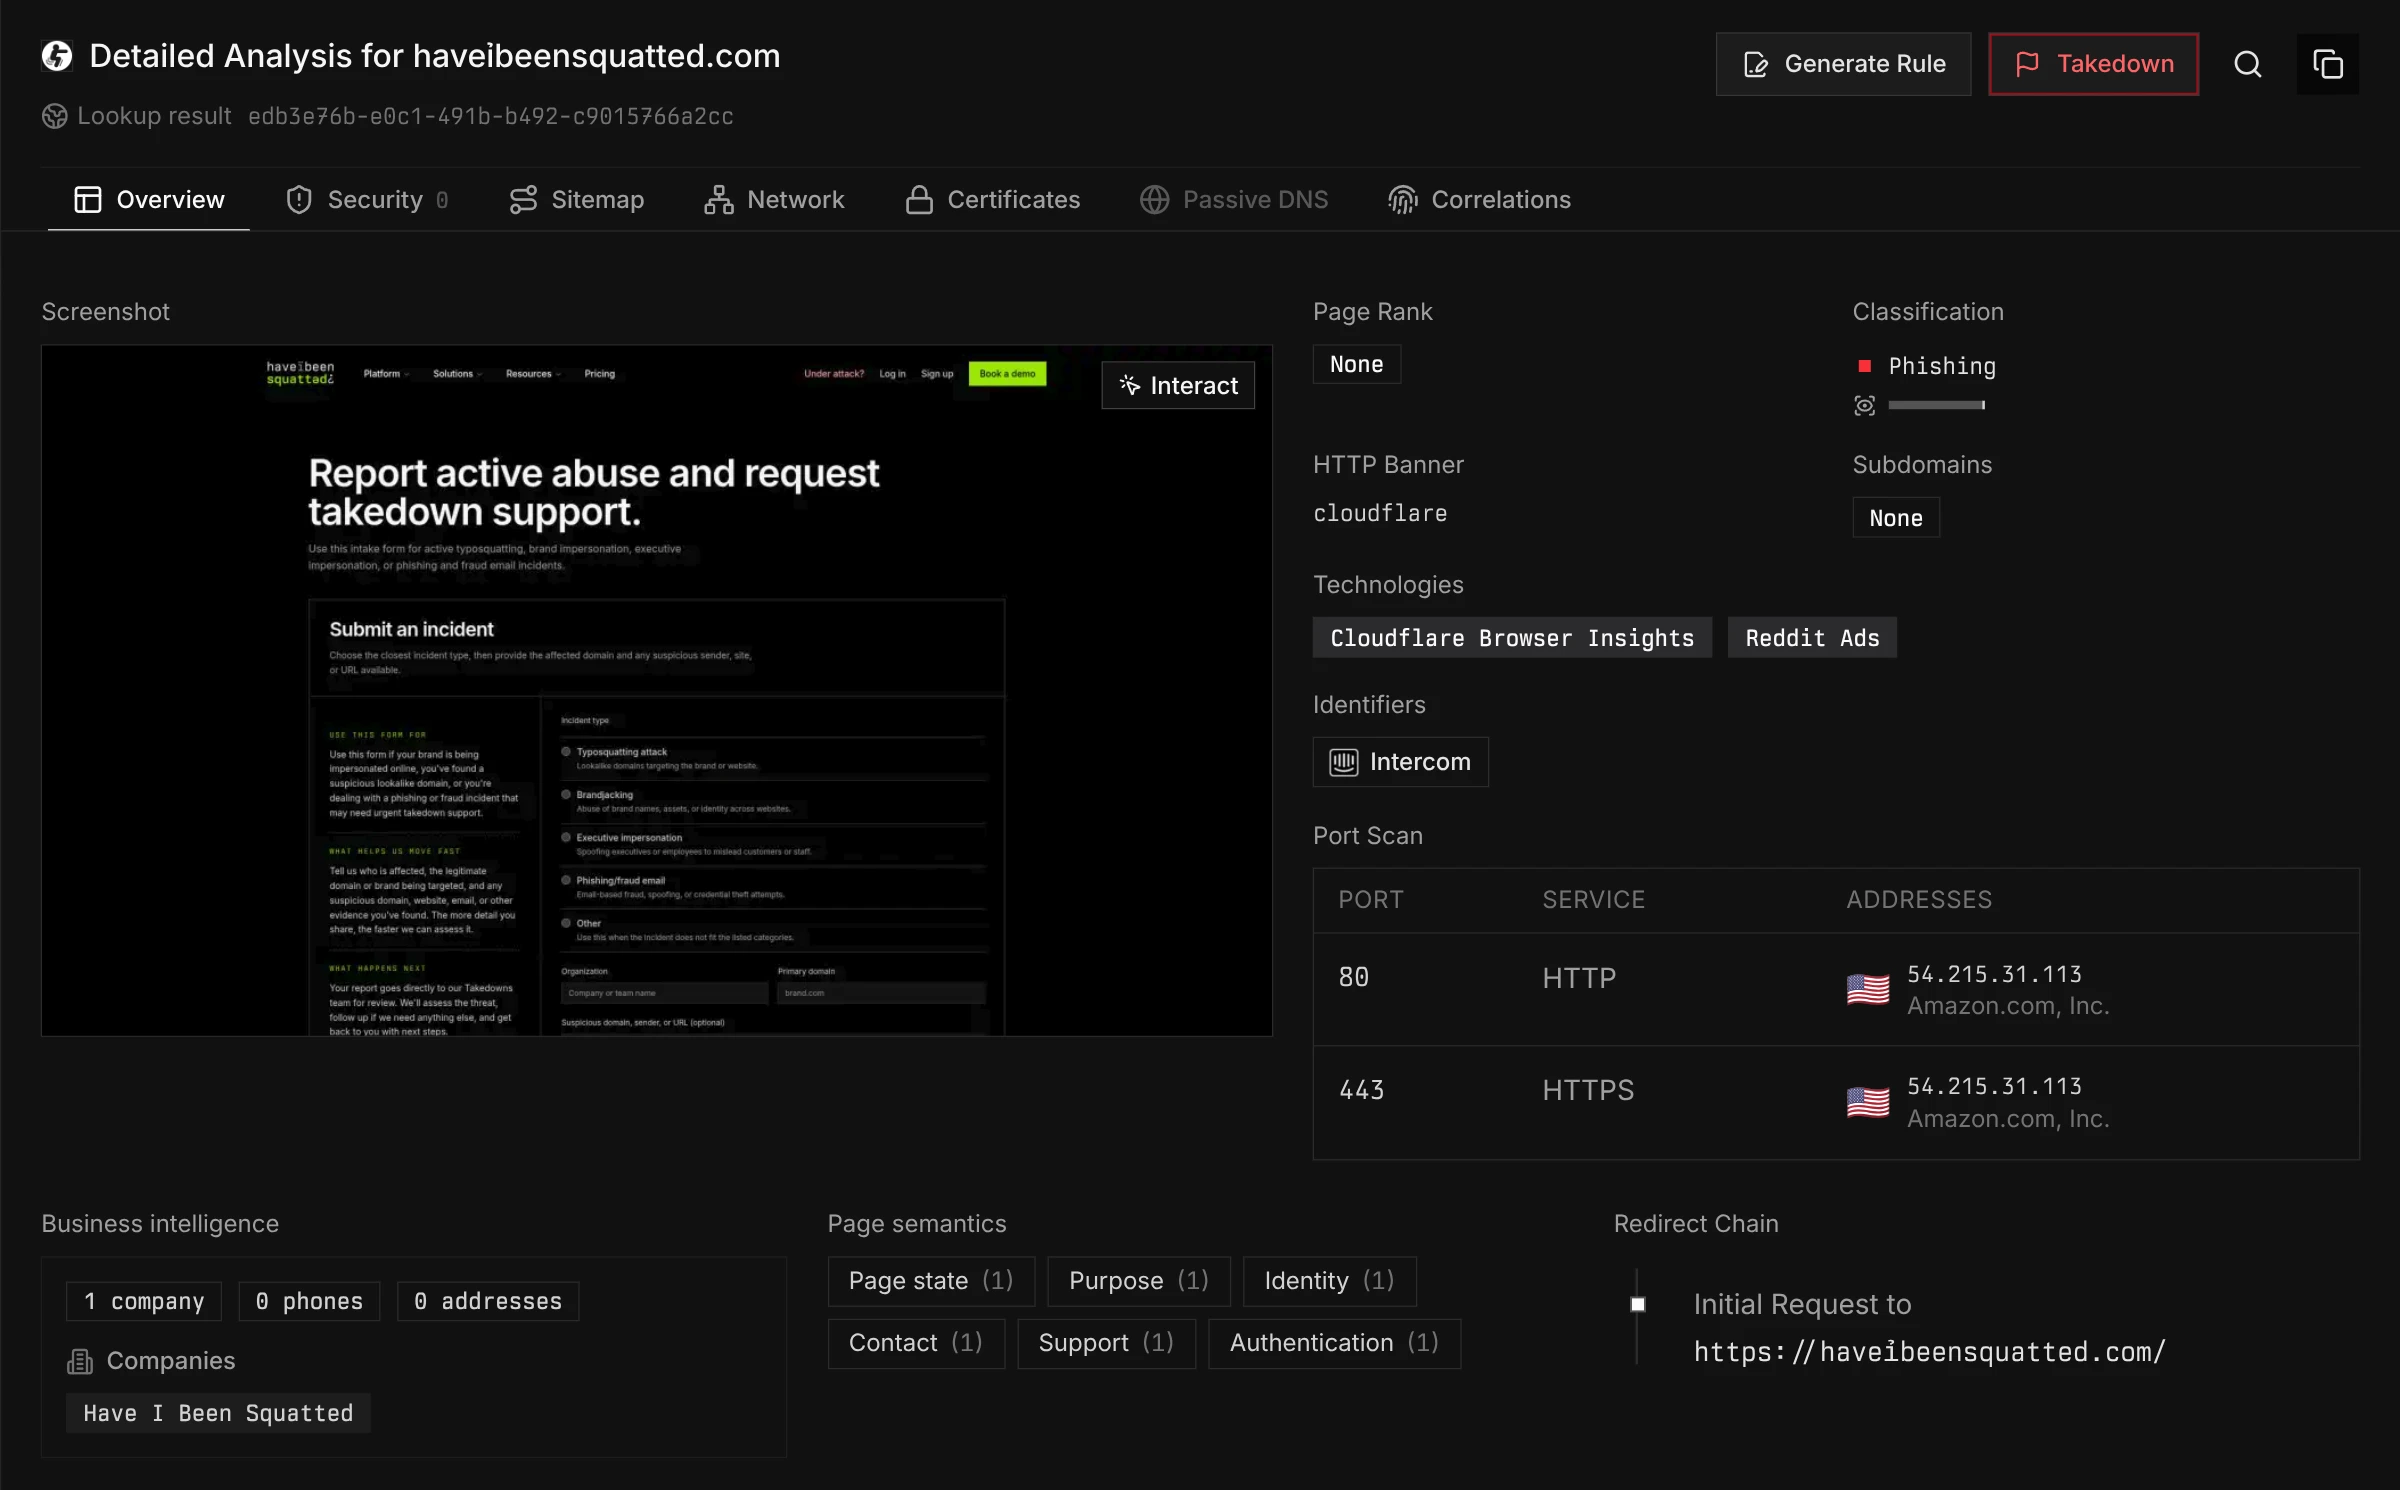
Have I Been Squatted gives your analysts the domain evidence to inspect. Discovery combines generated lookalikes, with named kinds such as homoglyphs, bitsquats and TLD swaps, with certificate transparency and newly registered domains. Results combine RDAP registration data, hosting details, DNS records, mail readiness, open ports and a capture of the website where available. A first-party model classifies each result as legitimate, parked or phishing, with a confidence score, and page semantics record observations such as a request for an account password. An analyst can check whether a lookalike resolves, is set up for email or serves a copied page, then open it in an isolated browser. No public documentation of Axur certificate transparency monitoring was found. 2,5,13–15,17–18,23–24,39,43,54–59
Both products ship a cloned-site script. Axur's OnePixel is a per-customer script with no usage limit that reads the HTTP referer when a copied page loads your site. Have I Been Squatted Site Canaries do the same job with a script matched against hostname patterns, with up to five active deployments per monitored domain. 47,60–61
Either product can carry a lookalike investigation. Choose Axur when visual triage fields and one queue for domain, social and app cases matter most. Choose Have I Been Squatted when you want certificate transparency in discovery, page semantics and isolated browsing behind each domain. 1–5,13–15,17–18,23,52
Following a lookalike to the rest of a campaign#
Axur's Threat Hunting searches its whole data lake, not only your own assets, across credentials, cards, URLs and domains. Axur markets it for pivoting across exposed credentials, cards and phishing indicators at scale, and Infoblox says Digital Risk Protection Services correlates related domains and attacker assets into campaigns. Investigation reports download from the Investigations panel, and Threat Hunting results export to CSV. 1–2,4,11,44,51,62–63
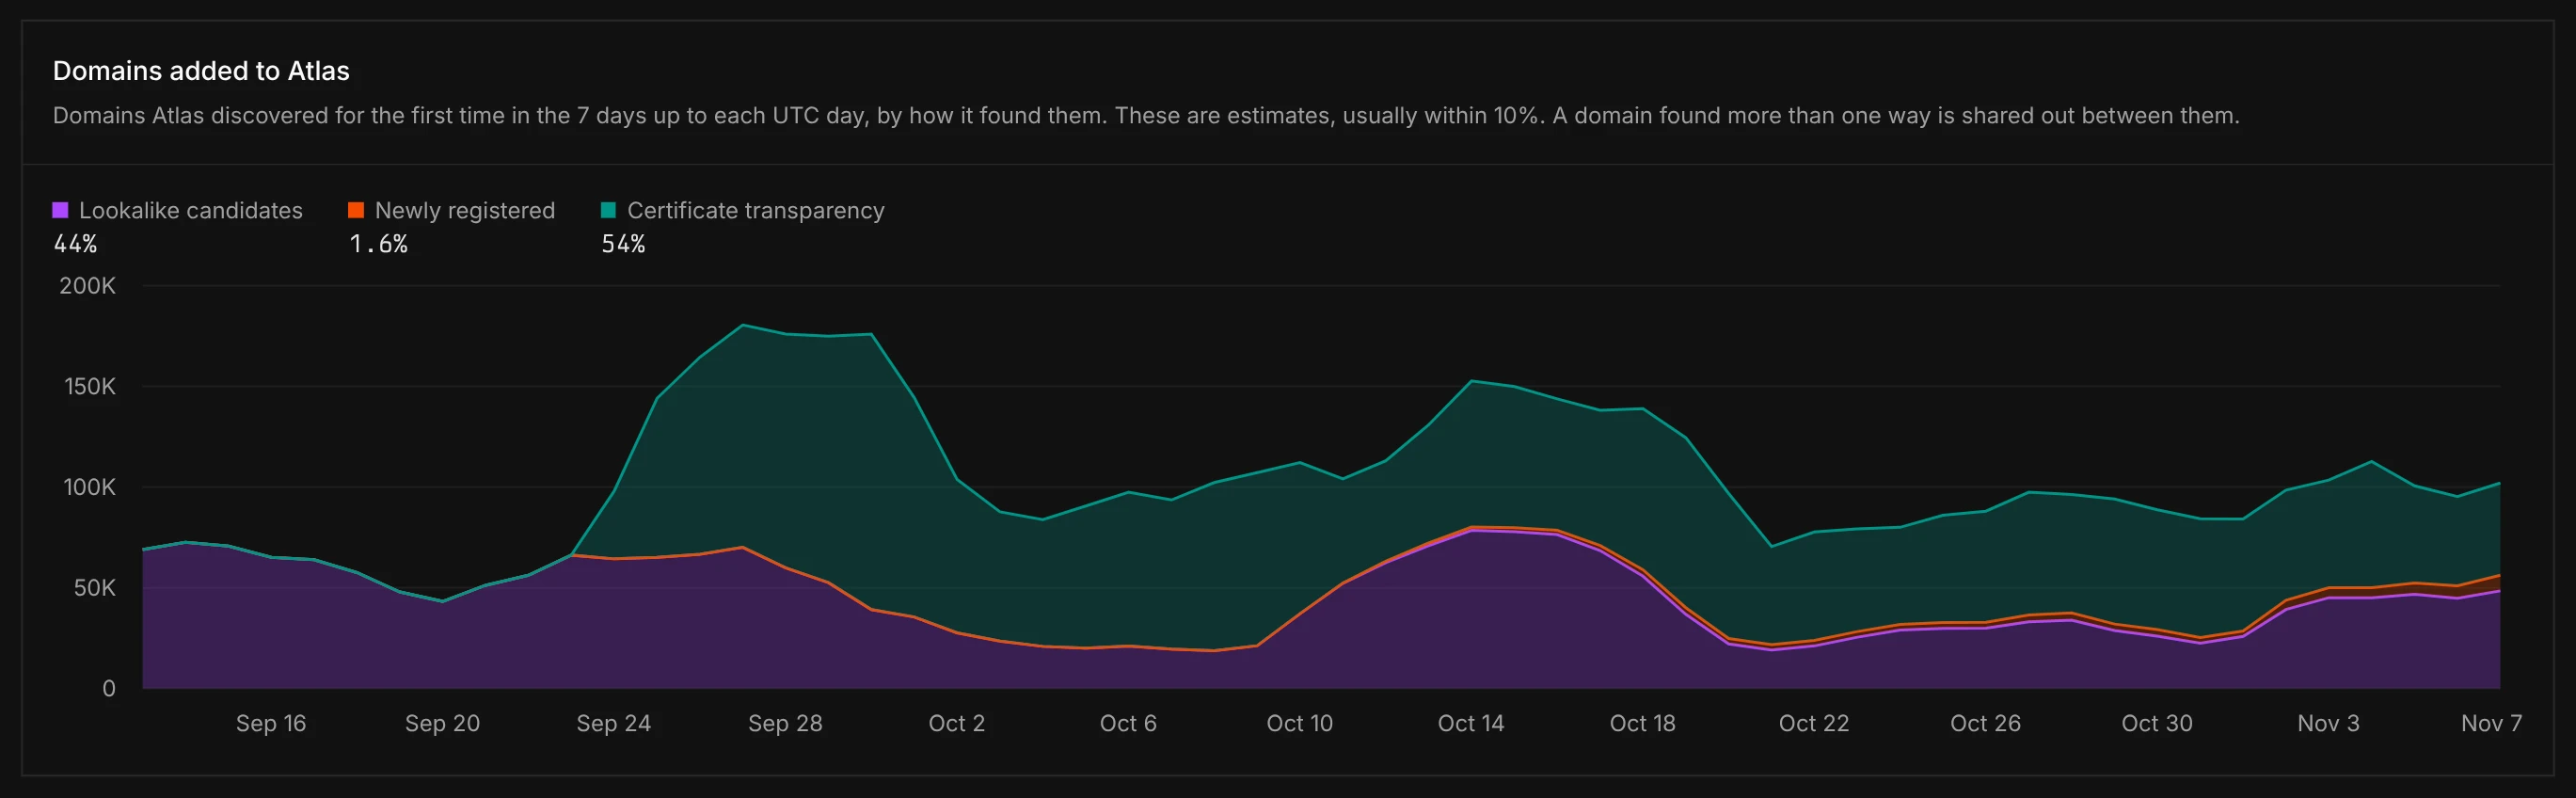
Have I Been Squatted follows the infrastructure with Atlas investigations, which are in early access. An admin describes the hunt and can seed it with lookalike domains already in hand, and Atlas pivots across shared infrastructure in its store of domain observations. Indicators such as IP addresses, nameservers or favicon hashes can be added later for it to pivot on. It keeps watching once the first pass ends and lays the results out in views such as Tree, Table, Clusters and Flows. An investigation exports to STIX 2.1, CSV, JSON or Markdown. No public documentation of a graph view or an infrastructure-pivot API was found for Axur. 4,11,37,51,57–58,64–67
Takedowns
Follow a Takedown from request to outcome.
A demo shows the Takedown case workflow and the Network Enforcement gateways that receive blocks.
Acting on a finding in your own tools#
Axur connects tickets and intelligence into security operations. Named connectors reach SIEM, SOAR, chat and threat-intel tools such as Splunk, Microsoft Sentinel, IBM QRadar, Rapid7 InsightIDR, ServiceNow and MISP, with webhooks signed HMAC-SHA256 and a TAXII collection for IOCs. Infoblox says Digital Risk Protection Services findings can feed Infoblox Threat Defense to block destinations while takedowns run. No public documentation of delivery to third-party gateways such as Zscaler, Cloudflare Gateway or Microsoft Defender was found. Axur also runs MCP servers for Threat Hunting, CTI, Tickets, Customers and EASM, which Axur marks as an experimental release. 2,4,30–35,68–70
Have I Been Squatted puts response in rules that run over domain signals. A maintained rules library covers common detections, and your team can add its own. A rule can raise an alert, deliver the finding to a SIEM, push the domain to a block list, mark the result Malicious with a note or request a Takedown. An analyst or an agent can also send one response for a result immediately, outside any rule. The MCP server covers lookups, monitoring queries, rules, alerts, Takedowns, response dispatch, result annotation and documentation search, and every write needs an organization admin. 15,23–25,28,39,66,71–76
Network Enforcement blocks flagged domains in Zscaler Internet Access, Cloudflare Zero Trust and Microsoft Defender for Endpoint, and adds mail blocks in Microsoft 365 and Cloudflare Email Security. Other tools can poll a hosted domain feed. Findings reach Splunk, Microsoft Sentinel and Google SecOps, or any endpoint through signed webhooks. CrowdStrike Falcon receives domains as detections. 19–22,28–29
No public documentation of an Axur Microsoft 365 or Google Workspace mailbox connector was found. Have I Been Squatted Email Intelligence correlates lookalike senders from those mail systems without changing MX records. 31,33,45–46
Managed takedowns and their targets#
Both products handle takedown requests for you. Axur lets users with the Expert or Manager profile request takedowns in the platform or through its API, and advertises notices that draft, send, read replies and escalate. Only resolved Axur takedowns count against the package, and a recurrence at the same URL and host within fifteen days does not count again. Axur publishes a conditional first-notification SLA when documents comply with platform policies. 1–3,6,10,36–37,51,77–83
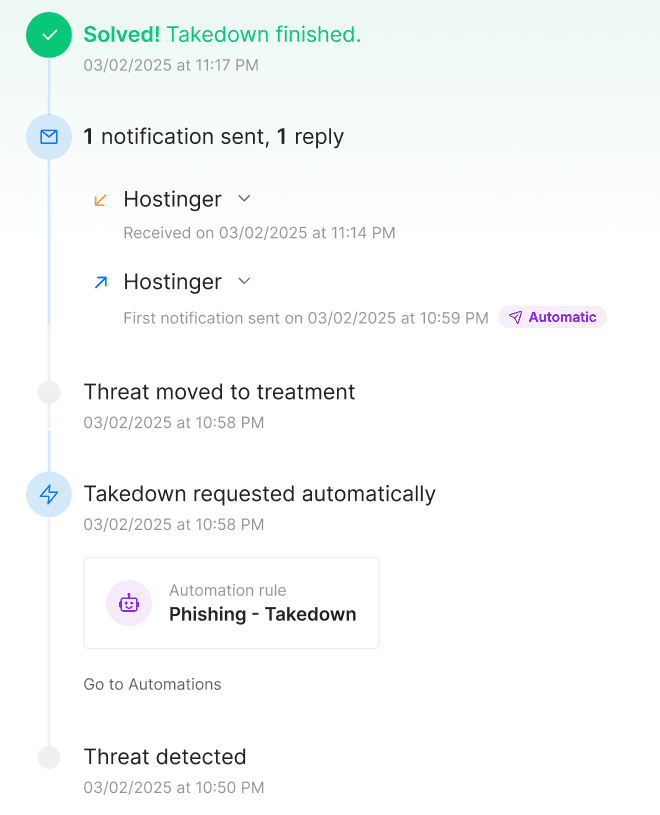
Axur reaches more kinds of target. Automated notifications go to providers, registrars and platforms, including a direct channel to the XYZ domain registry. Spoofing notices go to the registrar and email provider. Executive takedown covers fake social profiles and executive data on lead-sales sites. Web Safe Reporting sends phishing and malware URLs to entities such as Google Safe Browsing and APWG. Axur marketing also names direct channels with Meta and Mercado Livre, and coverage of paid search, social media and app stores. Parked lookalikes without content are not eligible, and Axur does not handle domain disputes or legal action. 1–3,6–11,68,82,84–85
Have I Been Squatted runs managed Takedowns for domains. An analyst reviews every request, and a rule can open a request automatically. The team reports the domain to its host and registrar, then escalates to ICANN and regional CSIRTs where necessary. The service stops short of legal action and can introduce legal partners. 36–39
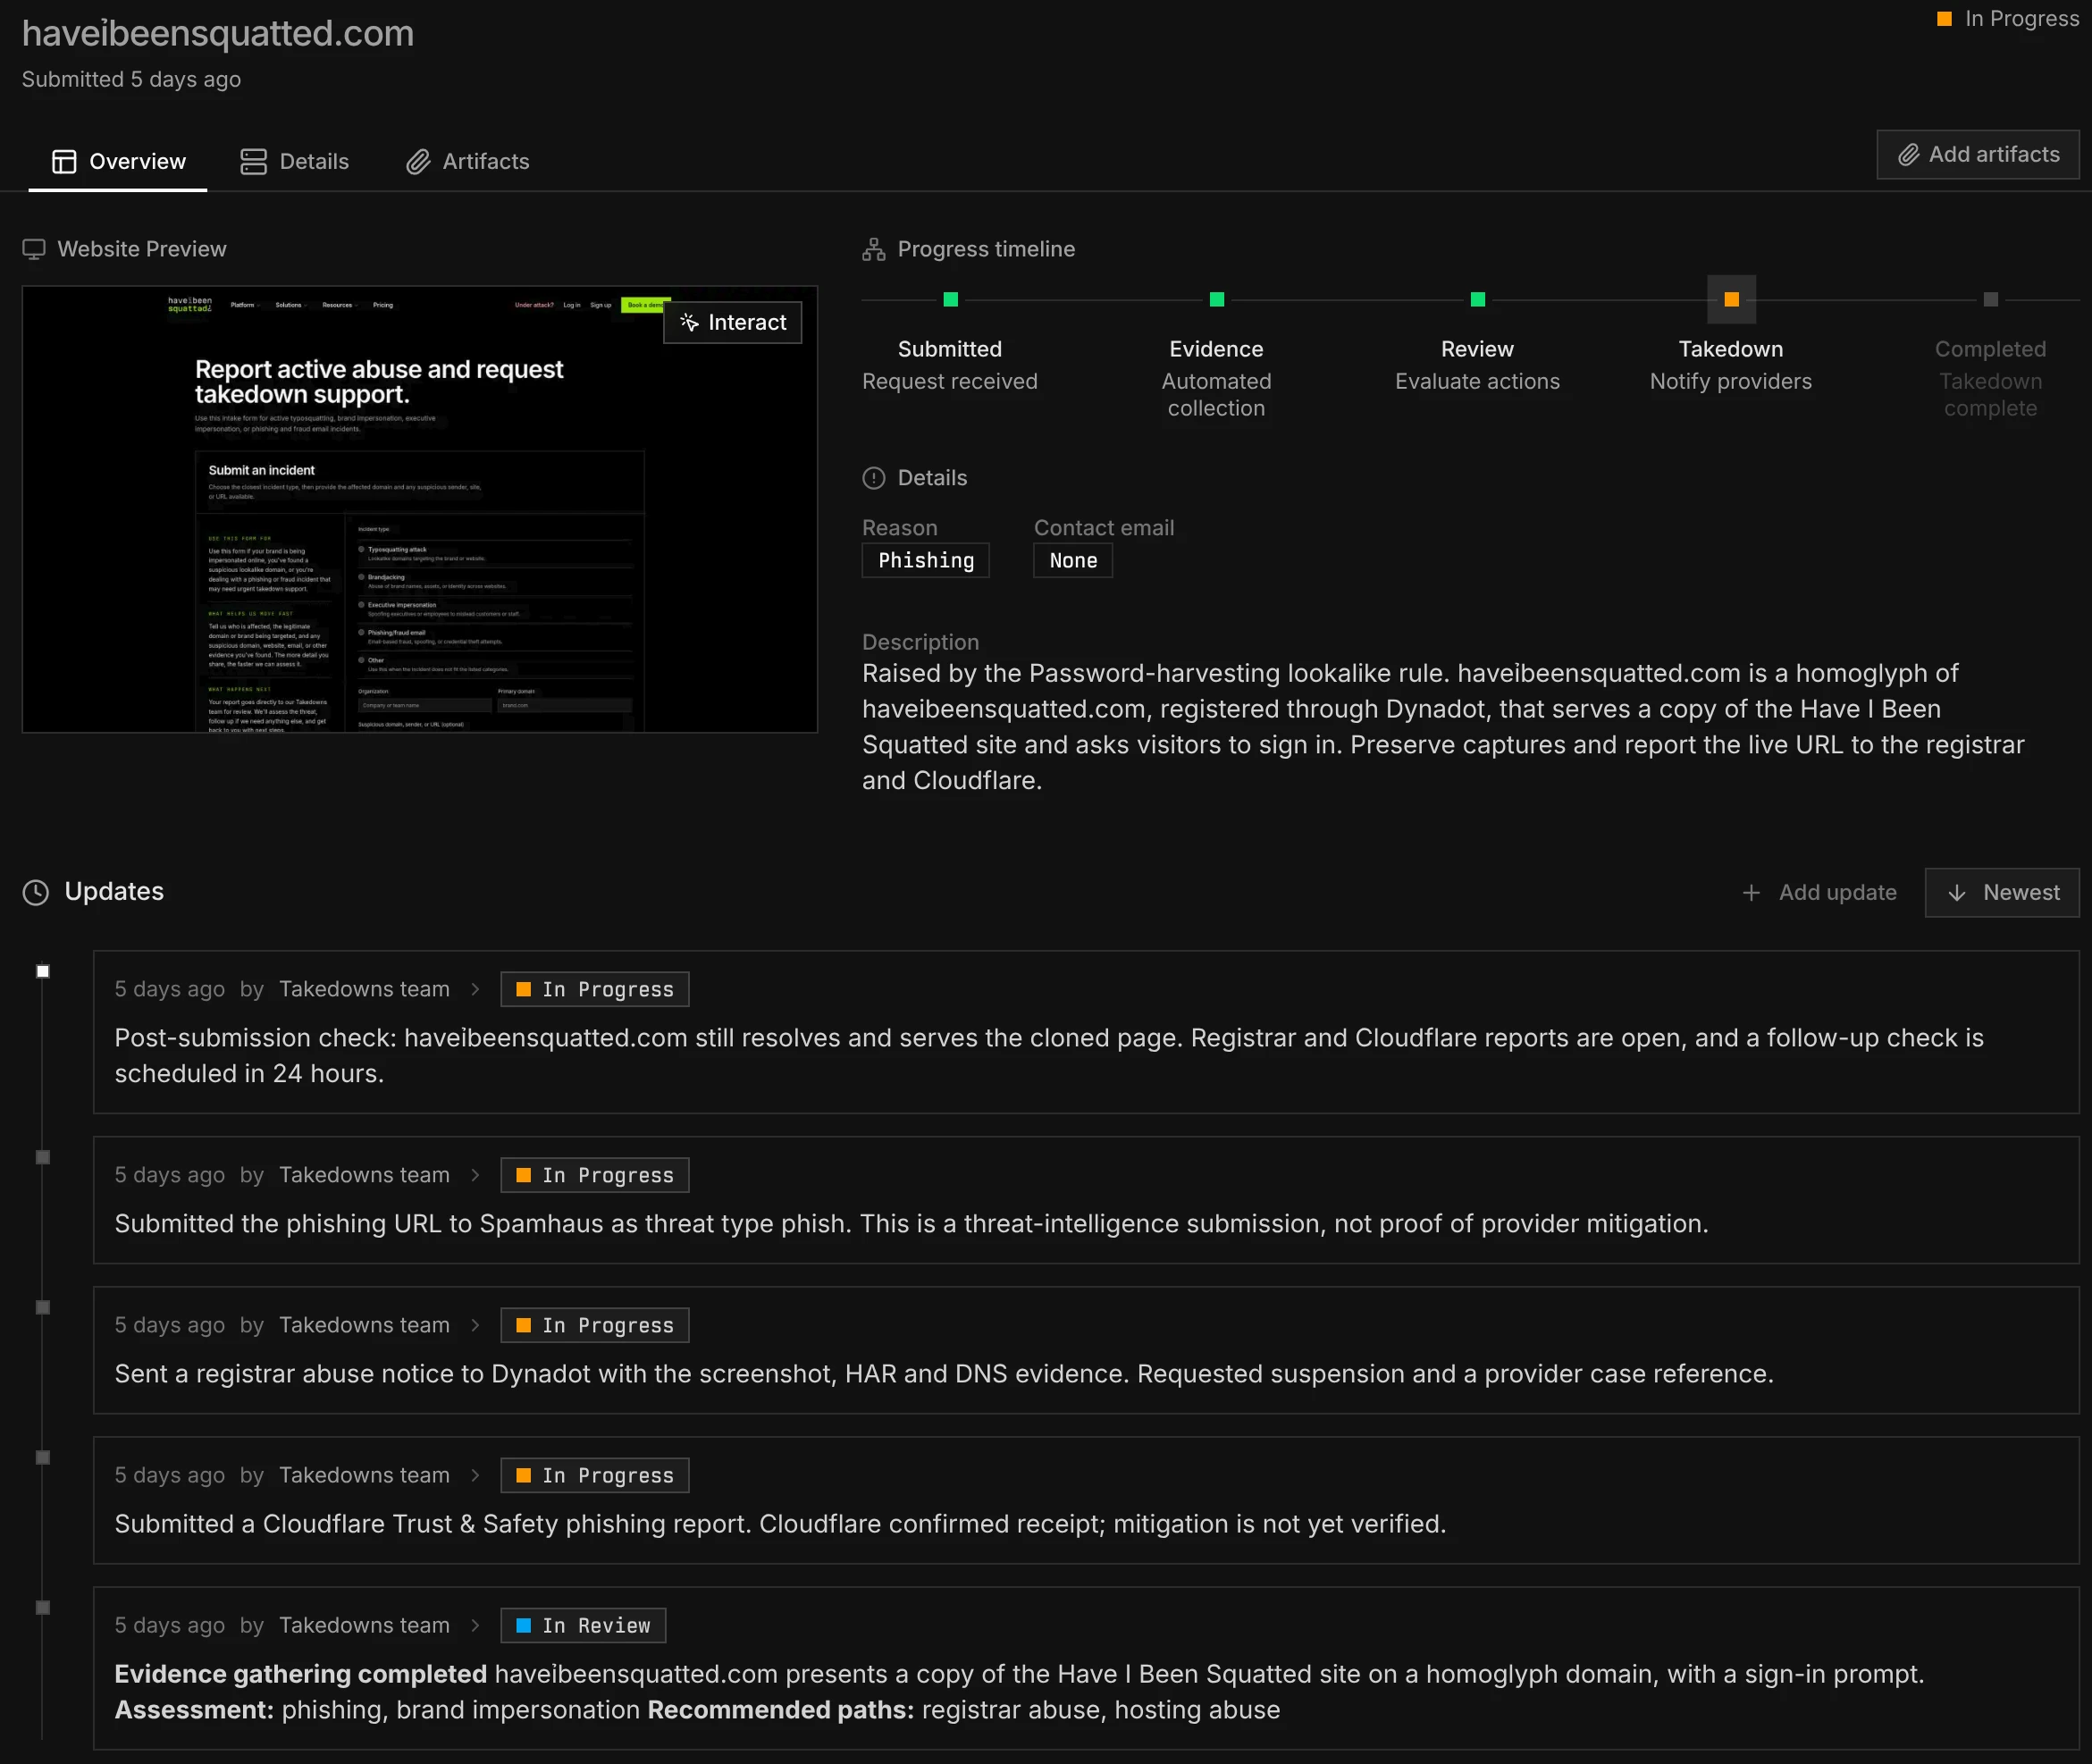
Both products can connect detections to takedown requests. Choose Axur for its wider target coverage, automated notice handling and browser-blocklist reporting. Choose Have I Been Squatted when you want analyst-reviewed domain Takedowns beside its domain evidence and Network Enforcement. If you run both, decide which product owns domain triage and takedown requests. 1–3,6–11,15,19–23,36–37,68,77
Where Axur is the better choice#
Axur fits when digital risk spans channels that a domain product does not cover, such as social impersonation, fake apps, paid-search abuse, dark-web collection, credential and card exposure, executive protection and online piracy. It also suits teams that want managed triage through SmartHunt and analyst help from the Axur Research Team. Managed security providers can manage customer tenants and credit limits through the Customers API, with four access profiles separating viewers from people who request takedowns. 1–7,10,77,86
Axur suits buyers who want takedowns billed only when content is removed, with a published first-notification SLA. Web Safe Reporting reaches browser and antivirus entities, and Infoblox Threat Defense can block destinations while work proceeds. Buying starts with a platform demo and a quote. 1,9–10,34–35,68,80,87
Where Have I Been Squatted is the better choice#
Have I Been Squatted fits a security team that works malicious domains and the attacker infrastructure behind them, and wants each one blocked in its own controls while removal runs. Network Enforcement pushes rule-flagged domains into Zscaler Internet Access, Cloudflare Zero Trust, iboss and Microsoft Defender for Endpoint, and adds mail blocks in Microsoft 365 and Cloudflare Email Security. Tools that poll a list can read a hosted domain feed in seven formats, among them STIX 2.1 and CSV, with documented MISP setup. Network Intelligence then shows whether devices on your network connected to the domain. 12,19–22,25,88
Each domain also gets a closer look. Domain Monitoring checks your domains continuously and adds certificate transparency and newly registered domains to the lookalikes it generates, and Analyze inspects any other domain on demand. When a domain serves a page, an analyst can open it in a live, isolated browser session. Email Intelligence correlates Microsoft 365 and Google Workspace mail telemetry, including sender and URL domains, with the domains you monitor. Managed Takedowns cover takedown and disruption of malicious infrastructure, starting with reports to the host and registrar. 13–15,17–18,36–39,45–46,73–74,89–90
You can start on your own. Monitoring, hunting tools, rules and alerts are self-serve with a free trial, and Takedowns and the email, network, SIEM and canary products are bought through sales. Results leave as a PDF "Domain security overview" or "Compliance readout", or as CSV and JSON exports. For a security review, Have I Been Squatted has a SOC 2 Type II report, available through its Trust Center, and supports single sign-on and audit logging. End users can add free Browser Protection for Chrome. 13,18,24,37,39,57,66–67,73–74,88,91–93
Have I Been Squatted does not suit a buyer who needs social media, app stores, the dark web, ads or leaked credentials monitored alongside domains. Axur covers those channels in one platform. 1–5,40–41
FAQ#
It can, if similar-domain monitoring inside a wider brand program covers what you need. Axur offers Smart Monitoring of similar domains inside Brand Protection, with ticket evidence and visual AI fields for triage. Compare that workflow with Have I Been Squatted's domain rules, enrichment and connector actions to decide which fits how your team works. 2–3,5,15,19–27,52
Yes. Axur requests takedowns from the platform or API, advertises automated notice handling, and also reaches targets beyond domains and browser and antivirus blocklists. Have I Been Squatted runs managed Takedowns with analyst review on every request and reports domains to their hosts and registrars. 1–3,6–11,36–39,51,68,77–79
Choose Have I Been Squatted if your team wants to start with a self-serve trial and run domain investigations and rules itself. Consider Axur if multi-channel Brand Protection, automated takedowns and optional managed triage matter more than self-serve buying, especially when your remit reaches past domains. 1–5,10,13,15,23–25,39,77
Sources and corrections
Each numbered marker on this page links to its sources below. Each source shows the date it was last checked. If a fact is wrong or out of date, send a correction. A correction is checked against the source and the page is updated.
- 1.Axur. “Technical Information (workspaces).” Accessed . https://www.axur.com/en-us/technical-information
- 2.Axur. “Axur Platform API (ticket types).” Accessed . https://docs.axur.com/en/axur/api/openapi-axur.yaml
- 3.Axur. “Brand Protection (FAQ, coverage).” Accessed . https://www.axur.com/en-us/brand-protection
- 4.Axur. “Threat Hunting.” Accessed . https://www.axur.com/en-us/threat-hunting
- 5.Axur. “URL & Domains parameters (ports, WHOIS, ads).” Accessed .
- 6.Axur. “What is Takedown? (notification targets).” Accessed . https://help.axur.com/en/articles/8054880-what-is-takedown
- 7.Axur. “Fraudulent Emails (Spoofing) (2025-12-15).” Accessed . https://help.axur.com/en/articles/8959480-fraudulent-emails-spoofing
- 8.Axur. “How is a Takedown counted? (2025-12-15).” Accessed . https://help.axur.com/en/articles/8055400-how-is-a-takedown-counted
- 9.Axur. “Web Safe Reporting (entities).” Accessed .
- 10.Axur. “Takedown (FAQ, platforms).” Accessed . https://www.axur.com/en-us/takedown
- 11.Infoblox. “What's New in Infoblox Exposure Management (2026-10-22 entry, XYZ registry channel).” Accessed . https://docs.infoblox.com/space/IEM/2652602612/What%E2%80%99s+New+in+Infoblox+Exposure+Management
- 12.Have I Been Squatted. “Homepage (footer tagline).” Accessed . https://haveibeensquatted.com/
- 13.Have I Been Squatted. “Domain Monitoring.” Accessed . https://haveibeensquatted.com/platform/monitoring
- 14.Have I Been Squatted. “Domain monitoring guide.” Accessed . https://docs.haveibeensquatted.com/features/domain-monitoring/
- 15.Have I Been Squatted. “Changelog.” Accessed . https://haveibeensquatted.com/changelog
- 16.Have I Been Squatted. “certgrep guide.” Accessed . https://docs.haveibeensquatted.com/certgrep/guide/
- 17.Have I Been Squatted. “Platform.” Accessed . https://haveibeensquatted.com/platform
- 18.Have I Been Squatted. “Access control reference.” Accessed . https://docs.haveibeensquatted.com/reference/access-control/
- 19.Have I Been Squatted. “Network Enforcement.” Accessed . https://haveibeensquatted.com/platform/network-enforcement
- 20.Have I Been Squatted. “Domain feed integration.” Accessed . https://docs.haveibeensquatted.com/integrations/domain-feed/
- 21.Have I Been Squatted. “CrowdStrike Falcon integration.” Accessed . https://docs.haveibeensquatted.com/integrations/crowdstrike-falcon/
- 22.Have I Been Squatted. “Microsoft Defender for Endpoint integration.” Accessed . https://docs.haveibeensquatted.com/integrations/microsoft-defender-endpoint/
- 23.Have I Been Squatted. “Domain signals.” Accessed . https://docs.haveibeensquatted.com/reference/signals/domain/
- 24.Have I Been Squatted. “Rules engine guide.” Accessed . https://docs.haveibeensquatted.com/guides/rules-engine/
- 25.Have I Been Squatted. “Network Intelligence guide.” Accessed . https://docs.haveibeensquatted.com/features/network-intelligence/
- 26.Axur. “Smart Monitoring of Similar Domains.” Accessed . https://help.axur.com/en/articles/11566976-smart-monitoring-of-similar-domains
- 27.Axur. “Hunting Like a Pro: Searches for Similar Domain Names.” Accessed . https://help.axur.com/en/articles/11785520-hunting-like-a-pro-searches-for-similar-domain-names
- 28.Have I Been Squatted. “Integrations.” Accessed . https://haveibeensquatted.com/platform/integrations
- 29.Have I Been Squatted. “Webhooks.” Accessed . https://docs.haveibeensquatted.com/integrations/webhooks/
- 30.Axur. “Feeds.” Accessed . https://help.axur.com/en/articles/9981895-feeds
- 31.Axur. “API & Integrations.” Accessed . https://www.axur.com/en-us/api-integrations
- 32.Axur / Infoblox. “Infoblox, Axur Slack Integration Guide.” Accessed . https://help.axur.com/en/articles/15859084-infoblox-axur-slack-integration-guide
- 33.Axur. “Help center: Settings collection (integration guides).” Accessed . https://help.axur.com/en/collections/4062925-settings
- 34.Axur / Infoblox. “Infoblox Completes Axur Acquisition (Threat Defense).” Accessed . https://www.axur.com/en-us/infoblox-completes-axur-acquisition-preemptive-security-external-threats
- 35.Infoblox. “Infoblox Exposure Management: DRPS and EASM, Customer FAQs (2026-05-05).” Accessed . https://www.infoblox.com/resources/faqs/infoblox-exposure-management-digital-risk-protection-services-and-external-attack-surface-management/
- 36.Have I Been Squatted. “Takedowns.” Accessed . https://haveibeensquatted.com/platform/takedowns
- 37.Have I Been Squatted. “Takedowns guide.” Accessed . https://docs.haveibeensquatted.com/features/takedowns/
- 38.Have I Been Squatted. “FAQ (stalled takedowns).” Accessed . https://haveibeensquatted.com/faq#takedowns-stall
- 39.Have I Been Squatted. “Pricing FAQ (takedowns).” Accessed . https://haveibeensquatted.com/pricing
- 40.Have I Been Squatted. “Solutions.” Accessed . https://haveibeensquatted.com/solutions
- 41.Have I Been Squatted. “Brand protection.” Accessed . https://haveibeensquatted.com/solutions/brand-protection
- 42.Axur. “Plan & Usage.” Accessed . https://help.axur.com/en/articles/7967883-plan-usage
- 43.Axur. “External Attack Surface Management.” Accessed . https://www.axur.com/en-us/easm
- 44.Axur. “What is Threat Hunting? (2026-05-22).” Accessed . https://help.axur.com/en/articles/10542636-what-is-threat-hunting
- 45.Have I Been Squatted. “Email Intelligence guide.” Accessed . https://docs.haveibeensquatted.com/features/email-intelligence/
- 46.Have I Been Squatted. “Email Intelligence.” Accessed . https://haveibeensquatted.com/platform/email-intelligence
- 47.Have I Been Squatted. “Site Canaries guide.” Accessed . https://docs.haveibeensquatted.com/features/site-canaries/
- 48.Axur. “Smart Monitoring (default rule).” Accessed .
- 49.Axur. “Hunting Like a Pro (typosquat limit).” Accessed .
- 50.Axur. “Possible learnings after a targeted attack attempt (Domain Watchdog).” Accessed . https://blog.axur.com/en-us/possible-learnings-after-a-targeted-attack-attempt
- 51.Infoblox. “Infoblox Exposure Management FAQs (DRPS).” Accessed .
- 52.Axur. “URL & Domains search parameters (2026-08-19).” Accessed . https://help.axur.com/en/articles/10545862-what-are-the-url-domains-search-parameters-of-threat-hunting
- 53.Axur. “Risk Score: Understanding and Using Threat Prioritization (2026-08-19).” Accessed . https://help.axur.com/en/articles/16165330-risk-score-understanding-and-using-threat-prioritization
- 54.Have I Been Squatted. “Atlas observations: registration data by TLD.” Accessed . https://mcp.haveibeensquatted.com/mcp
- 55.Have I Been Squatted. “Passive DNS guide.” Accessed . https://docs.haveibeensquatted.com/features/passive-dns/
- 56.Spamhaus. “Spamhaus passive DNS endpoint, unauthenticated probe.” Accessed . https://beta-pdns.spamhaus.com/api/v3/login
- 57.Have I Been Squatted. “Atlas investigations.” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/
- 58.Have I Been Squatted. “Atlas investigations (add domains and indicators).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#steer-an-investigation
- 59.Have I Been Squatted. “Rule field catalog (classification fields).” Accessed .
- 60.Axur. “OnePixel: how to set up.” Accessed . https://help.axur.com/en/articles/7981093-onepixel-how-to-set-up
- 61.Axur. “OnePixel (script).” Accessed .
- 62.Axur. “What is Threat Hunting? (limits, export).” Accessed .
- 63.Axur. “Work lists and Export.” Accessed . https://help.axur.com/en/articles/7967405-work-lists-and-export
- 64.Have I Been Squatted. “Atlas investigations (shareable view links).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#read-the-map
- 65.Have I Been Squatted. “Atlas investigations (New investigation flow).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#start-an-investigation
- 66.Have I Been Squatted. “Reports guide.” Accessed . https://docs.haveibeensquatted.com/features/reports/
- 67.Have I Been Squatted. “Explore guide.” Accessed . https://docs.haveibeensquatted.com/features/explore/
- 68.Axur. “Web Safe Reporting (2026-09-11).” Accessed . https://help.axur.com/en/articles/16923495-web-safe-reporting
- 69.Axur. “How to configure Axur MCP in AI clients.” Accessed . https://help.axur.com/en/articles/16299920-how-to-configure-axur-mcp-in-ai-clients-claude-chatgpt-and-gemini
- 70.Axur. “Axur MCP.” Accessed . https://mcp.axur.ai/
- 71.Have I Been Squatted. “Alert digest guide.” Accessed . https://docs.haveibeensquatted.com/guides/digest/
- 72.Have I Been Squatted. “Connectors.” Accessed . https://docs.haveibeensquatted.com/integrations/
- 73.Have I Been Squatted. “MCP server (Responses).” Accessed . https://docs.haveibeensquatted.com/ai/mcp/
- 74.Have I Been Squatted. “Agents.” Accessed . https://haveibeensquatted.com/platform/agents
- 75.Have I Been Squatted. “Slack app.” Accessed . https://docs.haveibeensquatted.com/ai/slack/
- 76.Have I Been Squatted. “MCP server (OAuth scopes).” Accessed . https://docs.haveibeensquatted.com/ai/mcp/#oauth-scopes
- 77.Axur. “User Profiles.” Accessed . https://help.axur.com/en/articles/7967787-user-profiles
- 78.Axur. “Fraudulent Emails (Spoofing) (follow-up).” Accessed .
- 79.Axur. “Takedown Authorization Document (2026-04-01).” Accessed . https://help.axur.com/en/articles/8058239-takedown-authorization-document-and-other-documents-required-for-takedown
- 80.Axur. “How is a Takedown counted? (re-up).” Accessed .
- 81.Axur. “How Takedown works (2026-01-30).” Accessed . https://help.axur.com/en/articles/9345675-how-takedown-works-the-role-of-entities-and-the-time-it-takes-to-resolve-an-incident
- 82.Axur. “What is Takedown? (resolution rate).” Accessed .
- 83.Axur. “Credit Usage (credits table).” Accessed .
- 84.Axur. “Content not eligible for Takedown (2026-03-31).” Accessed . https://help.axur.com/en/articles/14362781-content-not-eligible-for-takedown
- 85.Axur. “Content not eligible (disputes).” Accessed .
- 86.Axur. “MSSP Program.” Accessed . https://www.axur.com/en-us/mssp-program
- 87.Axur. “Home.” Accessed . https://www.axur.com/en-us/
- 88.Have I Been Squatted. “Network Intelligence.” Accessed . https://haveibeensquatted.com/platform/network-intelligence
- 89.Have I Been Squatted. “API: Analyze a URL.” Accessed . https://docs.haveibeensquatted.com/guides/api/analyze/#analyze-a-url
- 90.Have I Been Squatted. “Tools: Analyze (URL analysis note, served without sign-in).” Accessed . https://haveibeensquatted.com/app/tools?mode=analyze
- 91.Have I Been Squatted. “Security.” Accessed . https://haveibeensquatted.com/about/security
- 92.Have I Been Squatted. “Administration guide.” Accessed . https://docs.haveibeensquatted.com/guides/administration/
- 93.Have I Been Squatted. “Browser Protection.” Accessed . https://docs.haveibeensquatted.com/browser-protection/
- 94.Infoblox. “Infoblox ... Planned Acquisition of Axur (GlobeNewswire).” Accessed . https://stocks.observer-reporter.com/observerreporter/article/gnwcq-2026-1-14-infoblox-expands-its-preemptive-security-offering-to-combat-brand-abuse-credential-exposure-and-external-threats-with-planned-acquisition-of-axur
- 95.IT Brief UK. “"Infoblox completes Axur takeover to boost threat defence".” Accessed . https://itbrief.co.uk/story/infoblox-completes-axur-takeover-to-boost-threat-defence
- 96.Infoblox. “Infoblox Free Tools - Threat Scan.” Accessed . https://freetools.axur.com/?lang=en