- Choose Silent Push when your security team investigates adversary infrastructure beyond your brand and delivers threat intelligence to the tools it already runs. 1–7
- Choose Have I Been Squatted to detect malicious domains, starting from continuous monitoring of your own, then block them in your gateways and endpoints through rules and hand removal to its own Takedowns team. 8–17
- Use both when your security team needs broad infrastructure intelligence and your brand team needs a dedicated lookalike monitoring and response workflow. 9–11,18–21
At a glance#
| Have I Been Squatted | Silent Push | |
|---|---|---|
| What you get | ||
| What you get | Detection and response for malicious domains8 | Threat-infrastructure intelligence with Indicators of Future Attack1 |
| Lookalike discovery | ||
| Lookalike discovery | Domain or asset searches with scheduled new-result alerts23–25 | |
| Infrastructure investigation | ||
| Infrastructure investigation | Atlas pivots on IPs, nameservers, certificates, favicons, tracking IDs (early access)26–29 | Pivots across passive DNS, certificates, WHOIS, favicons, banners30–32 |
| Threat-actor intelligence | ||
| Threat-actor intelligence | IOFA feeds, APT feeds, TLP Amber reports, analyst services2–4 | |
| Mail telemetry | ||
| Mail telemetry | Microsoft 365 and Google Workspace33–34 | |
| Response in your tools | ||
| Response in your tools | ||
| Managed takedowns | ||
| Managed takedowns | Analyst-reviewed domain Takedowns16–17 | Not offered (evidence for your takedown provider)40 |
| How you buy | ||
| How you buy | ||
How each product finds lookalike domains#
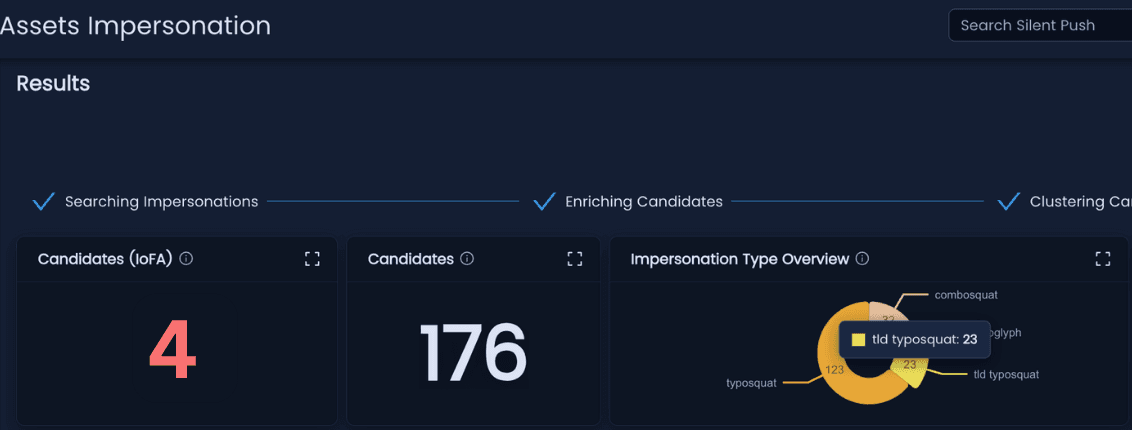
Silent Push finds lookalikes through impersonation searches that you save for a target. Domain Impersonation takes a target domain, and Assets Impersonation takes a My Assets folder of owned domains or IPs. Results group candidates into typosquat, homoglyph, combosquat and TLD variants, with overviews of registration date, HTTP response, registrar and ASN. Email Impersonation finds lookalikes that have MX records, while Favicon and HTML Title Impersonation match favicon hashes and page titles. Monitors rerun a saved query every 24 hours and alert you only when something new appears. 23–24,31,42–48
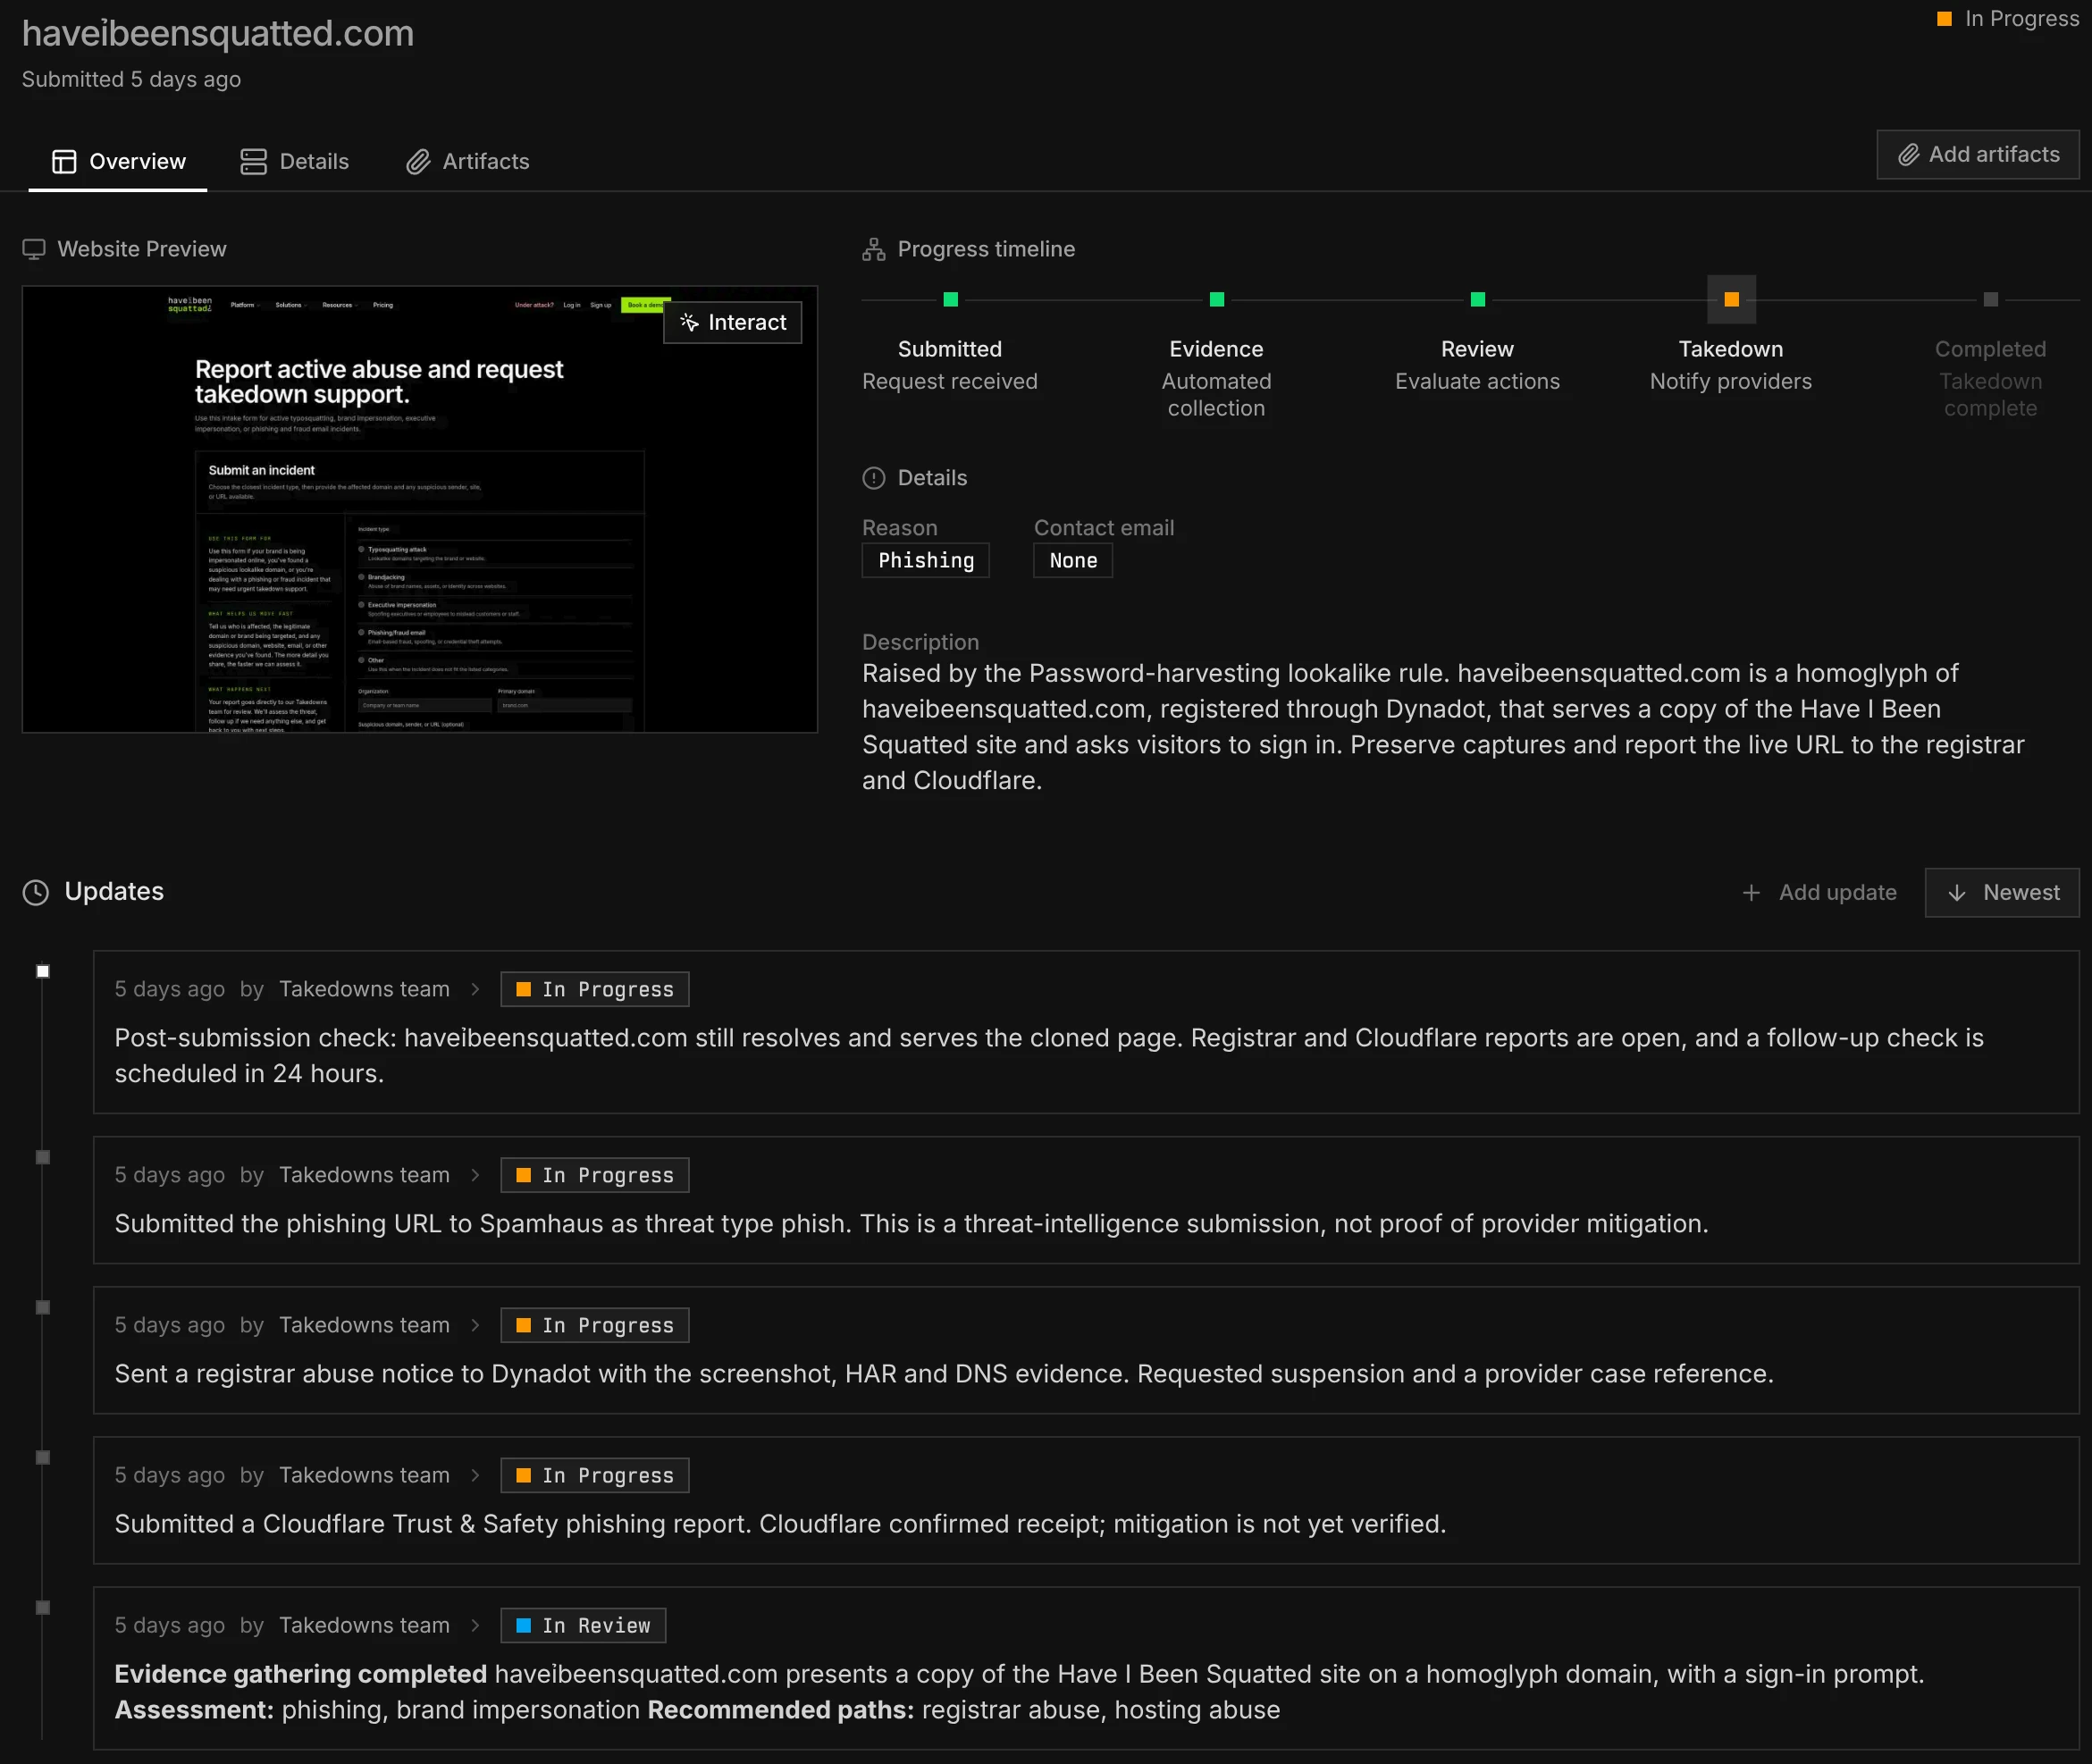
Have I Been Squatted generates and watches lookalikes for each monitored domain, with no keyword or permutation lists to maintain. Discovery combines generated kinds such as homoglyphs, bitsquats and TLD swaps with certificate transparency and newly registered domains. Business context lets agents suggest extra lookalikes, which become results only when they resolve. Each result combines the enrichment available for that domain, such as RDAP registration data, hosting and ASN, DNS records, mail readiness, open ports and a screenshot, with an isolated browser session for a closer look. Typosquat, Analyze and Discovery lookups cover one-off checks outside monitoring. 9–10,22,26,29,49–57
Two further signals show whether a lookalike has reached your people or copied your site. Email Intelligence correlates Microsoft 365 and Google Workspace mail telemetry, such as senders, recipients and URL domains, without MX changes. Site Canaries add a script to your own pages and flag page loads on hostnames you have not recognized. No public documentation of a Silent Push mailbox integration or of beacons that detect copied pages was found. 5,32–35,46,48,58–59
Sending findings to your tools and requesting removal#
Silent Push delivers intelligence through feeds, indicator lookups and connectors to security tools. Curated and customer-built IOFA feeds export as CSV or JSON, and scheduled Feed Search exports add TXT, RPZ, STIX and TAXII formats after the first export runs. Threat Check looks up indicators in bulk against IOFA feeds and Traffic Origin data, through the API or a DNS-based integration. Named connectors reach SIEM, SOAR and threat intelligence platforms, a bidirectional TAXII server shares feeds, and Slack, Teams and custom webhooks carry alerts. 2,5–7,35,38–39,60–63
Have I Been Squatted puts response in rules that run over domain signals. The maintained rules library covers common detections, and your team can write its own rules. A rule can raise an alert, deliver the finding to a SIEM, push the domain to a block list, annotate the result with a status such as Malicious, or request a Takedown. Network Enforcement sends flagged domains to gateways, endpoints and mail filters, and to a hosted domain feed in seven formats, including STIX 2.1 and CSV, with documented MISP setup. Tools poll the feed, and its STIX output is a static bundle rather than a TAXII server. For a single result, an admin can send one response now, outside any rule, such as a notification, a SIEM finding, a block or a detection. 9,11–15,20–21,36–37,49–50,57
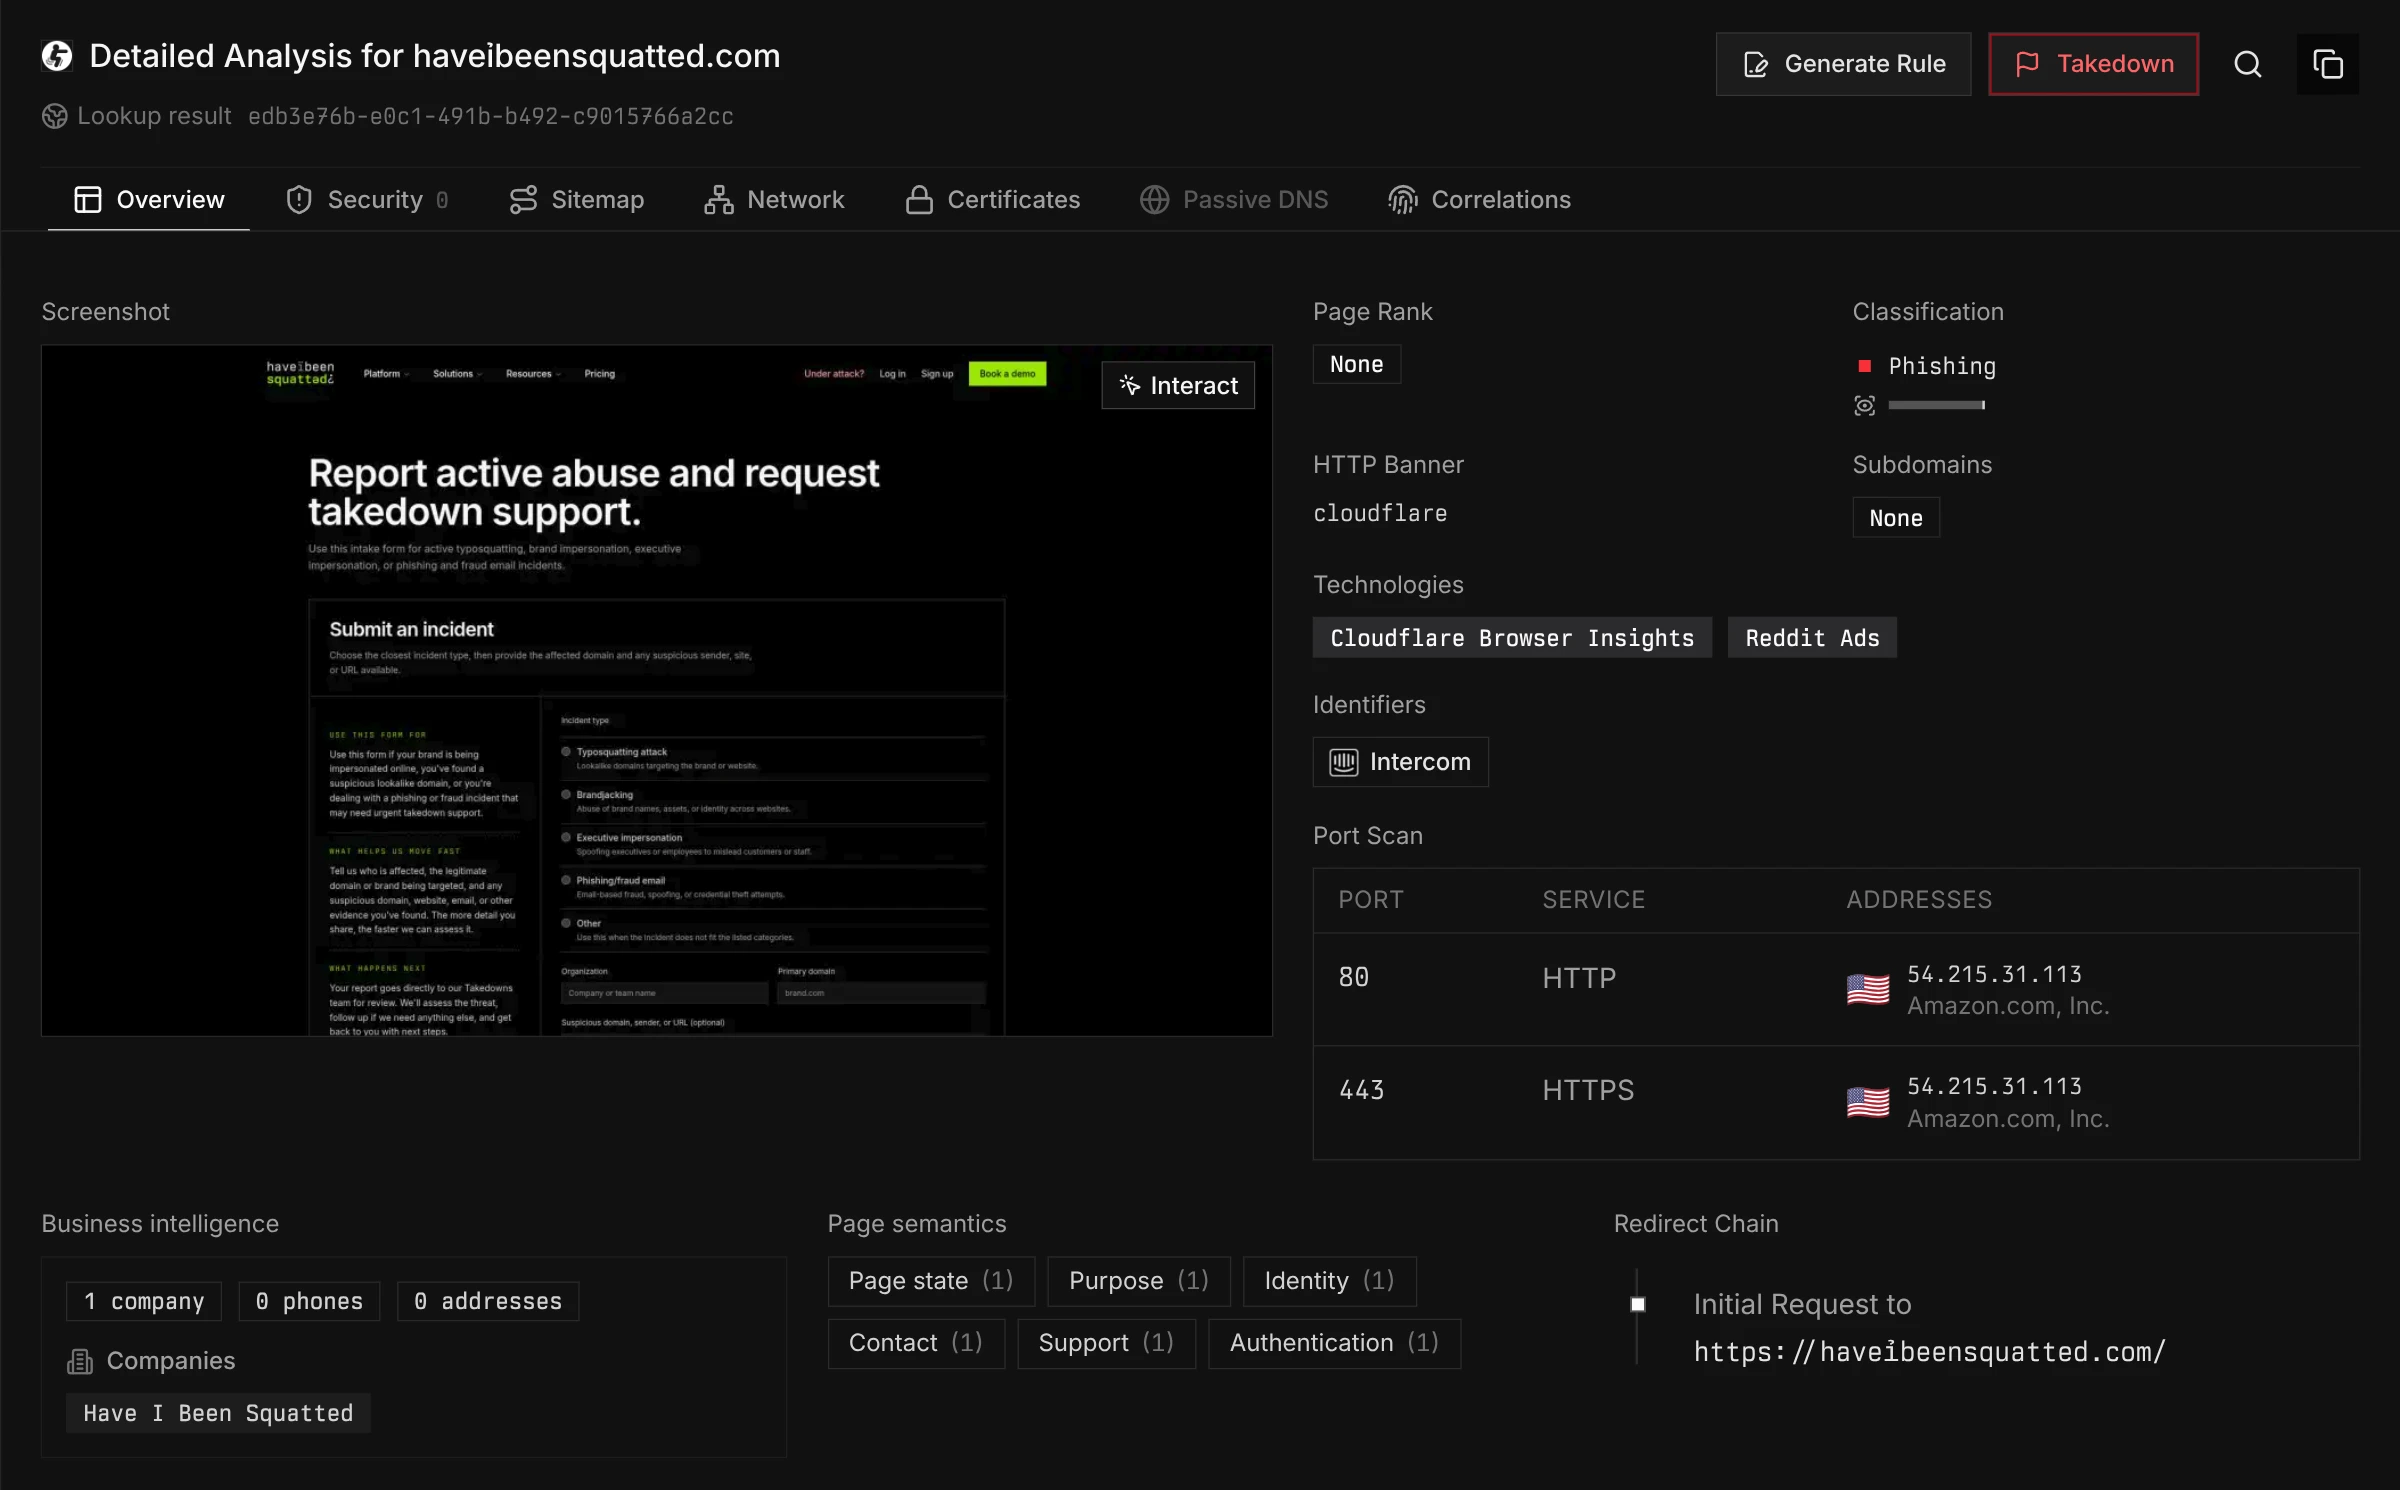
For removal, Silent Push says it does not take down malicious domains. It supplies the evidence for your takedown provider, and impersonation results can be exported as takedown evidence. Have I Been Squatted runs managed Takedowns. An analyst reviews every request, then the team reports the domain to its host and registrar. If a provider does not respond, the team escalates to ICANN and regional CSIRTs where necessary. Takedowns stop short of legal action, and the team can connect you with third-party legal providers. 6,9,16–17,32,40,64–65
Domain protection
Detect adversary infrastructure while it is being staged.
Have I Been Squatted helps security teams detect lookalike domains, certificate and DNS changes, and staging infrastructure, investigate the evidence, and coordinate takedowns.
Investigating infrastructure beyond your brand#
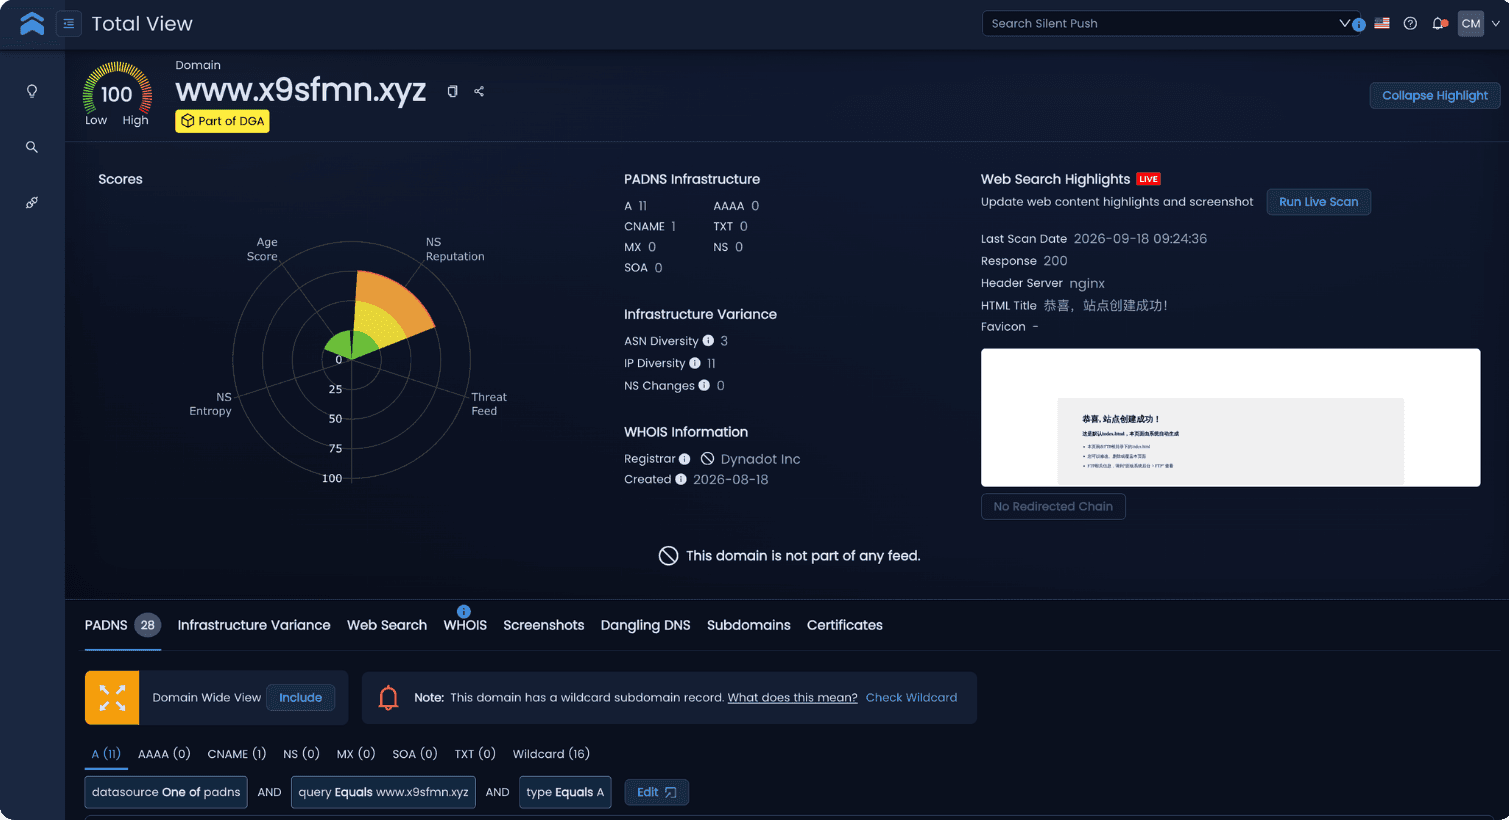
Silent Push helps analysts investigate adversary infrastructure beyond a brand's lookalike domains. It builds on first-party data that, Silent Push states, logs changes across the entire IPv4 and IPv6 space. Total View brings a domain's data together, and Silent Push states that it integrates over 100 data points that analysts can pivot on. Passive DNS history shows when records were first and last seen, beside Farsight and Zetalytics third-party passive DNS tabs and a WHOIS Changes chart. 18–19,31,35,60,66–70
Pivots follow shared fingerprints across domains and servers. Context Graph Search runs SPQL, a query language Silent Push lists as alpha, over web, dark web, open-directory, banner and WHOIS scan data. Analysts can match favicon Murmur3 hashes, ssdeep HTML similarity, JARM and server banners, and run sibling, cousin, nameserver and MX hash lookups. Traffic Origin returns the countries where traffic from an IP was detected, and Silent Push markets it as a way to reveal the true country behind a connection. 18,30–32,38,46,48,60,68,71–74
Have I Been Squatted reaches past your own lookalikes with Atlas investigations, in early access. An investigation starts from a hunt you describe and any domains you already suspect, pivots across shared infrastructure in Atlas, its store of domain observations, and keeps watching after the first pass. An admin can add IP addresses, nameservers, favicon hashes or identifiers for it to pivot on. Analysts review results in views such as Tree, Table, Clusters and Flows, and export an investigation as STIX 2.1, CSV or JSON. 17,26–29,75–76
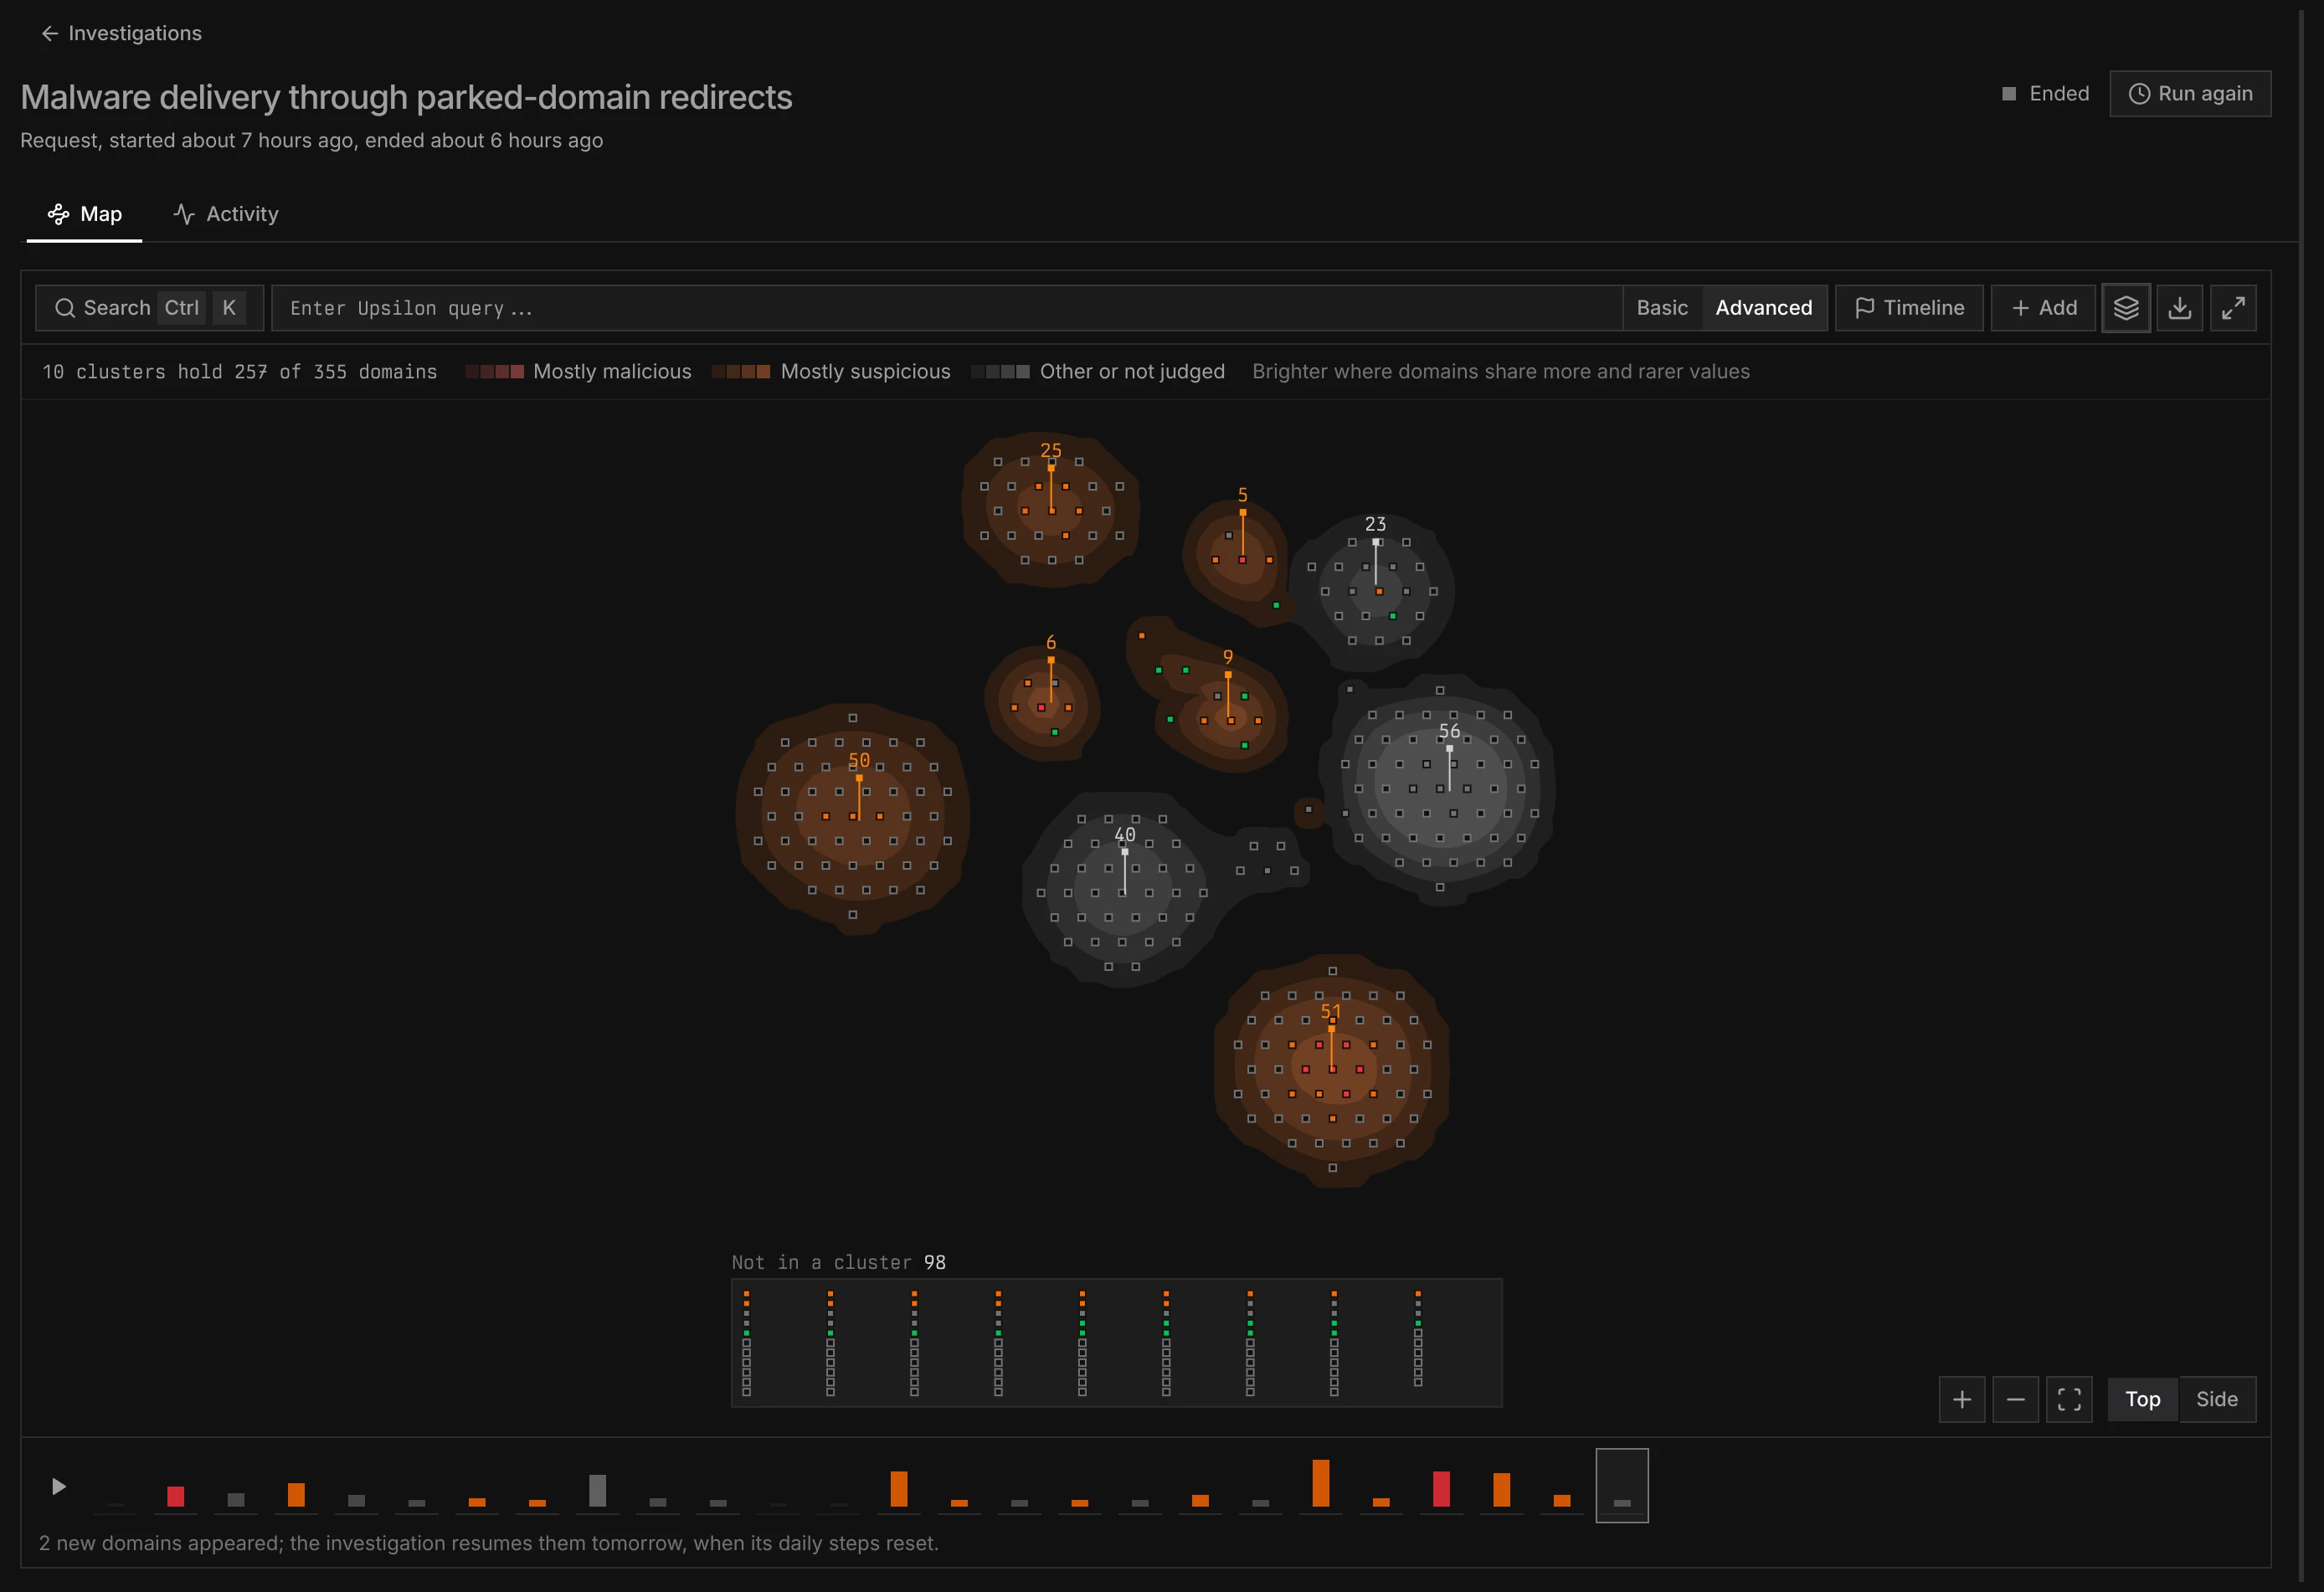
Where RDAP data is available, a lookalike also carries its current registration data, including registration, expiration and last-updated dates, but no record of past owners. Have I Been Squatted records current DNS records but does not collect passive DNS history today, so Silent Push keeps the deeper record of how infrastructure changed. Silent Push suits investigations that start from adversary infrastructure, and Have I Been Squatted suits teams that start with their own domains and need an enriched list of lookalikes to review. 9–10,26,29–32,49–51,53–54,67,69–70
Where Silent Push is the better choice#
Choose Silent Push when infrastructure intelligence is the job and brand lookalikes are one part of it. Its first-party scan data spans six data sources, including banners, open directories and Tor, and its passive DNS and WHOIS history let an investigation reach back in time. IOFA feeds, APT feeds, TLP Amber reports and Intelligence On-Demand analyst services extend that work to threat actors and campaigns. Silent Push states that IOFA often reveal attacks 3 to 6 months in advance. 2–4,18–19,31,67,69–70,77
It also suits a team with a broad security stack. Silent Push names 21 integrations with SIEM, SOAR, threat intelligence and other security platforms, including Microsoft Sentinel, plus a bidirectional TAXII server. A free, account-based version gives researchers full raw passive DNS data with a monthly request quota, for evaluation and research. Its Chrome extension lets an analyst scan a page's domains, IPs and URLs with an API key. 1–2,5–7,30,38–39,66–67,78–79
Where Have I Been Squatted is the better choice#
Choose Have I Been Squatted when your team needs malicious domains detected, blocked and taken down. Lookalikes of your own domains are one way in. Domain Monitoring watches for them continuously, with no keyword or permutation lists to maintain, and Analyze checks any other domain on demand. Rules from the maintained library, or written by your team over a catalog of 173 domain signals, decide whether a finding raises an alert, reaches your SIEM or gets blocked. A rule can also request a managed Takedown, and an analyst reviews every request before the team reports the domain to its host and registrar. 8–11,16–17,20–22,49–50,55–57,65,80–81
Blocking happens in the tools you already run. Network Enforcement pushes rule-flagged domains to Zscaler, Microsoft Defender for Endpoint, Cloudflare Zero Trust and iboss, and to Microsoft 365 Quarantine and Cloudflare Email Security for mail. Network Intelligence reads Microsoft Defender every 15 seconds and Cloudflare Gateway every minute, showing which domains devices on your network reached. End users can add the free Browser Protection extension for Chrome, which warns on dangerous or suspicious sites. 9,12–15,21,82–83
Monitoring, hunting tools, rules and alerts are a public self-serve subscription with a free trial. Takedowns and the email, network, SIEM and canary products are added through sales. For a security review, Have I Been Squatted has a SOC 2 Type II report, available through its Trust Center. No public documentation of a SOC 2 or ISO 27001 report was found for Silent Push. 9,22,55–57,78,82,84–85
A buyer who wants one platform for adversary infrastructure hunting, threat-actor feeds and proxy-origin data is better served by Silent Push. Have I Been Squatted does not scan the dark web, and it has no equivalent to Traffic Origin. 2–4,74,86–87
FAQ#
Silent Push can cover recurring lookalike discovery through saved impersonation searches and scheduled alerts for new results. It fits if your team wants to investigate those findings in Silent Push and deliver intelligence to its existing tools. Choose Have I Been Squatted when you want continuous Domain Monitoring tied to rules, connector actions and managed Takedowns. 5,7,9–11,16–17,20–21,23–25,35,42,62–63
No. Silent Push says it does not take down malicious domains. It supplies the evidence, and your team escalates it to your takedown provider. A 2024 help article described a registrar-abuse service for a limited number of customers. Have I Been Squatted runs managed Takedowns, with analyst review on every request. 6,16,32,40,64
Choose Silent Push when you need passive DNS history, Context Graph Search, IOFA feeds and threat-actor reports around infrastructure that may not yet target your brand. Choose Have I Been Squatted when the investigation starts from your own domains and ends in a rule, one immediate response or a Takedown. Atlas investigations, in early access, also pivot across shared infrastructure from a hunt you describe. 2–3,9–11,18,20–21,26,31,57,60,67,69–71
Yes. Silent Push offers a free, account-based version with a monthly request quota for evaluation and research, and its terms prohibit production use except by students or individual analysts. Have I Been Squatted offers a free trial and a public self-serve subscription for Domain Monitoring, hunting tools, rules and alerts. Takedowns and the email, network, SIEM and canary products are bought through sales. 9,22,30,66,78,82
Sources and corrections
Each numbered marker on this page links to its sources below. Each source shows the date it was last checked. If a fact is wrong or out of date, send a correction. A correction is checked against the source and the page is updated.
- 1.Silent Push. “Silent Push Platform.” Accessed . https://www.silentpush.com/platform/
- 2.Silent Push. “How To Use IOFA Feeds.” Accessed . https://help.silentpush.com/docs/how-to-use-iofa-feeds
- 3.Silent Push. “TLP Amber Reports.” Accessed . https://help.silentpush.com/docs/tlp-amber-reports
- 4.Silent Push. “Intelligence On-Demand.” Accessed . https://www.silentpush.com/intelligence-on-demand/
- 5.Silent Push. “Integrations.” Accessed . https://www.silentpush.com/integrations/
- 6.Silent Push. “Silent Push 6.1 Platform Detects Attacker Infrastructure Earlier.” Accessed . https://www.silentpush.com/press-releases/platform-6-1-earlier-action/
- 7.Silent Push. “Gaining Greater Control and Access Management with Preemptive Cyber Defense (Silent Push 6.2, 2026-10-06).” Accessed . https://www.silentpush.com/blog/platform-6-2/
- 8.Have I Been Squatted. “Homepage (footer tagline).” Accessed . https://haveibeensquatted.com/
- 9.Have I Been Squatted. “Pricing.” Accessed . https://haveibeensquatted.com/pricing
- 10.Have I Been Squatted. “Domain monitoring guide.” Accessed . https://docs.haveibeensquatted.com/features/domain-monitoring/
- 11.Have I Been Squatted. “Rules engine guide.” Accessed . https://docs.haveibeensquatted.com/guides/rules-engine/
- 12.Have I Been Squatted. “Network Enforcement.” Accessed . https://haveibeensquatted.com/platform/network-enforcement
- 13.Have I Been Squatted. “Domain feed integration.” Accessed . https://docs.haveibeensquatted.com/integrations/domain-feed/
- 14.Have I Been Squatted. “CrowdStrike Falcon integration.” Accessed . https://docs.haveibeensquatted.com/integrations/crowdstrike-falcon/
- 15.Have I Been Squatted. “Microsoft Defender for Endpoint integration.” Accessed . https://docs.haveibeensquatted.com/integrations/microsoft-defender-endpoint/
- 16.Have I Been Squatted. “Takedowns.” Accessed . https://haveibeensquatted.com/platform/takedowns
- 17.Have I Been Squatted. “Takedowns guide.” Accessed . https://docs.haveibeensquatted.com/features/takedowns/
- 18.Silent Push. “SPQL Data Sources.” Accessed . https://help.silentpush.com/docs/data-sources
- 19.Silent Push. “About Us.” Accessed . https://www.silentpush.com/company/
- 20.Have I Been Squatted. “Integrations.” Accessed . https://haveibeensquatted.com/platform/integrations
- 21.Have I Been Squatted. “Network Intelligence guide.” Accessed . https://docs.haveibeensquatted.com/features/network-intelligence/
- 22.Have I Been Squatted. “Domain Monitoring.” Accessed . https://haveibeensquatted.com/platform/monitoring
- 23.Silent Push. “Monitored Queries.” Accessed . https://help.silentpush.com/docs/monitored-queries
- 24.Silent Push. “Assets Impersonation.” Accessed . https://help.silentpush.com/docs/assets-impersonation
- 25.Silent Push. “Brand Impersonation Monitoring and Queries.” Accessed . https://help.silentpush.com/docs/brand-impersonation-monitoring-and-queries
- 26.Have I Been Squatted. “Atlas investigations.” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/
- 27.Have I Been Squatted. “Atlas investigations (shareable view links).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#read-the-map
- 28.Have I Been Squatted. “Atlas investigations (New investigation flow).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#start-an-investigation
- 29.Have I Been Squatted. “Atlas investigations (add domains and indicators).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#steer-an-investigation
- 30.Silent Push. “Community Edition.” Accessed . https://www.silentpush.com/community-edition/
- 31.Silent Push. “Release 6.1.” Accessed . https://help.silentpush.com/docs/release-6-1
- 32.Silent Push. “Silent Push Knowledge Base index (no entry contains "takedown").” Accessed . https://help.silentpush.com/llms.txt
- 33.Have I Been Squatted. “Email Intelligence guide.” Accessed . https://docs.haveibeensquatted.com/features/email-intelligence/
- 34.Have I Been Squatted. “Email Intelligence.” Accessed . https://haveibeensquatted.com/platform/email-intelligence
- 35.Silent Push. “Release 5.1.” Accessed . https://help.silentpush.com/docs/release-51
- 36.Have I Been Squatted. “Alert digest guide.” Accessed . https://docs.haveibeensquatted.com/guides/digest/
- 37.Have I Been Squatted. “Connectors.” Accessed . https://docs.haveibeensquatted.com/integrations/
- 38.Silent Push. “Release 5.0.” Accessed . https://help.silentpush.com/docs/release-50
- 39.Silent Push. “How To Use Feed Search.” Accessed . https://help.silentpush.com/docs/how-to-use-feed-search
- 40.Silent Push. “"Silent Push Joins Singapore's IMDA Spark Programme" (2026-10-16), FAQ.” Accessed . https://www.silentpush.com/news/singapore-imda-spark-programme/
- 41.Silent Push via Internet Archive. “Understand our subscription types (archived 2024-09-27, page updated 2024-08-12).” Accessed . https://web.archive.org/web/20240927161637/https://help.silentpush.com/docs/subscriptions
- 42.Silent Push. “Impersonation.” Accessed . https://help.silentpush.com/docs/impersonation
- 43.Silent Push. “Domain Impersonation.” Accessed . https://help.silentpush.com/docs/domain-impersonation
- 44.Silent Push. “Scan for Domain Siblings.” Accessed . https://help.silentpush.com/docs/scan-for-domain-siblings
- 45.Silent Push. “Email Impersonation.” Accessed . https://help.silentpush.com/docs/email-impersonation
- 46.Silent Push. “Favicon Impersonation.” Accessed . https://help.silentpush.com/docs/favicon-impersonation.md
- 47.Silent Push. “HTML Title Impersonation.” Accessed . https://help.silentpush.com/docs/html-title-impersonation
- 48.Silent Push. “HTML Content Similarity.” Accessed . https://help.silentpush.com/docs/html-content-similarity
- 49.Have I Been Squatted. “Domain signals.” Accessed . https://docs.haveibeensquatted.com/reference/signals/domain/
- 50.Have I Been Squatted. “Changelog.” Accessed . https://haveibeensquatted.com/changelog
- 51.Have I Been Squatted. “Atlas observations: registration data by TLD.” Accessed . https://mcp.haveibeensquatted.com/mcp
- 52.Have I Been Squatted. “Platform.” Accessed . https://haveibeensquatted.com/platform
- 53.Have I Been Squatted. “Passive DNS guide.” Accessed . https://docs.haveibeensquatted.com/features/passive-dns/
- 54.Spamhaus. “Spamhaus passive DNS endpoint, unauthenticated probe.” Accessed . https://beta-pdns.spamhaus.com/api/v3/login
- 55.Have I Been Squatted. “Access control reference.” Accessed . https://docs.haveibeensquatted.com/reference/access-control/
- 56.Have I Been Squatted. “Agents.” Accessed . https://haveibeensquatted.com/platform/agents
- 57.Have I Been Squatted. “MCP server.” Accessed . https://docs.haveibeensquatted.com/ai/mcp/
- 58.Have I Been Squatted. “Site Canaries.” Accessed . https://haveibeensquatted.com/platform/site-canaries
- 59.Have I Been Squatted. “Site Canaries guide.” Accessed . https://docs.haveibeensquatted.com/features/site-canaries/
- 60.Silent Push. “Release 6.0.” Accessed . https://help.silentpush.com/docs/release-6-0
- 61.Silent Push. “Threat Check.” Accessed . https://help.silentpush.com/docs/threat-check
- 62.Silent Push. “CrowdStrike Indicator Feed Integration.” Accessed . https://help.silentpush.com/docs/crowdstrike-integration
- 63.Silent Push. “Notification Center.” Accessed . https://help.silentpush.com/docs/notification-center
- 64.Silent Push via Internet Archive. “Understand the Takedown service (archived 2024-09-27, page updated 2024-05-16).” Accessed . https://web.archive.org/web/20240927133936/https://help.silentpush.com/docs/takedown-service
- 65.Have I Been Squatted. “FAQ (stalled takedowns).” Accessed . https://haveibeensquatted.com/faq#takedowns-stall
- 66.Silent Push. “Total View.” Accessed . https://help.silentpush.com/docs/total-view
- 67.Silent Push. “PADNS Tab.” Accessed . https://help.silentpush.com/docs/padns-tab
- 68.Silent Push. “API Feature Overview.” Accessed . https://help.silentpush.com/docs/silent-push-api-highlights
- 69.Silent Push. “Farsight Tab.” Accessed . https://help.silentpush.com/docs/farsight-tab
- 70.Silent Push. “Zetalytics Tab.” Accessed . https://help.silentpush.com/docs/zetalytics-tab
- 71.Silent Push. “Context Graph Search Datasources.” Accessed . https://help.silentpush.com/docs/context-graph-search-datasources
- 72.Silent Push. “The Silent Push API.” Accessed . https://www.silentpush.com/api/
- 73.Silent Push. “SPQL.” Accessed . https://help.silentpush.com/docs/spql
- 74.Silent Push. “Traffic Origin.” Accessed . https://www.silentpush.com/traffic-origin/
- 75.Have I Been Squatted. “Reports guide.” Accessed . https://docs.haveibeensquatted.com/features/reports/
- 76.Have I Been Squatted. “Explore guide.” Accessed . https://docs.haveibeensquatted.com/features/explore/
- 77.Silent Push. “Purchase Analyst Credits.” Accessed . https://help.silentpush.com/docs/purchase-an-analsyt-credit
- 78.Silent Push. “Terms of Service, Community Edition section B.” Accessed . https://www.silentpush.com/terms-of-use/
- 79.Silent Push. “Silent Push Chrome Extension.” Accessed . https://help.silentpush.com/docs/silent-push-chrome-extension
- 80.Have I Been Squatted. “API: Analyze a URL.” Accessed . https://docs.haveibeensquatted.com/guides/api/analyze/#analyze-a-url
- 81.Have I Been Squatted. “Tools: Analyze (URL analysis note, served without sign-in).” Accessed . https://haveibeensquatted.com/app/tools?mode=analyze
- 82.Have I Been Squatted. “Network Intelligence.” Accessed . https://haveibeensquatted.com/platform/network-intelligence
- 83.Have I Been Squatted. “Browser Protection.” Accessed . https://docs.haveibeensquatted.com/browser-protection/
- 84.Have I Been Squatted. “Security.” Accessed . https://haveibeensquatted.com/about/security
- 85.Silent Push. “Contact.” Accessed . https://www.silentpush.com/contact/
- 86.Have I Been Squatted. “Solutions.” Accessed . https://haveibeensquatted.com/solutions
- 87.Have I Been Squatted. “Brand protection.” Accessed . https://haveibeensquatted.com/solutions/brand-protection