- Choose Doppel when social engineering spans domains, social profiles, ads, apps, messaging and executives, and you want managed takedowns plus campaign correlation across those channels. 1–6
- Choose Have I Been Squatted to detect malicious domains and the infrastructure behind them, starting from generated lookalikes, with your own rules enforced as blocks in your gateways and endpoints. 7–15
- Use both if Doppel runs your wider brand program and your security team wants its own domain rules and response, with one product named as owner of domain triage and takedown requests. 1–3,8–19
At a glance#
| Have I Been Squatted | Doppel | |
|---|---|---|
| What you get | ||
| What you get | Detection and response for malicious domains7 | Social engineering defense with Brand Protection20 |
| Lookalike discovery | ||
| Lookalike discovery | Permutations, certificate transparency, newly registered domains, business context21–22 | |
| Campaign correlation | ||
| Campaign correlation | Domain investigations and pivots in Atlas, early access24–27 | Threat Graph across domains, profiles, ads and more4–5 |
| Alert triage | ||
| Alert triage | ||
| Response in your tools | ||
| Response in your tools | ||
| Managed takedowns | ||
| Managed takedowns | ||
| Beyond domains | ||
| Beyond domains | Not covered: social, apps, dark web, ads40–41 | Social, apps, ads, dark web, phone, email, training1–3 |
| How you buy | ||
| How you buy | Quote-based contract42 | |
Coverage beyond lookalike domains#
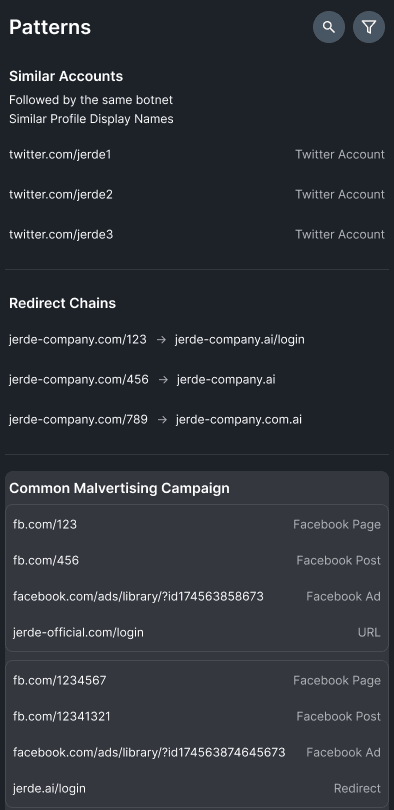
Doppel sells social engineering defense that reaches well past domains. Brand Protection monitors impersonation, fraud and counterfeit attacks across domains, social media, ads, the dark web, apps and messaging. Executive Protection adds impersonation detection, dark-web credential monitoring and takedowns that include data broker sites and voice numbers. Threat Graph Intelligence links those findings into campaigns, and the same platform also ships Email Security, Phishing Triage, Simulation and Security Awareness Training. 2,4,20,43–49
That breadth changes the buyer's day. A brand or fraud team can hand one vendor its lookalike domains, fake profiles, scam ads and executive exposure, then ask Doppel's SOC to take confirmed threats down across those channels. Doppel's integrations directory lists 61 integrations, most of them channels such as social networks, app stores, crypto sites and email providers. Doppel states that its Threat Graph connects domains, profiles, ads, phone numbers and related signals into attacker campaigns. 1–6
Have I Been Squatted concentrates on domains and the threats built on them. Domain Monitoring generates lookalikes and watches certificate transparency and newly registered domains. Email Intelligence adds mail telemetry from Microsoft 365 and Google Workspace, and Site Canaries flag copies of your own pages. Have I Been Squatted does not monitor social media, app stores, the dark web, ads or leaked credentials. 16,21–22,40–41,50–52
How each product investigates a lookalike domain#
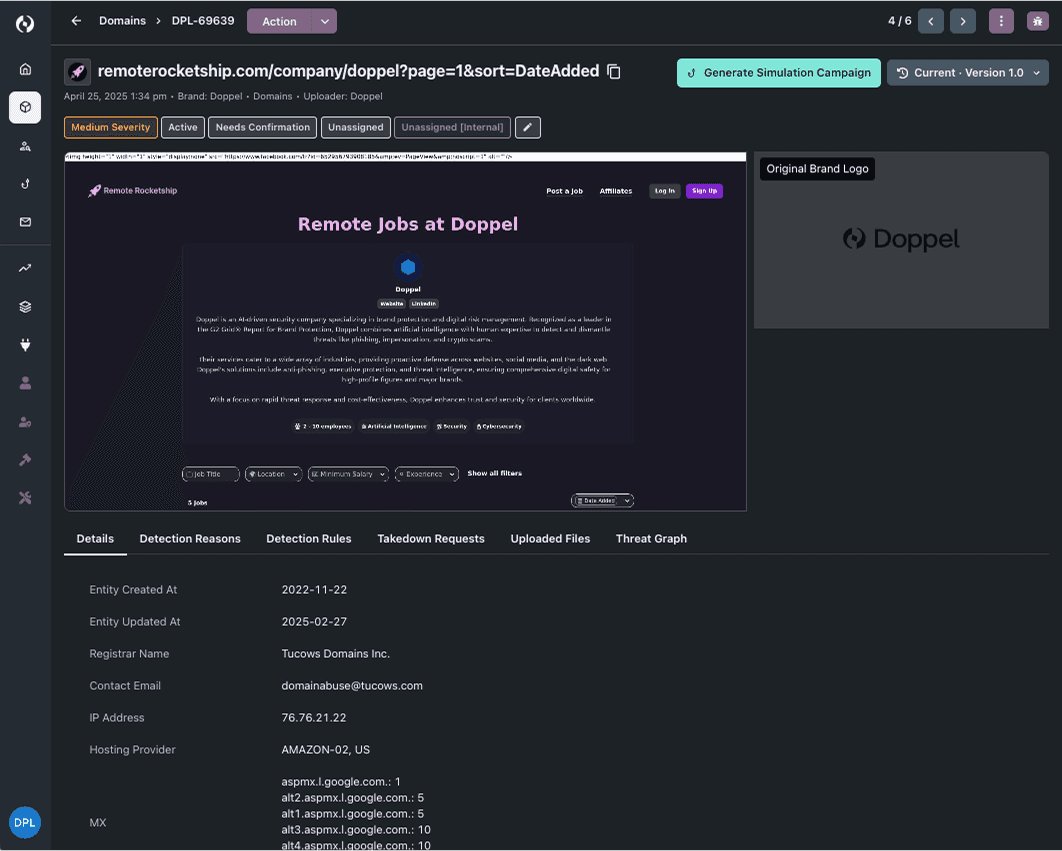
Doppel analysts review domain alerts before your team confirms them, while Have I Been Squatted gives your own analysts the evidence to investigate. Brand Protection monitors for lookalike domains as part of a wider brand alert stream. A Doppel domain alert can carry registrar, contact email, IP address, hosting provider, country, MX records and nameservers, plus a screenshot with a signed URL. The Scan API scores submitted URLs as low, medium or high suspiciousness, and alerts carry severity, a numeric score and an AI-generated summary. 1–3,20,23,29,53–55
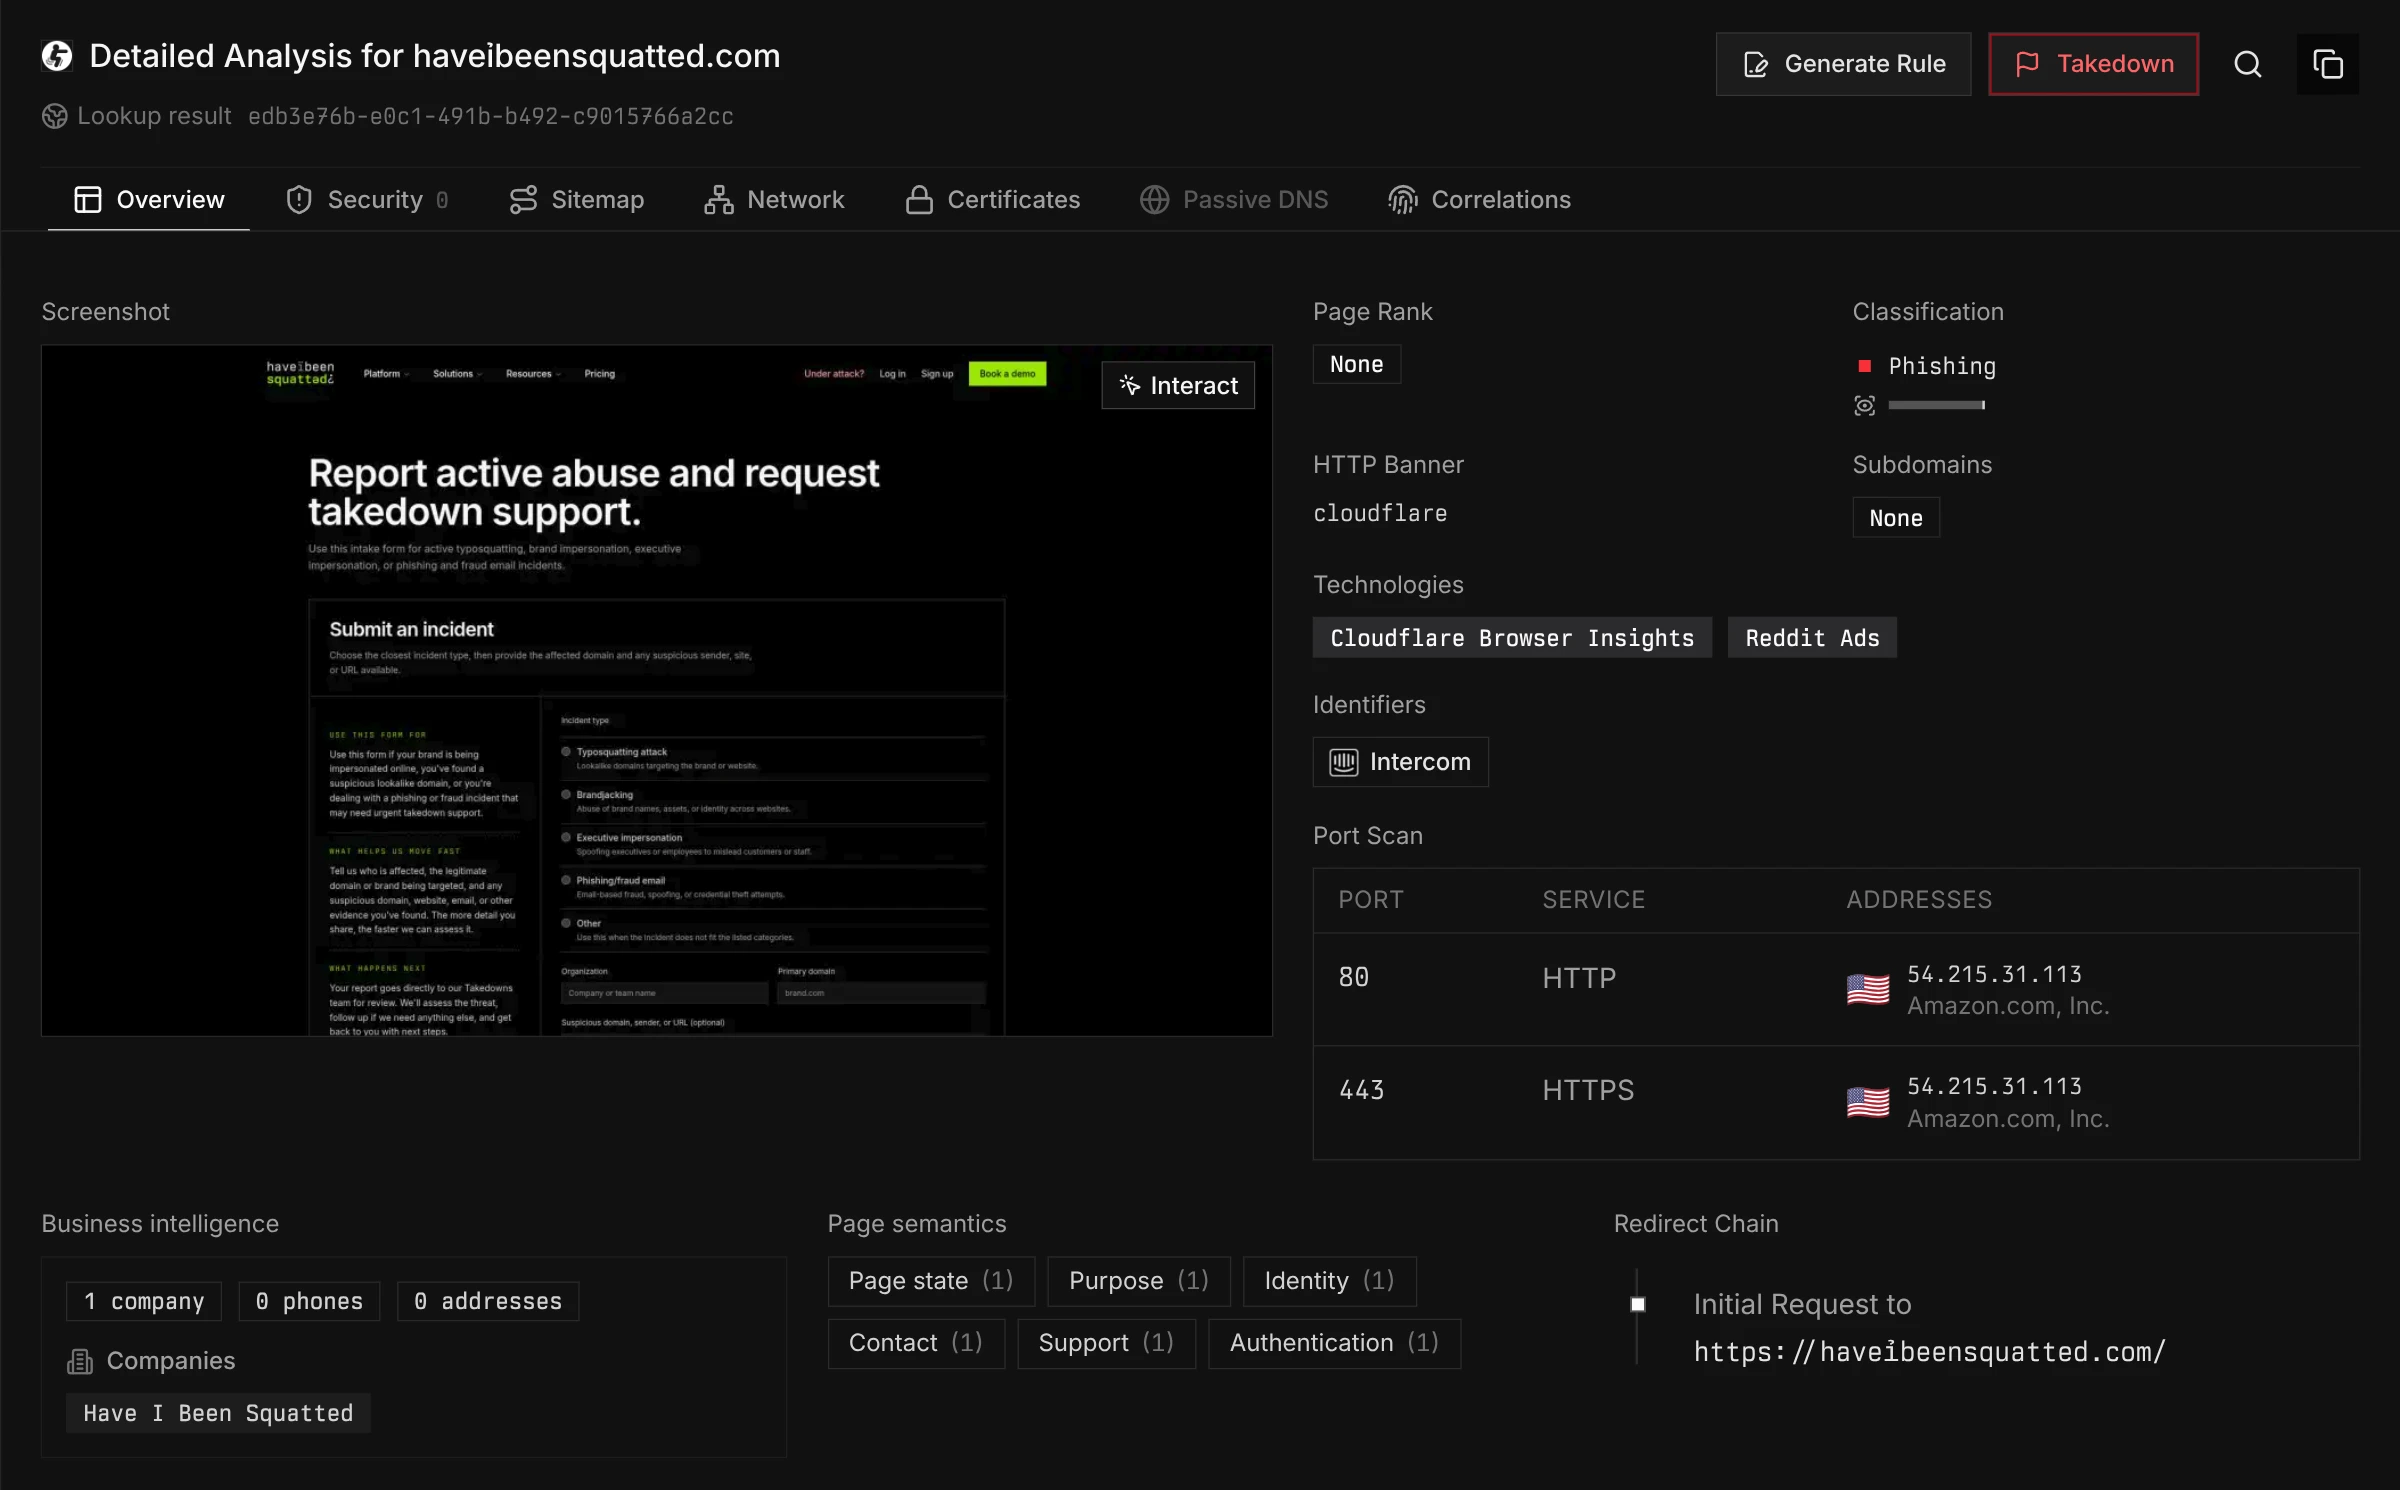
Have I Been Squatted results can include RDAP registration data, hosting details, DNS records, mail readiness, open ports and a capture of the website. Discovery combines generated lookalikes, with named kinds such as homoglyphs, bitsquats and TLD swaps, with certificate transparency and newly registered domains. A first-party model classifies each result as legitimate, parked or phishing, with a confidence score, and rule authors assign their own scores. An analyst can check whether a lookalike resolves, is set up for email or serves a copied page, then open it in an isolated browser. Signed-in users can also give Analyze a single page's URL, such as a phishing kit's path with its token, in the dashboard, through the API or through the MCP server. 8–10,16,18–19,21–22,24,27,56–62
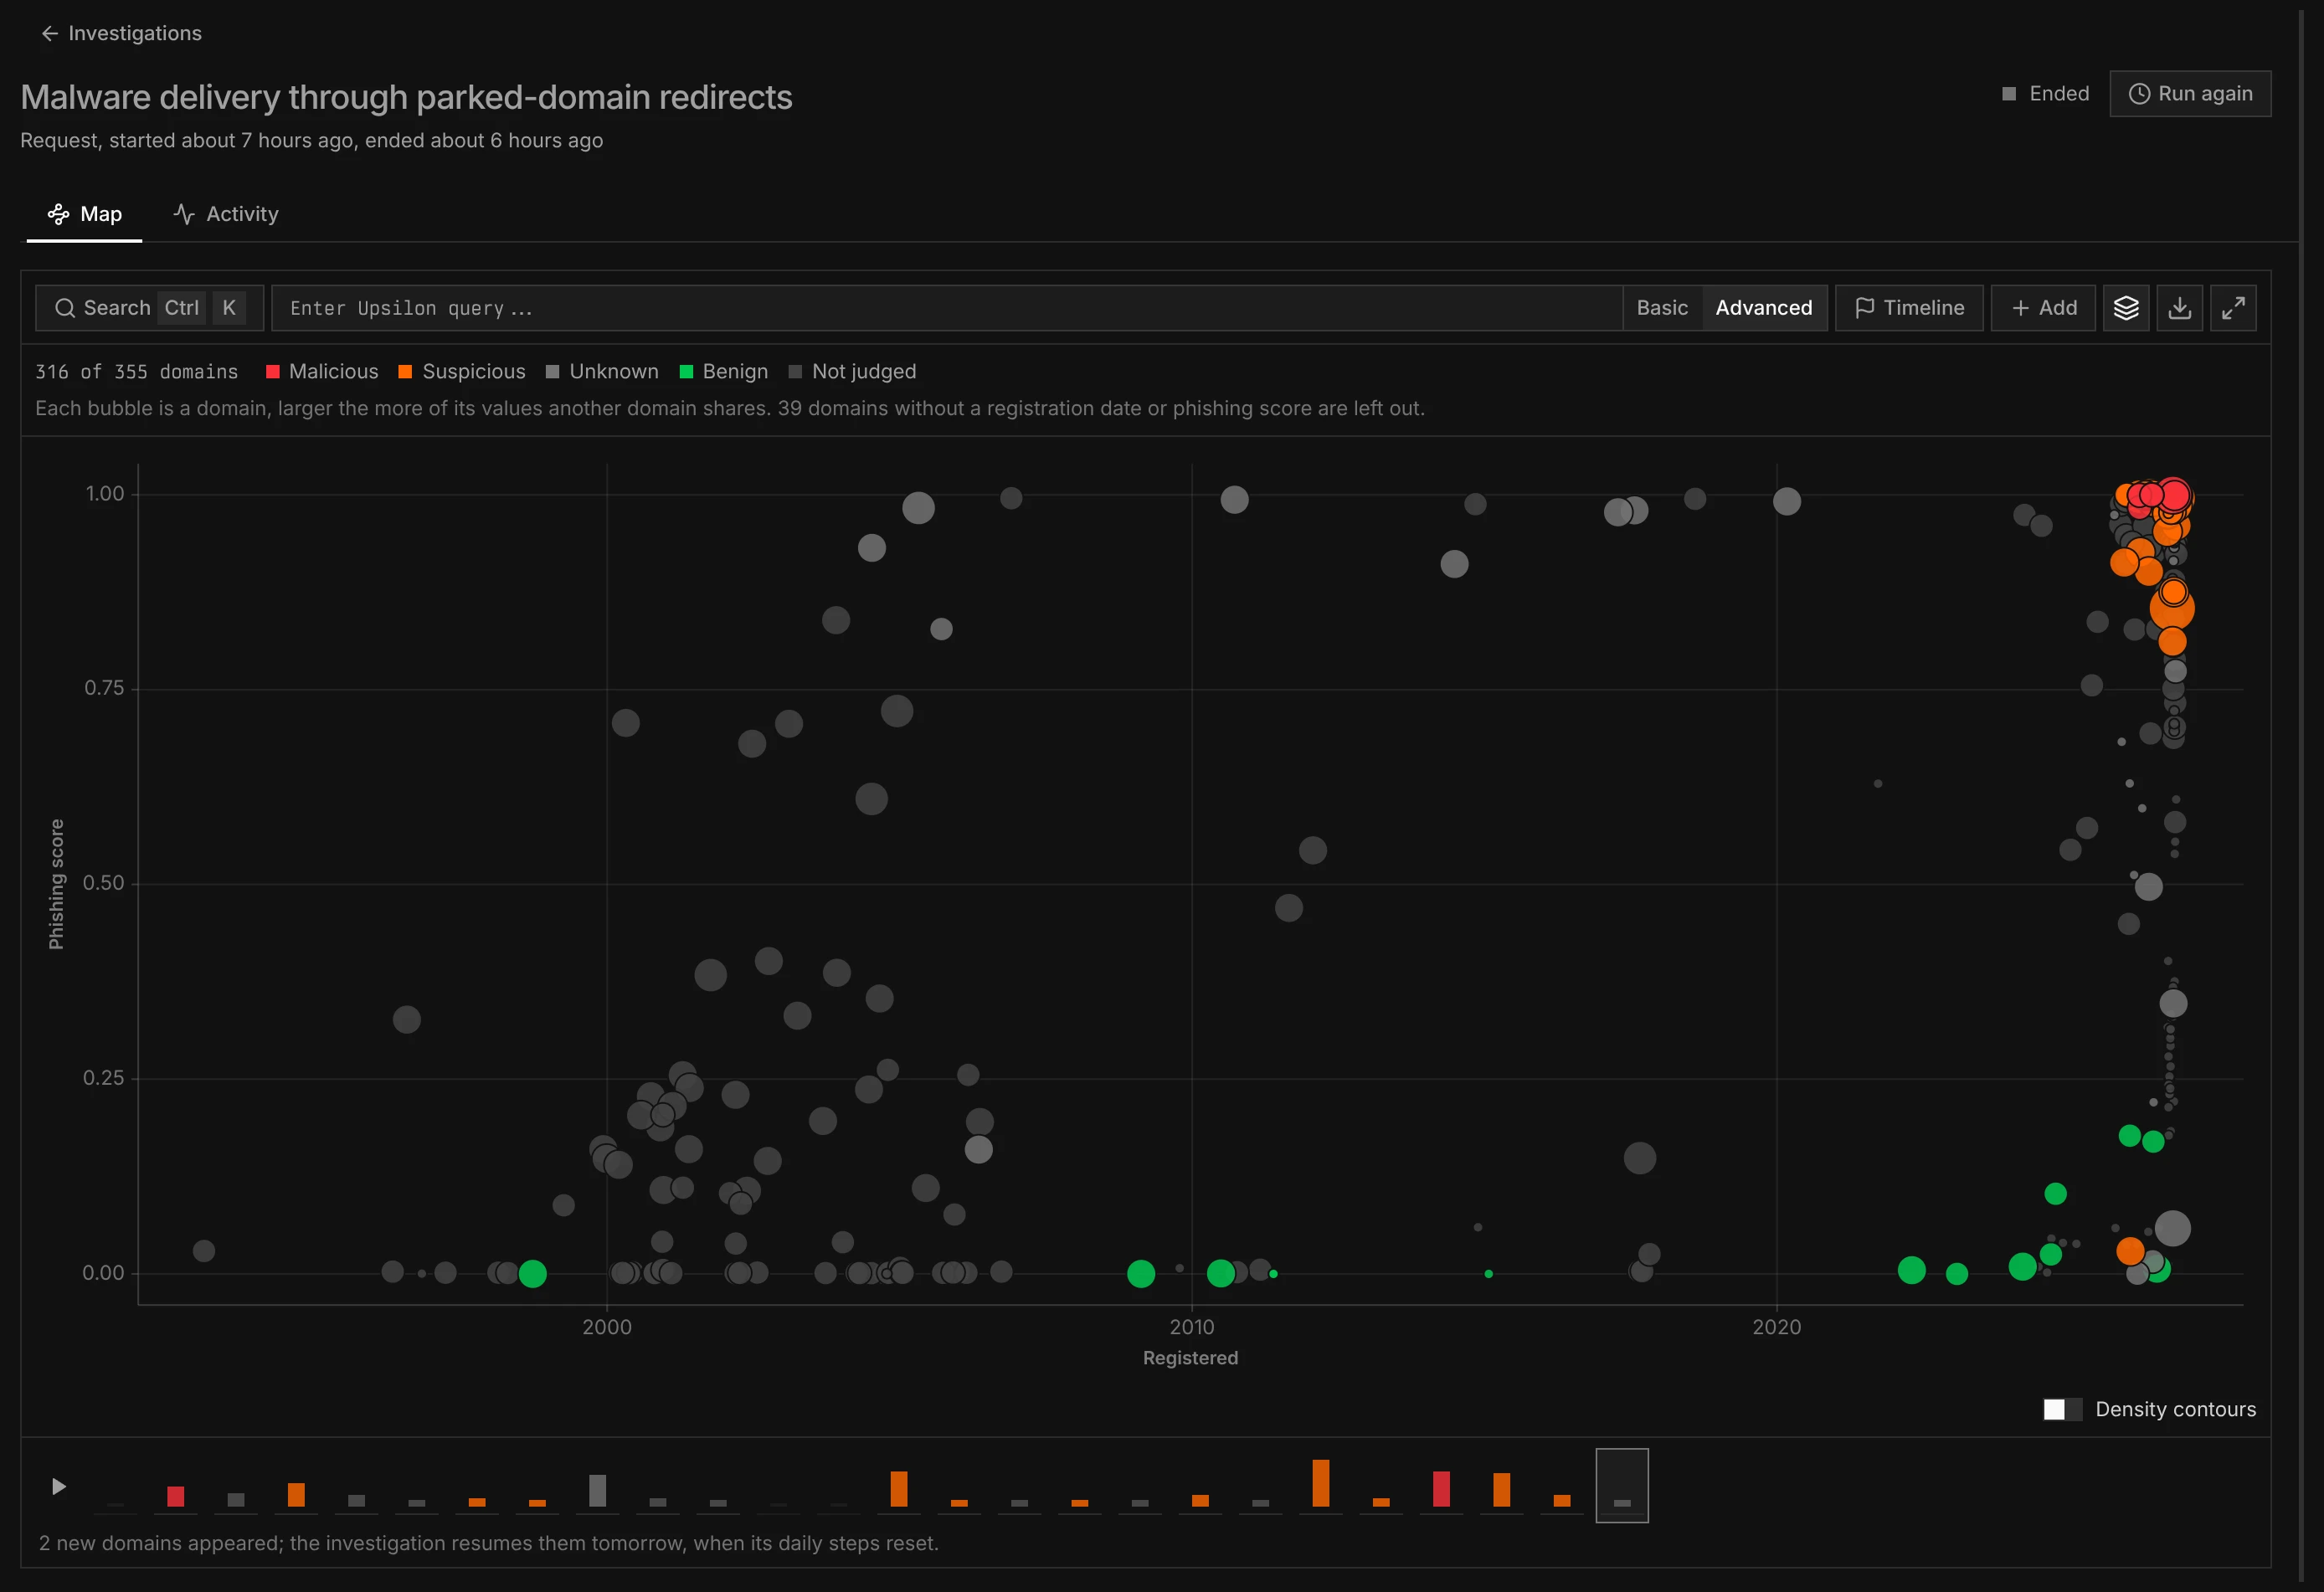
For campaign work on domains, Have I Been Squatted offers Atlas investigations in early access. An investigation begins from a hunt described in plain words, optionally with domains you already suspect, then pivots across shared infrastructure in Atlas, the store of domain observations. An admin can add indicators such as IP addresses or nameservers along the way. It keeps running after the first pass and reruns its name searches every six hours. Views such as Tree, Table, Clusters and Flows show the result, and an investigation exports as STIX 2.1, CSV or JSON. 24–27,37,63–64
Choose Doppel when you want analysts to review domain alerts alongside threats on other channels, with its Threat Graph correlating campaigns across them while Atlas stays with domains. Choose Have I Been Squatted when your team wants to investigate domain evidence itself and control response through maintained or custom rules. 1–2,4–5,8–11,16,29
Acting on a finding in your own tools#
Both products send findings to your security tools, and the difference is where a block lands. Doppel sends findings through its public REST API, webhooks and connectors such as Splunk, Elastic and Microsoft Sentinel, so your team can work them in its existing investigation and response workflows. Doppel also states that confirmed malicious sites can reach Phantom and MetaMask blocklists, and that its validated malicious-site intelligence extends into Coinbase Wallet. No public documentation of Doppel delivering blocks to a customer's own DNS resolvers or secure web gateways was found. 1,3,23,33–35,65–66
Have I Been Squatted puts response in rules that run over domain signals. A maintained rules library covers common detections, and your team can add its own rules. A rule can raise an alert, deliver the finding to a SIEM, push the domain to a block list or request a Takedown. It can also mark each matched result with a status such as Malicious and a note. Network Enforcement sends flagged domains to gateways, endpoints, mail filters and a hosted domain feed. 8–16,30–32
Network Intelligence reads Microsoft Defender and Cloudflare Gateway traffic counts for each destination, so your team can see traffic to a flagged domain from its own network. An MCP server lets agents work the same alerts and Takedowns, and every write needs an admin. 11,17,19,63,67–69
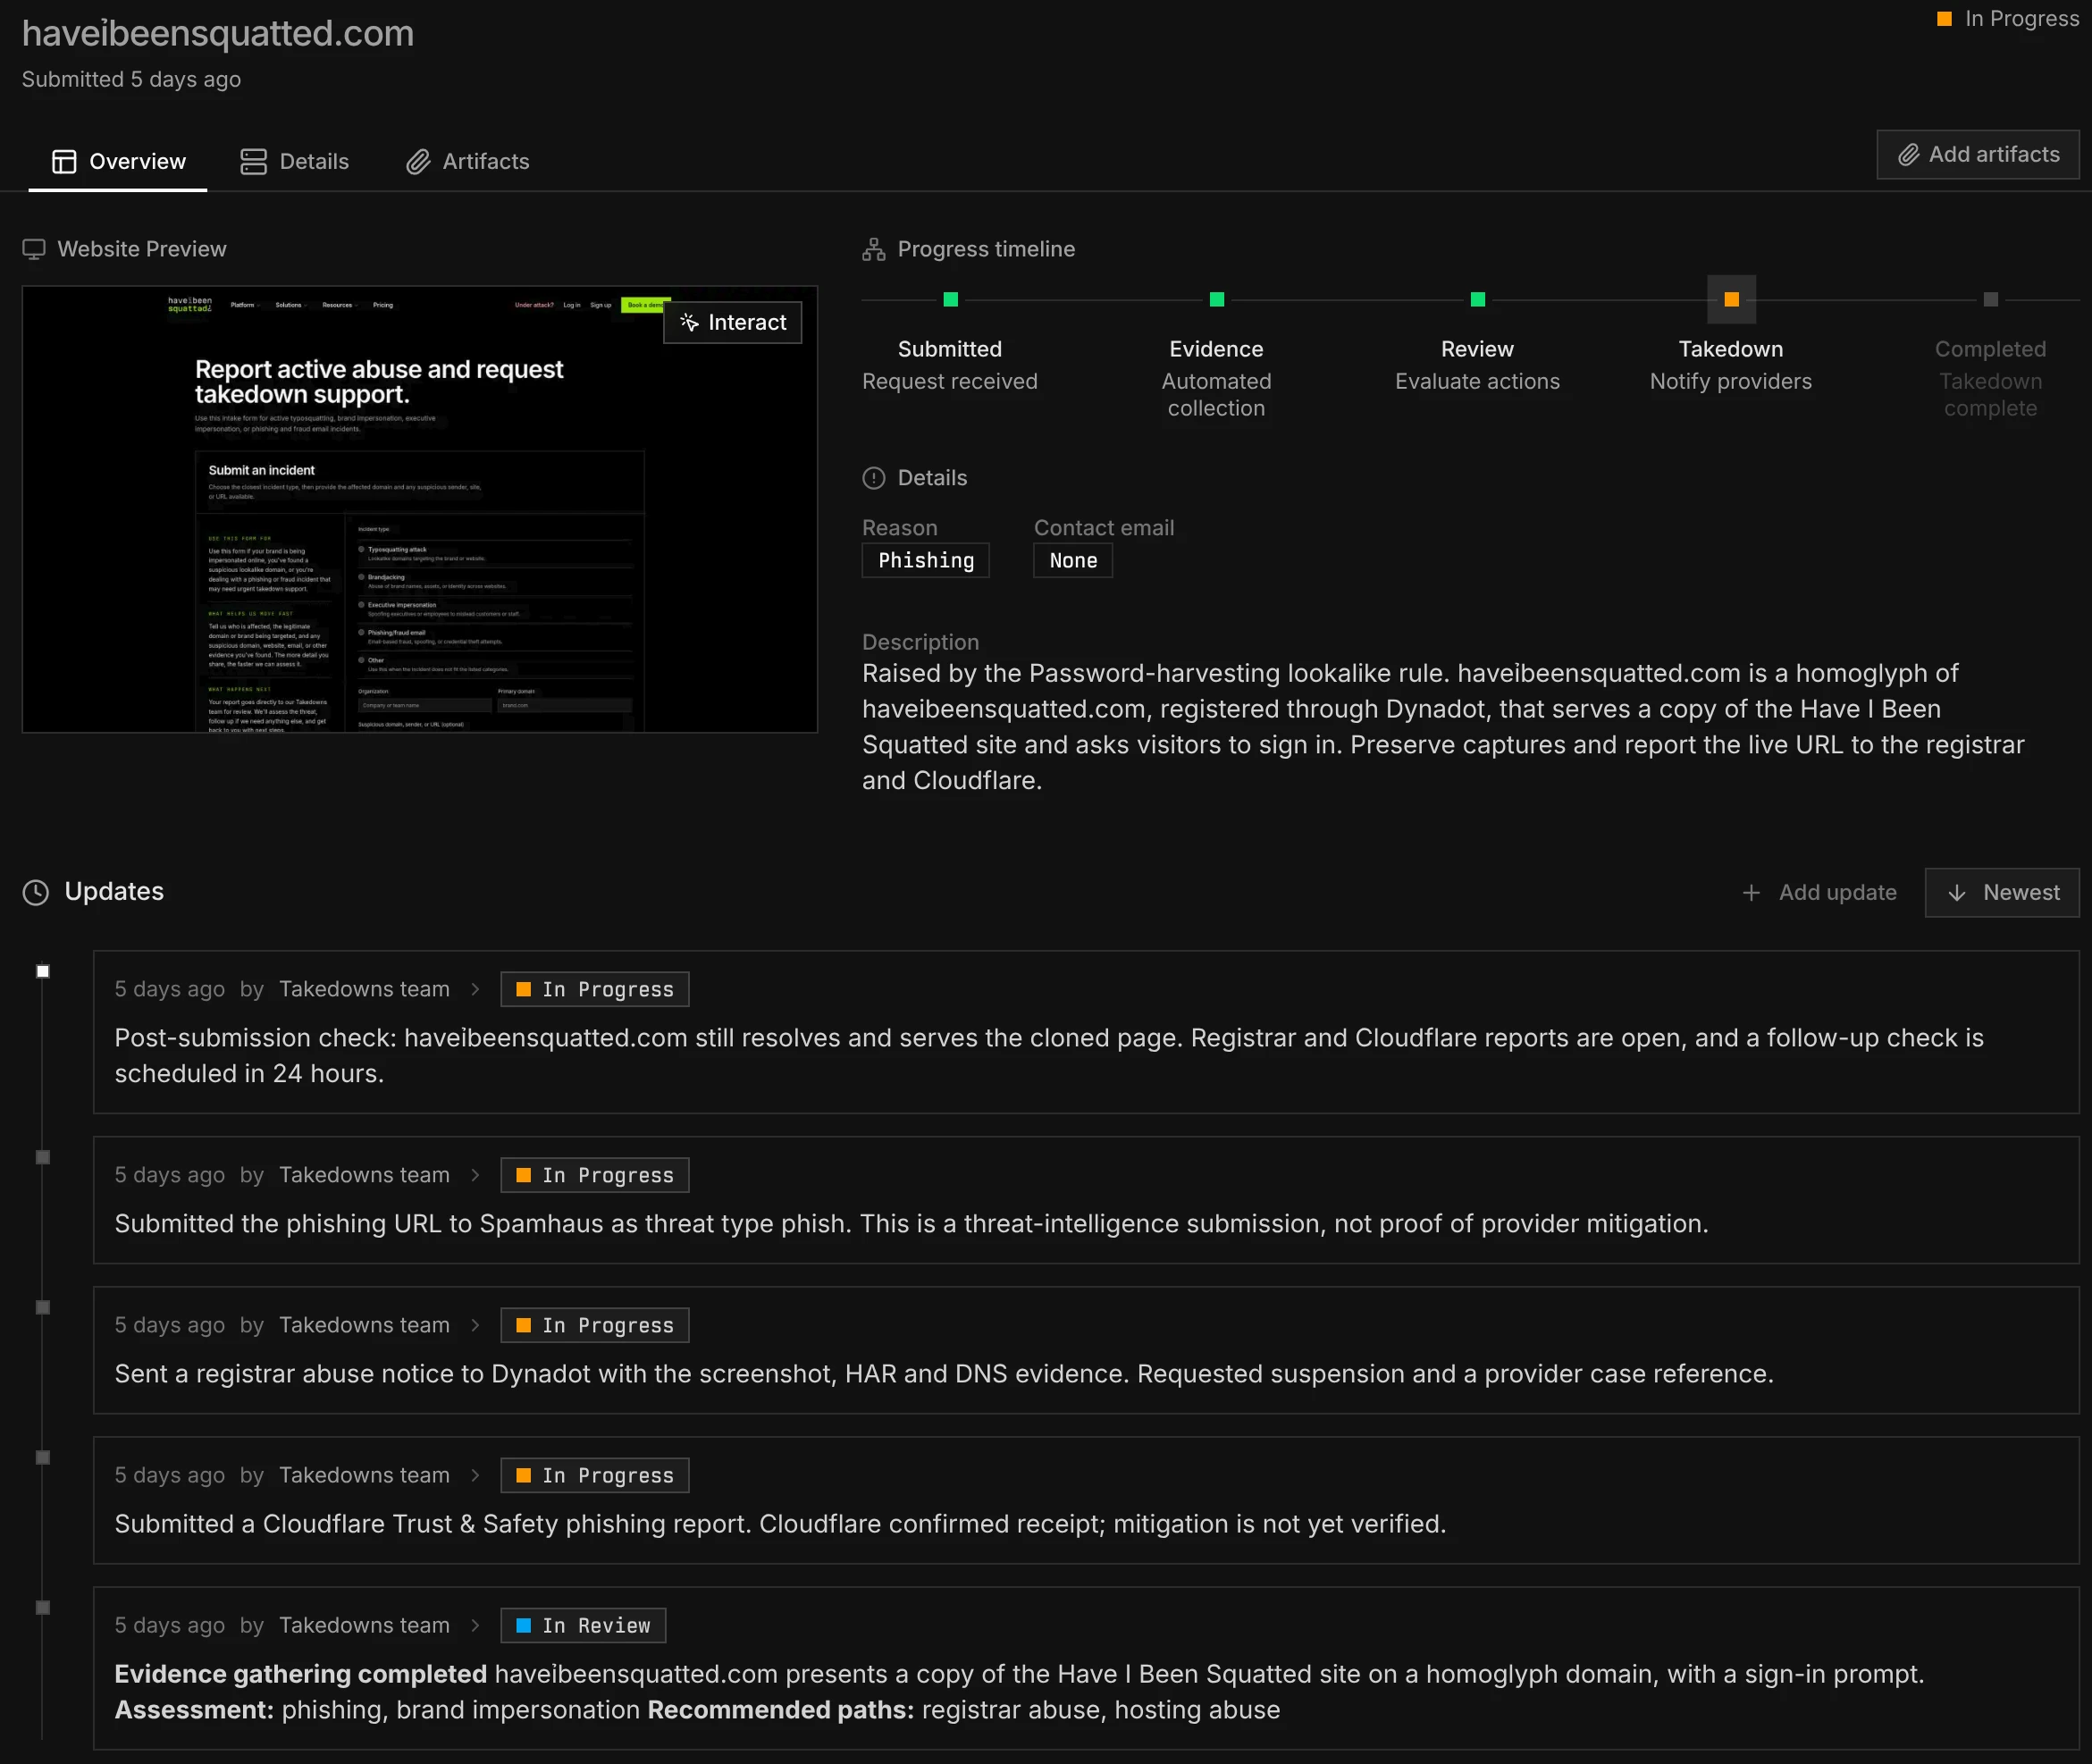
Takedowns
Follow a Takedown from request to outcome.
A demo shows the Takedown case workflow and the Network Enforcement gateways that receive blocks.
Managed takedowns and their targets#
Both products run managed takedowns, and Doppel reaches more kinds of target. Doppel's internal SOC, powered by AI agents and humans, executes every takedown. Customers trigger work with Request Takedown in the product or through the alert API. Doppel states a median under 10 hours across domains, social media and paid ads, and a 12-minute median mitigation for phishing URLs. 2–3,5–6,20,39,42,70–71
Doppel's takedowns go to registrars, hosting providers, DNS, phone carriers, social platforms, ad networks, data broker sites, app stores and crypto listing sites. Have I Been Squatted runs managed Takedowns for domains. An analyst reviews every request, and a rule can open a request automatically. The team reports the domain to its host and registrar, then escalates to ICANN and regional CSIRTs where necessary. The service stops short of legal action and can introduce legal partners. 2–3,5,16,36–39
Choose Doppel when takedowns must cover domains, social profiles, ads, apps or phone numbers. Choose Have I Been Squatted when you want domain rules to request managed Takedowns automatically. 2–3,5,8–11,36–37,39
Where Doppel is the better choice#
Doppel fits when social engineering spans the channels a domain product does not cover and you want them in one platform, with human-risk products such as simulation and email security alongside. Its Threat Graph suits buyers who need linked entity graphs across channels, where Have I Been Squatted's investigations stay with domain observations. Doppel is venture-backed and reports raising a Series C round. 1,3–5,24,43–44,46,48,72–73
It also suits buyers who want analysts to review alerts and handle disruption for them. Doppel publishes median takedown and mitigation times, and it documents a public API with webhooks into the security stack. Doppel reports SOC 2 Type II and ISO/IEC 27001, 27701 and 42001. Doppel is bought through a demo and a quote. 1–2,6,20,23,29,42,66,74–75
Where Have I Been Squatted is the better choice#
Have I Been Squatted suits a security team that tracks malicious domains and the attacker infrastructure behind them, and wants to set and enforce the response itself. Your team writes rules in the Upsilon query language or adopts maintained library rules. A match can alert, reach Splunk, Elastic Security or Microsoft Sentinel, block the domain or request a managed Takedown, which the team reports to the host and registrar. Network Enforcement puts those blocks in Zscaler, Cloudflare Zero Trust, iboss or Microsoft Defender for Endpoint, and Network Intelligence shows which flagged domains devices on your network reached. 7–16,30–32,36–38,67
Lookalikes of your own domains are the first way in. Domain Monitoring watches your domains continuously, generating lookalikes of named kinds such as homoglyphs, bitsquats and TLD swaps alongside certificate transparency and newly registered domains. Analyze inspects any other domain on demand. Each result can carry RDAP registration, DNS records, mail readiness and open ports, and an analyst can open a live page in an isolated browser session. 9–10,16–19,21–22,56–59
Monitoring, hunting tools, rules and alerts are self-serve with a free trial. Takedowns and the email, network, SIEM and canary products are bought through sales. For security review, Have I Been Squatted has a SOC 2 Type II report, available through its Trust Center, and audit logging sits beside Google, Microsoft 365 and SAML single sign-on. PDF reports such as the "Compliance readout", and CSV or JSON exports, take findings to stakeholders. End users can add the free Browser Protection extension for Chrome. 16–17,21,24,28,37,63–64,67,76–77
Have I Been Squatted does not suit a buyer who needs social media, app-store and ad monitoring alongside domains. Doppel brings those channels into the same platform. 1,3,40–41
FAQ#
Yes, if its brand-alert and analyst-review workflow meets your needs. Doppel monitors lookalike domains inside Brand Protection, with analyst review before customer confirmation. Have I Been Squatted instead gives your team domain rules, enrichment and connector actions to run the work itself. 1–3,8–15,20,23,29
Yes. Both run managed takedowns with analyst involvement. Doppel covers more targets beyond domains and publishes median turnaround claims across channels. Have I Been Squatted reports domains to their hosts and registrars. An admin requests a Takedown from a lookup result or an alert, and a rule can request one automatically. 2–3,5–6,16,20,36–39,70
Sources and corrections
Each numbered marker on this page links to its sources below. Each source shows the date it was last checked. If a fact is wrong or out of date, send a correction. A correction is checked against the source and the page is updated.
- 1.Doppel. “Get Alerts (product and queue enums).” Accessed . https://doppel.readme.io/reference/get-alerts
- 2.Doppel. “Executive Protection.” Accessed . https://www.doppel.com/product/executive-protection
- 3.Doppel. “Integrations.” Accessed . https://www.doppel.com/integrations
- 4.Doppel. “Campaign-Level Threat Visibility.” Accessed . https://www.doppel.com/solutions/use-cases/campaign-level-threat-visibility
- 5.Doppel. “Doppel vs. Legacy DRP.” Accessed . https://www.doppel.com/compare/legacy-drp
- 6.Doppel. “Introducing Doppel Threat Graph.” Accessed . https://www.doppel.com/blog/introducing-doppel-threat-graph-powering-graph-driven-defense
- 7.Have I Been Squatted. “Homepage (footer tagline).” Accessed . https://haveibeensquatted.com/
- 8.Have I Been Squatted. “Rules engine guide.” Accessed . https://docs.haveibeensquatted.com/guides/rules-engine/
- 9.Have I Been Squatted. “Domain signals.” Accessed . https://docs.haveibeensquatted.com/reference/signals/domain/
- 10.Have I Been Squatted. “Changelog.” Accessed . https://haveibeensquatted.com/changelog
- 11.Have I Been Squatted. “Network Intelligence guide.” Accessed . https://docs.haveibeensquatted.com/features/network-intelligence/
- 12.Have I Been Squatted. “Network Enforcement.” Accessed . https://haveibeensquatted.com/platform/network-enforcement
- 13.Have I Been Squatted. “Domain feed integration.” Accessed . https://docs.haveibeensquatted.com/integrations/domain-feed/
- 14.Have I Been Squatted. “CrowdStrike Falcon integration.” Accessed . https://docs.haveibeensquatted.com/integrations/crowdstrike-falcon/
- 15.Have I Been Squatted. “Microsoft Defender for Endpoint integration.” Accessed . https://docs.haveibeensquatted.com/integrations/microsoft-defender-endpoint/
- 16.Have I Been Squatted. “Pricing.” Accessed . https://haveibeensquatted.com/pricing
- 17.Have I Been Squatted. “Agents.” Accessed . https://haveibeensquatted.com/platform/agents
- 18.Have I Been Squatted. “Access control reference.” Accessed . https://docs.haveibeensquatted.com/reference/access-control/
- 19.Have I Been Squatted. “MCP server.” Accessed . https://docs.haveibeensquatted.com/ai/mcp/
- 20.Doppel. “Brand Protection.” Accessed . https://www.doppel.com/product/brand-protection
- 21.Have I Been Squatted. “Domain Monitoring.” Accessed . https://haveibeensquatted.com/platform/monitoring
- 22.Have I Been Squatted. “Domain monitoring guide.” Accessed . https://docs.haveibeensquatted.com/features/domain-monitoring/
- 23.Doppel. “Doppel Documentation index.” Accessed . https://doppel.readme.io/llms.txt
- 24.Have I Been Squatted. “Atlas investigations.” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/
- 25.Have I Been Squatted. “Atlas investigations (shareable view links).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#read-the-map
- 26.Have I Been Squatted. “Atlas investigations (New investigation flow).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#start-an-investigation
- 27.Have I Been Squatted. “Atlas investigations (add domains and indicators).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#steer-an-investigation
- 28.Have I Been Squatted. “Administration guide.” Accessed . https://docs.haveibeensquatted.com/guides/administration/
- 29.Doppel. “Create Protected Asset.” Accessed . https://doppel.readme.io/reference/create-protected-asset
- 30.Have I Been Squatted. “Integrations.” Accessed . https://haveibeensquatted.com/platform/integrations
- 31.Have I Been Squatted. “Alert digest guide.” Accessed . https://docs.haveibeensquatted.com/guides/digest/
- 32.Have I Been Squatted. “Connectors.” Accessed . https://docs.haveibeensquatted.com/integrations/
- 33.Doppel. “IOC Updated Webhook.” Accessed . https://doppel.readme.io/reference/ioc_updated
- 34.Doppel. “Jira Integration Instructions.” Accessed . https://www.doppel.com/docs/jira-integration
- 35.Doppel. “Doppel and Filigran Announce Integration.” Accessed . https://www.doppel.com/company/press-releases/doppel-and-filigran-announce-integration-strengthen-threat-intelligence
- 36.Have I Been Squatted. “Takedowns.” Accessed . https://haveibeensquatted.com/platform/takedowns
- 37.Have I Been Squatted. “Takedowns guide.” Accessed . https://docs.haveibeensquatted.com/features/takedowns/
- 38.Have I Been Squatted. “FAQ (stalled takedowns).” Accessed . https://haveibeensquatted.com/faq#takedowns-stall
- 39.Doppel. “Lookalike Domain Monitoring (Doppel section).” Accessed . https://www.doppel.com/blog/lookalike-domain-monitoring
- 40.Have I Been Squatted. “Solutions.” Accessed . https://haveibeensquatted.com/solutions
- 41.Have I Been Squatted. “Brand protection.” Accessed . https://haveibeensquatted.com/solutions/brand-protection
- 42.Doppel. “Request a Demo.” Accessed . https://www.doppel.com/request-a-demo
- 43.Doppel. “Digital Risk Protection (DRP).” Accessed . https://www.doppel.com/solutions/digital-risk-protection
- 44.Doppel. “Rewiring Threat Intel: How Doppel's Graph Engine Maps Social Engineering at Scale.” Accessed . https://www.doppel.com/blog/rewiring-threat-intel-how-doppels-graph-engine-maps-social-engineering-scale
- 45.Doppel. “Email Security.” Accessed . https://www.doppel.com/product/email-security
- 46.Doppel. “Doppel Email Security Now Generally Available.” Accessed . https://www.doppel.com/company/press-releases/doppel-email-security-generally-available
- 47.Doppel. “Phishing Triage.” Accessed . https://www.doppel.com/product/phishing-triage
- 48.Doppel. “Simulation.” Accessed . https://www.doppel.com/product/simulation
- 49.Doppel. “Security Awareness Training.” Accessed . https://www.doppel.com/product/security-awareness-training
- 50.Have I Been Squatted. “Email Intelligence guide.” Accessed . https://docs.haveibeensquatted.com/features/email-intelligence/
- 51.Have I Been Squatted. “Email Intelligence.” Accessed . https://haveibeensquatted.com/platform/email-intelligence
- 52.Have I Been Squatted. “Site Canaries guide.” Accessed . https://docs.haveibeensquatted.com/features/site-canaries/
- 53.Doppel. “Get Alert (API reference).” Accessed . https://doppel.readme.io/reference/get-alert
- 54.Doppel. “Submit Scan Url.” Accessed . https://doppel.readme.io/reference/submit_scan
- 55.Doppel. “Minutes, Not Hours: What Our OpenAI Case Study Proves.” Accessed . https://www.doppel.com/blog/minutes-not-hours-what-our-openai-case-study-proves-about-social-engineering-defense
- 56.Have I Been Squatted. “API: Analyze a URL.” Accessed . https://docs.haveibeensquatted.com/guides/api/analyze/#analyze-a-url
- 57.Have I Been Squatted. “Tools: Analyze (URL analysis note, served without sign-in).” Accessed . https://haveibeensquatted.com/app/tools?mode=analyze
- 58.Have I Been Squatted. “Atlas observations: registration data by TLD.” Accessed . https://mcp.haveibeensquatted.com/mcp
- 59.Have I Been Squatted. “Platform.” Accessed . https://haveibeensquatted.com/platform
- 60.Have I Been Squatted. “Passive DNS guide.” Accessed . https://docs.haveibeensquatted.com/features/passive-dns/
- 61.Spamhaus. “Spamhaus passive DNS endpoint, unauthenticated probe.” Accessed . https://beta-pdns.spamhaus.com/api/v3/login
- 62.Have I Been Squatted. “Rule field catalog (classification fields).” Accessed .
- 63.Have I Been Squatted. “Reports guide.” Accessed . https://docs.haveibeensquatted.com/features/reports/
- 64.Have I Been Squatted. “Explore guide.” Accessed . https://docs.haveibeensquatted.com/features/explore/
- 65.Doppel. “Authentication.” Accessed . https://doppel.readme.io/docs/authentication
- 66.Doppel. “Migrating to V2.” Accessed . https://doppel.readme.io/docs/migrating-to-v2
- 67.Have I Been Squatted. “Network Intelligence.” Accessed . https://haveibeensquatted.com/platform/network-intelligence
- 68.Have I Been Squatted. “Slack app.” Accessed . https://docs.haveibeensquatted.com/ai/slack/
- 69.Have I Been Squatted. “MCP server (OAuth scopes).” Accessed . https://docs.haveibeensquatted.com/ai/mcp/#oauth-scopes
- 70.Doppel. “Request a takedown.” Accessed . https://doppel.readme.io/docs/request-takedown
- 71.Doppel. “Doppel Platform.” Accessed . https://www.doppel.com/platform
- 72.Doppel. “Doppel Raises $70M Series C.” Accessed . https://www.doppel.com/company/press-releases/doppel-raises-series-c-to-meet-rising-demand-for-ai-driven-social-engineering-defense
- 73.Fortune. “Exclusive: Doppel raises $70 million Series C at more than $600 million valuation.” Accessed . https://fortune.com/2025/11/19/exclusive-doppel-raises-70-million-series-c-at-more-than-600-million-valuation-to-fight-ai-powered-social-engineering-attacks/
- 74.Doppel. “Security at Doppel.” Accessed . https://www.doppel.com/security
- 75.Doppel. “Doppel Among First 350 Organizations Worldwide to Achieve ISO 42001 Certification.” Accessed . https://www.doppel.com/company/press-releases/doppel-among-first-350-organizations-worldwide-achieve-iso-42001
- 76.Have I Been Squatted. “Security.” Accessed . https://haveibeensquatted.com/about/security
- 77.Have I Been Squatted. “Browser Protection.” Accessed . https://docs.haveibeensquatted.com/browser-protection/
- 78.Have I Been Squatted. “Webhooks.” Accessed . https://docs.haveibeensquatted.com/integrations/webhooks/