- Choose PhishFort for analyst-led detection and removal across domains, apps and social accounts, or for a one-off takedown of an incident you already found. 1–8
- Choose Have I Been Squatted when your own team investigates malicious domains and the infrastructure behind them, inspects them in a live, isolated browser session and sets the response, from rules to blocks. 9–19
- Use both if PhishFort handles social, app and dark web cases while your security team keeps domain rules and response in its own stack, with one agreed owner for domain takedown requests. 2,6,10–17,20–25
At a glance#
| Have I Been Squatted | PhishFort | |
|---|---|---|
| What you get | ||
| What you get | Detection and response for malicious domains9 | Managed brand protection and takedown service6 |
| Lookalike discovery | ||
| Lookalike discovery | Permutations, certificate transparency, newly registered domains, business context26–27 | New domains, new certificates, search data, threat feeds4 |
| Alert triage | ||
| Alert triage | Maintained and custom domain rules10–13 | SOC validates suspicious domains, apps and impersonations1 |
| Response in your tools | ||
| Response in your tools | ||
| Managed takedowns | ||
| Managed takedowns | Domains, social, apps, phone, email, IP, ads, legal routes2–6 | |
| Beyond domains | ||
| Beyond domains | Not covered: social, apps, dark web36–37 | |
| How you buy | ||
| How you buy | Quote-based managed service7 | |
Who investigates suspicious domains#
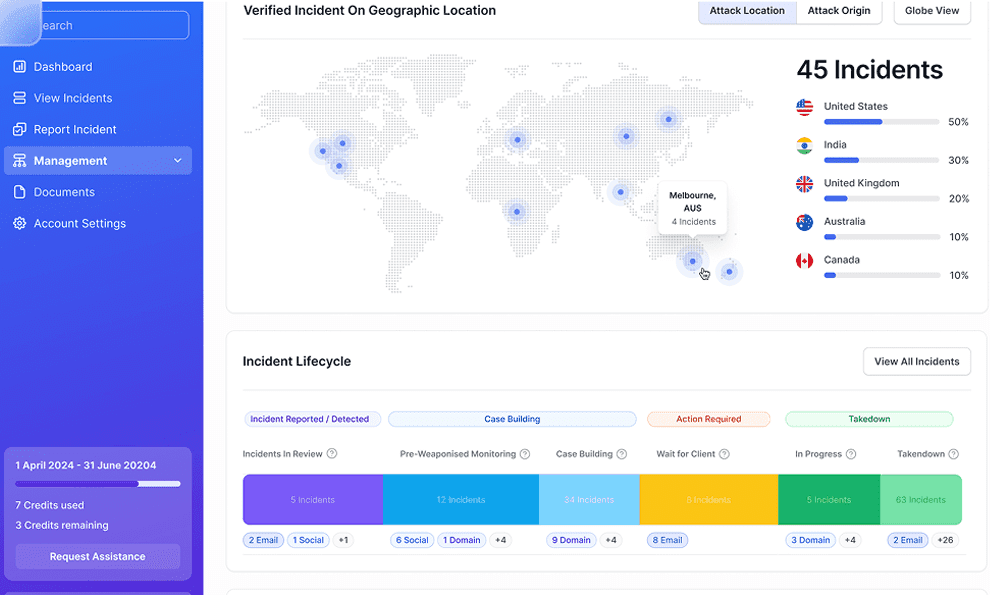
PhishFort analysts validate suspected threats, and Have I Been Squatted gives your own team the evidence and rules to investigate them. PhishFort's managed monitoring scans newly registered domains from popular top-level domains, newly issued SSL certificates, search engine data and threat intelligence feeds. It combines machine learning with analyst review, and incidents reach the dashboard as Monitor or Malicious cases. PhishFort states that its SOC validates every suspicious domain, app or impersonation. 1,4,10–13
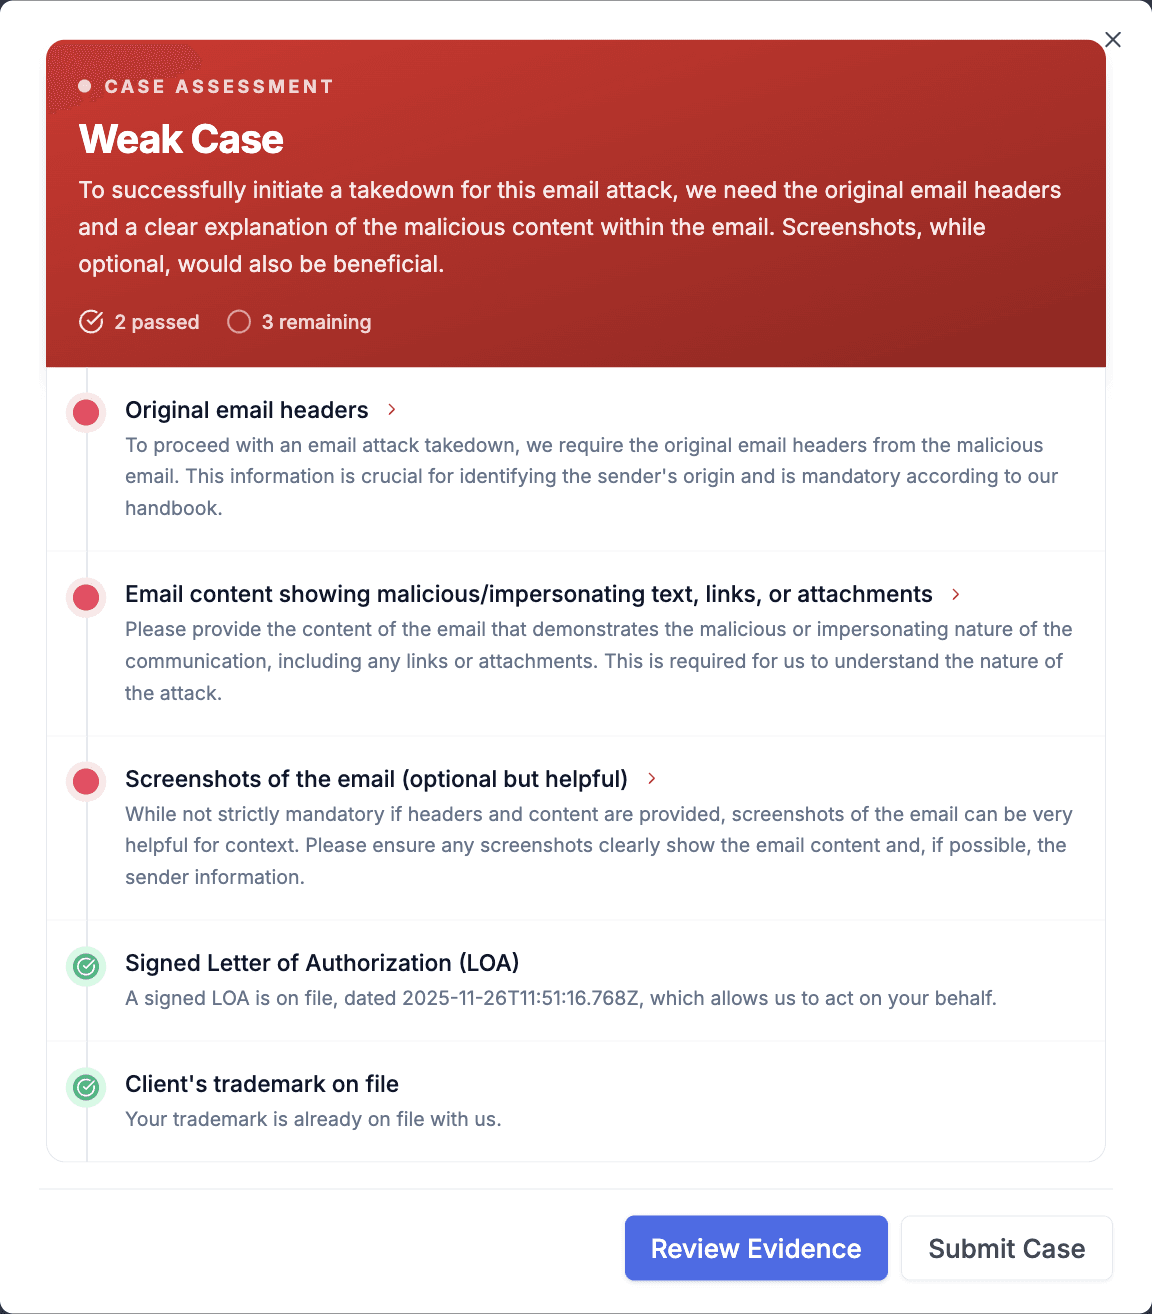
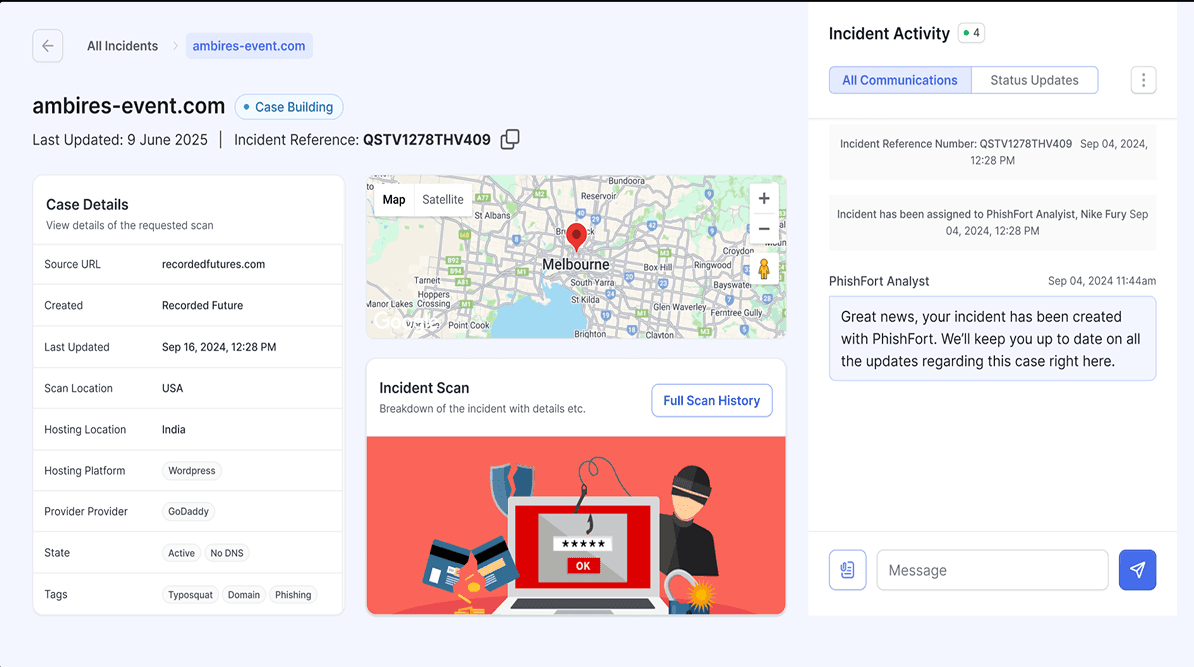
When a customer reports an incident, Automated Incident Review rates the case as strong or weak for progression and names missing evidence before submission. Case pages show status, evidence, registrar responses and notes from the assigned analyst. Incident snapshots record DNS, WHOIS and TLS certificate state, and richer captures can add hosting, redirect and page-count fields plus ssdeep and screenshot hashes for correlating similar incidents. 1,20,38–42
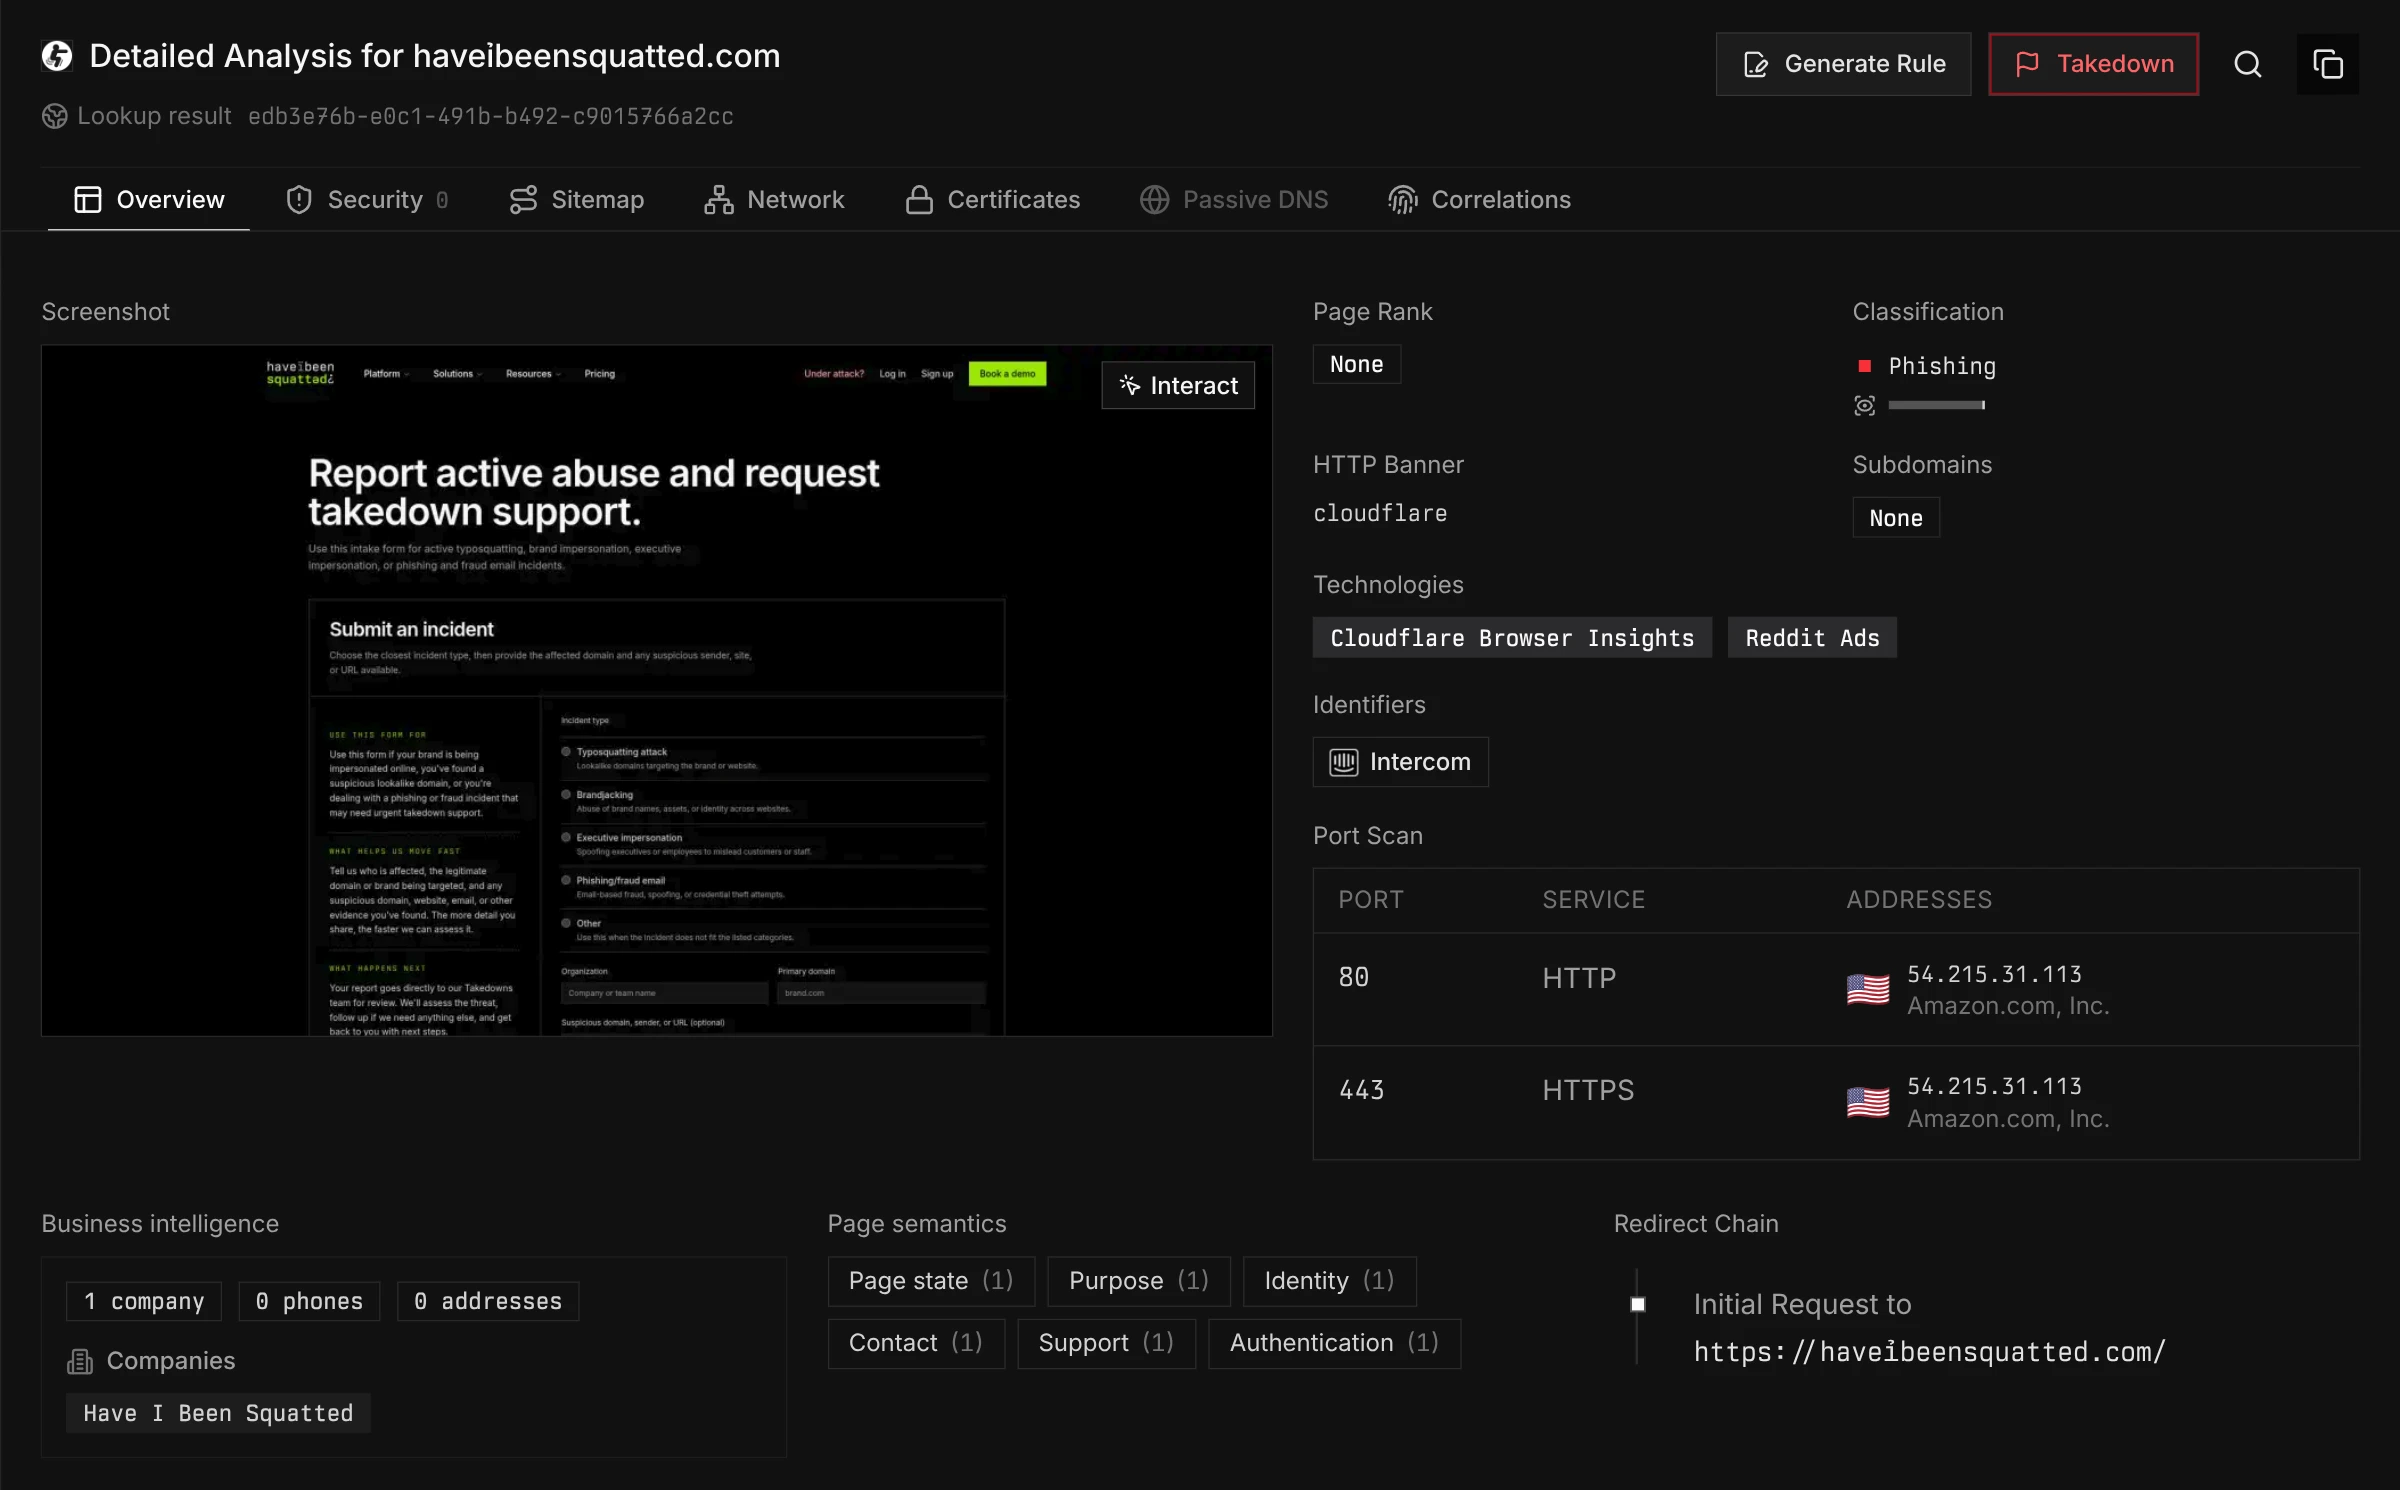
Have I Been Squatted gives your analysts the domain evidence to inspect. Discovery combines generated lookalikes, with named kinds such as homoglyphs, bitsquats and TLD swaps, with certificate transparency and newly registered domains. Results can include RDAP registration data, hosting details, DNS records, mail readiness, open ports and a capture of the website. An analyst can check whether a lookalike resolves, is set up for email or serves a copied page, then open it in an isolated browser. 11–12,18–19,26–27,35,43–47
Both products look past a single domain to the infrastructure behind it. PhishFort states that it clusters related domains, wallets, apps and emails and groups persistent campaigns. No public documentation of a customer pivot or graph tool was found. 6,20,48
Have I Been Squatted puts that pivot in your team's hands. Analyze inspects any domain on demand, and Atlas investigations, in early access, start from a described hunt and any domains you already suspect, then follow shared infrastructure through Atlas, the store of domain observations. An investigation keeps watching after the first pass, shows results in views such as Tree, Table, Clusters and Flows, and exports STIX 2.1, CSV or JSON. 12,19,25,35,46–47,49–56
Acting on a finding in your own tools#
Both products connect to your tools, but they carry different work. PhishFort's Client API and signed webhooks let your team report incidents, follow case status in its own tools and approve takedowns when the account requires it. PhishFort's marketing names Splunk, Sentinel and ServiceNow among its SIEM and ticketing destinations, and the documented Zendesk connector is one the customer builds and hosts. PhishFort's MCP server serves documentation only, and an API MCP server is listed as coming soon. 1,7,20,31–33,57–60
Have I Been Squatted puts automated response in rules over domain signals, taken from a maintained library or written by your team. A rule can raise an alert, deliver the finding to a SIEM, push the domain to a block list or request a Takedown. It can also mark each matched result with a status such as Malicious and a note. An admin can also send one result to a connected tool as a notification, SIEM finding or block without writing a rule. Network Enforcement sends flagged domains to gateways, endpoints, mail filters and a hosted domain feed. An MCP server lets agents work the same alerts and Takedowns, and every write needs an admin. 10–17,28–30,35,50,52,55,61–62
PhishFort states that its enterprise IOC feed is available in STIX, JSON, CSV or custom API formats. No public documentation of PhishFort customer-written detection rules or of direct push to a customer's gateway or EDR was found. 6,20,39,57,59,63–64
Have I Been Squatted publishes its own feed and shows whether a flagged domain reached your network. The hosted domain feed serves rule-flagged domains in seven formats, among them STIX 2.1, CSV and JSON, with documented setup for MISP. Network Intelligence reads Microsoft Defender every 15 seconds and Cloudflare Gateway every minute, so your team can see which flagged domains devices on its network reached before deciding how to respond. 10,13,15,28–30,65
Coverage beyond lookalike domains#
PhishFort's managed service reaches well past domains. Its takedown service covers phishing sites, lookalike domains, fake apps and impersonation accounts, with incident types for social profiles, phone numbers, apps, browser extensions and IP addresses. PhishFort also monitors the dark web for leaked credentials and brand mentions, and offers executive protection, an abuse mailbox that triages phishing reports and a partner blocklist of analyst-confirmed phishing domains. 2–6,20–23,33,63
PhishFort analysts handle validation and filing across these channels. A brand or fraud team can hand those cases to one service, and an MSP can run the same service for its clients. PhishFort says it fits best when customers face fake sites, apps and accounts and want them removed without running a platform themselves. 2,4–7,20–23,58–59,66
Have I Been Squatted concentrates on domains and the threats built on them. Domain Monitoring generates lookalikes and watches certificate transparency and newly registered domains. Email Intelligence adds mail telemetry from Microsoft 365 and Google Workspace, and Site Canaries flag copies of your own pages. Have I Been Squatted does not monitor social media, app stores, the dark web, ads or leaked credentials. 26–27,35–37,67–69
Takedowns
Follow a Takedown from request to outcome.
A demo shows the Takedown case workflow and the Network Enforcement gateways that receive blocks.
Managed takedowns and their targets#
Both products offer managed takedowns with analyst review. PhishFort analysts validate and file. Customers report incidents in the dashboard or through the API, and PhishFort decides the action. The full service is sold on a quote-based contract that packages detection, analyst validation, takedowns and reporting. Single takedowns can also be bought without a subscription, from a public per-takedown price list. 7–8,24–25,35,58–59
PhishFort pairs removal requests with submissions to partner blocklists, including Google Safe Browsing, Cloudflare, VirusTotal and Spamhaus. Cases go to registrars, hosts, app stores and social platforms. Contracted legal services cover trademark and copyright, and PhishFort describes UDRP disputes and DMCA notices, with a Letter of Authorization for DMCA. 2–6,24,35,70
For MSP buyers, PhishFort's terms set a 12-hour deadline to start takedown work and a separate Safe Browsing insertion target, with a fee reduction when it is missed. The same terms report a median takedown time of six hours for phishing cases with enough evidence at the last audit, and they do not guarantee an outcome or a completion time. PhishFort's Trezor case study reports 29,000 or more takedowns for that customer at a 99.76% success rate. 4,6–8,22,24,71–72
Have I Been Squatted runs managed Takedowns for domains. An analyst reviews every request, and a rule can open a request automatically. The team reports the domain to its host and registrar, then escalates to ICANN and regional CSIRTs where necessary. The service stops short of legal action and can introduce legal partners. 24–25,34–35
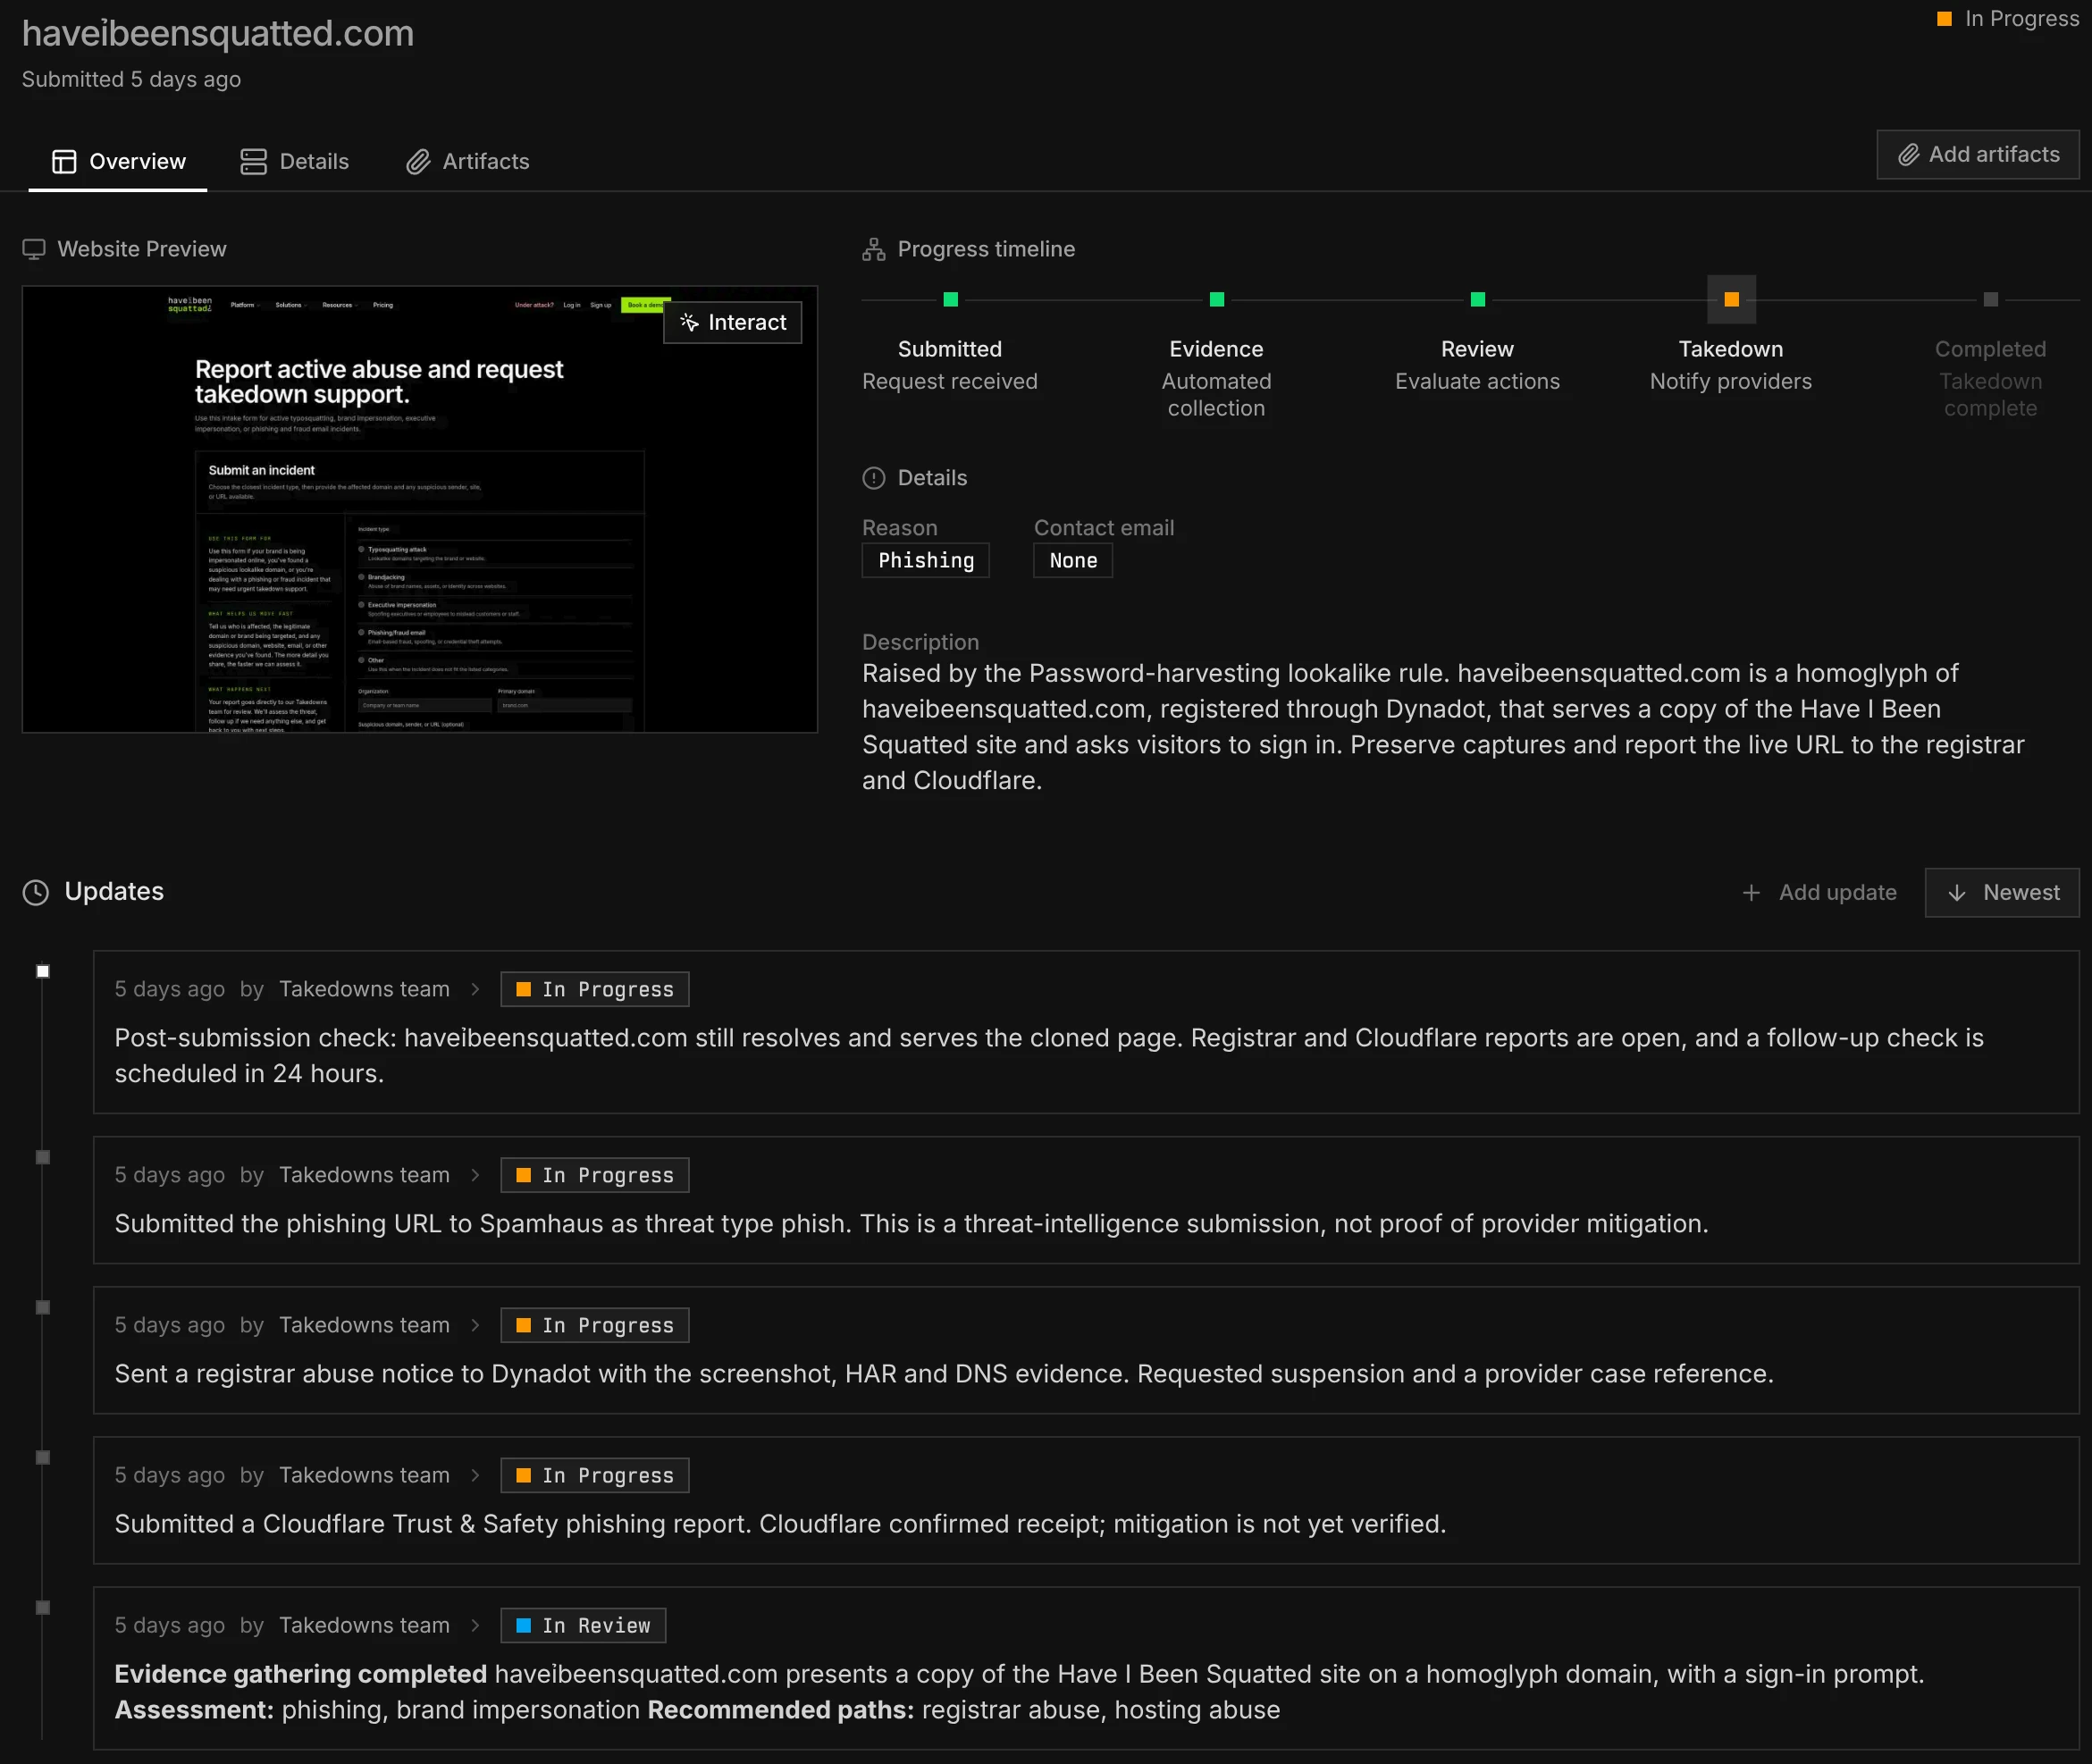
Choose PhishFort when a case can move from a domain to a social profile, an app store listing or a legal filing. Choose Have I Been Squatted when the case is a malicious domain and you want the Takedown tied to the monitoring and rules that found it. 2–6,10–13,24–25,34–35
Where PhishFort is the better choice#
PhishFort fits a brand, fraud or security team that wants one managed service for domains, social impersonation, rogue apps and dark web credential exposure. Buyers who need a single removal can buy an Individual Takedown at a published price. PhishFort refunds an unsuccessful takedown, less card fees, but does not refund a cancellation, and a false positive can bring a penalty fee. PhishFort notes that those purchases include no continuous monitoring, so detection still depends on the buyer's own team or on customer reports. 2,4,6–8,20–25,35,73
It also suits MSPs and security platforms that want PhishFort to run detection and takedowns while they keep the client relationship. The API gives partners parent and reseller roles scoped to each client, and the program offers co-branded client reports. Buyers who need blocklist submission and legal routes in the same service get both. Recorded Future's own documentation states that PhishFort operates its Takedown API, and PhishFort announces SOC 2 Type II attestation. 2–5,24,35,66,70,74–76
Where Have I Been Squatted is the better choice#
Choose Have I Been Squatted when your own analysts work malicious domains and the attacker infrastructure behind them, and pick the response for each. Rules come from the maintained library or are written by your team in the Upsilon query language. A match can alert, send the finding to a SIEM, block the domain in Cloudflare Zero Trust, Zscaler or Microsoft Defender for Endpoint, or request a Takedown. Each Takedown request still gets an analyst's review before the team reports the domain to its host and registrar. 9–17,24–25,28–30,34–35
Your analysts can also inspect any domain themselves, whether it is a lookalike of your own or one that Analyze or an Atlas investigation, in early access, turned up. Results can carry RDAP registration, DNS records, hosting, mail readiness and open ports, and when a domain serves a page, an analyst can open it in a live, isolated browser session. Network Intelligence shows which flagged domains devices on your network reached. 11–13,18–19,26–27,43,46–47,49–51,53–54,65
Monitoring starts without a sales call. Domain Monitoring keeps checking your domains continuously, and it is self-serve with the hunting tools, rules and alerts, starting from a free trial. Takedowns and the email, network, SIEM and canary products are bought through sales. For security review, Have I Been Squatted has a SOC 2 Type II report, available through its Trust Center. Members sign in through Google, Microsoft 365 or SAML single sign-on, with audit logging, and PDF reports or CSV and JSON exports hand findings to stakeholders. End users can add the free Browser Protection extension for Chrome. 25–27,35,46,52,55–56,65,77–79
Have I Been Squatted does not suit a buyer whose main need is social impersonation, rogue-app removal or dark web monitoring. PhishFort brings those channels into its managed service. 2,6,20–25,36–37
FAQ#
Yes. Both run managed takedowns with analyst review. PhishFort covers more targets beyond domains and submits to partner blocklists while work proceeds. Have I Been Squatted reports domains to their hosts and registrars. An admin requests a Takedown from a lookup result or an alert, and a rule can request one automatically. 2–7,24–25,34–35,58–59
Choose Have I Been Squatted if your team wants to investigate domains and control its own rules, starting from a self-serve trial, and can add managed Takedowns through sales. Choose PhishFort if you want analysts to run detection and validation, even when your immediate problem is domains. It also covers apps and social impersonation, and sells one-off removals without monitoring. 1–2,6–8,10–13,24–25,35,65
Sources and corrections
Each numbered marker on this page links to its sources below. Each source shows the date it was last checked. If a fact is wrong or out of date, send a correction. A correction is checked against the source and the page is updated.
- 1.PhishFort. “AI-Native Detection Paired with Threat Expertise.” Accessed . https://phishfort.com/capabilities/phishing-detection/
- 2.PhishFort. “Data Structures (Incident Types, Incident Class).” Accessed . https://phishfort.github.io/unified-client-api-docs/structures/
- 3.PhishFort. “Data Structures (BlocklistListing).” Accessed . https://phishfort.github.io/unified-client-api-docs/structures/#blocklistlisting
- 4.PhishFort. “MSP Partner and End-User Terms of Use (last updated 2025-08-04).” Accessed . https://phishfort.com/msp-tos/
- 5.PhishFort. “Brand Protection.” Accessed . https://phishfort.com/product/brand-protection/
- 6.PhishFort. “Managed Phishing and Domain Takedown Service.” Accessed . https://phishfort.com/capabilities/takedowns/
- 7.PhishFort. “Request a Takedown (One-Off Takedown Packages).” Accessed . https://phishfort.com/resources/request-takedown/
- 8.PhishFort. “Individual Takedown Terms and Conditions (last updated 2025-04-01).” Accessed . https://phishfort.com/terms-and-conditions/
- 9.Have I Been Squatted. “Homepage (footer tagline).” Accessed . https://haveibeensquatted.com/
- 10.Have I Been Squatted. “Rules engine guide.” Accessed . https://docs.haveibeensquatted.com/guides/rules-engine/
- 11.Have I Been Squatted. “Domain signals.” Accessed . https://docs.haveibeensquatted.com/reference/signals/domain/
- 12.Have I Been Squatted. “Changelog.” Accessed . https://haveibeensquatted.com/changelog
- 13.Have I Been Squatted. “Network Intelligence guide.” Accessed . https://docs.haveibeensquatted.com/features/network-intelligence/
- 14.Have I Been Squatted. “Network Enforcement.” Accessed . https://haveibeensquatted.com/platform/network-enforcement
- 15.Have I Been Squatted. “Domain feed integration.” Accessed . https://docs.haveibeensquatted.com/integrations/domain-feed/
- 16.Have I Been Squatted. “CrowdStrike Falcon integration.” Accessed . https://docs.haveibeensquatted.com/integrations/crowdstrike-falcon/
- 17.Have I Been Squatted. “Microsoft Defender for Endpoint integration.” Accessed . https://docs.haveibeensquatted.com/integrations/microsoft-defender-endpoint/
- 18.Have I Been Squatted. “Platform.” Accessed . https://haveibeensquatted.com/platform
- 19.Have I Been Squatted. “Access control reference.” Accessed . https://docs.haveibeensquatted.com/reference/access-control/
- 20.PhishFort. “Dark Web Monitoring.” Accessed . https://phishfort.com/product/dark-web-monitoring/
- 21.PhishFort. “Executive Protection.” Accessed . https://phishfort.com/product/executive-protection/
- 22.PhishFort. “PhishFort, Brand Protection and Phishing Takedowns.” Accessed . https://phishfort.com/
- 23.PhishFort. “Dark Web Monitoring release notes, v1.0 (2025-10-14).” Accessed . https://phishfort.com/dark-web-monitoring-v1-release/
- 24.Have I Been Squatted. “Takedowns.” Accessed . https://haveibeensquatted.com/platform/takedowns
- 25.Have I Been Squatted. “Takedowns guide.” Accessed . https://docs.haveibeensquatted.com/features/takedowns/
- 26.Have I Been Squatted. “Domain Monitoring.” Accessed . https://haveibeensquatted.com/platform/monitoring
- 27.Have I Been Squatted. “Domain monitoring guide.” Accessed . https://docs.haveibeensquatted.com/features/domain-monitoring/
- 28.Have I Been Squatted. “Integrations.” Accessed . https://haveibeensquatted.com/platform/integrations
- 29.Have I Been Squatted. “Alert digest guide.” Accessed . https://docs.haveibeensquatted.com/guides/digest/
- 30.Have I Been Squatted. “Connectors.” Accessed . https://docs.haveibeensquatted.com/integrations/
- 31.PhishFort. “Webhooks.” Accessed . https://phishfort.github.io/unified-client-api-docs/webhooks/
- 32.PhishFort. “Zendesk Integration.” Accessed . https://phishfort.github.io/unified-client-api-docs/zendesk/
- 33.PhishFort. “Abuse Mailbox.” Accessed . https://phishfort.com/product/abuse-mailbox/
- 34.Have I Been Squatted. “FAQ (stalled takedowns).” Accessed . https://haveibeensquatted.com/faq#takedowns-stall
- 35.Have I Been Squatted. “Pricing FAQ (takedowns).” Accessed . https://haveibeensquatted.com/pricing
- 36.Have I Been Squatted. “Solutions.” Accessed . https://haveibeensquatted.com/solutions
- 37.Have I Been Squatted. “Brand protection.” Accessed . https://haveibeensquatted.com/solutions/brand-protection
- 38.PhishFort. “Introducing Automated Incident Review (2025-12-05).” Accessed . https://phishfort.com/automated-incident-review-release/
- 39.PhishFort. “Reporting System.” Accessed . https://phishfort.com/capabilities/reporting-system/
- 40.PhishFort. “Incident Snapshots.” Accessed . https://phishfort.github.io/unified-client-api-docs/snapshots/
- 41.PhishFort. “Data Structures (IncidentInsights).” Accessed . https://phishfort.github.io/unified-client-api-docs/structures/#incidentinsights
- 42.PhishFort. “Incident Snapshots (Screenshots).” Accessed . https://phishfort.github.io/unified-client-api-docs/snapshots/#screenshots
- 43.Have I Been Squatted. “Atlas observations: registration data by TLD.” Accessed . https://mcp.haveibeensquatted.com/mcp
- 44.Have I Been Squatted. “Passive DNS guide.” Accessed . https://docs.haveibeensquatted.com/features/passive-dns/
- 45.Spamhaus. “Spamhaus passive DNS endpoint, unauthenticated probe.” Accessed . https://beta-pdns.spamhaus.com/api/v3/login
- 46.Have I Been Squatted. “Atlas investigations.” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/
- 47.Have I Been Squatted. “Atlas investigations (add domains and indicators).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#steer-an-investigation
- 48.PhishFort. “Threat Monitoring That Never Stops.” Accessed . https://phishfort.com/capabilities/brand-monitoring/
- 49.Have I Been Squatted. “API: Analyze a URL.” Accessed . https://docs.haveibeensquatted.com/guides/api/analyze/#analyze-a-url
- 50.Have I Been Squatted. “MCP server (analyze a URL).” Accessed . https://docs.haveibeensquatted.com/ai/mcp/
- 51.Have I Been Squatted. “Tools: Analyze (URL analysis note, served without sign-in).” Accessed . https://haveibeensquatted.com/app/tools?mode=analyze
- 52.Have I Been Squatted. “Agents.” Accessed . https://haveibeensquatted.com/platform/agents
- 53.Have I Been Squatted. “Atlas investigations (shareable view links).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#read-the-map
- 54.Have I Been Squatted. “Atlas investigations (New investigation flow).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#start-an-investigation
- 55.Have I Been Squatted. “Reports guide.” Accessed . https://docs.haveibeensquatted.com/features/reports/
- 56.Have I Been Squatted. “Explore guide.” Accessed . https://docs.haveibeensquatted.com/features/explore/
- 57.PhishFort. “PhishFort Client API.” Accessed . https://phishfort.github.io/unified-client-api-docs/
- 58.PhishFort. “Incident Lifecycle.” Accessed . https://phishfort.github.io/unified-client-api-docs/incident-lifecycle/
- 59.PhishFort. “Approve a Takedown.” Accessed . https://phishfort.github.io/unified-client-api-docs/approve-takedown/
- 60.PhishFort. “Docs MCP Server.” Accessed . https://phishfort.github.io/unified-client-api-docs/mcp-server/
- 61.Have I Been Squatted. “Slack app.” Accessed . https://docs.haveibeensquatted.com/ai/slack/
- 62.Have I Been Squatted. “MCP server (OAuth scopes).” Accessed . https://docs.haveibeensquatted.com/ai/mcp/#oauth-scopes
- 63.PhishFort. “The PhishFort Blocklist.” Accessed . https://phishfort.com/resources/report-phishing/
- 64.PhishFort. “Partner Sharing API (Threat Intel).” Accessed . https://lookup.phishfort.com/docs/partner-sharing/threat-intel
- 65.Have I Been Squatted. “Network Intelligence.” Accessed . https://haveibeensquatted.com/platform/network-intelligence
- 66.PhishFort. “MSP Partner Program.” Accessed . https://phishfort.com/company/msp-partnerships/
- 67.Have I Been Squatted. “Email Intelligence guide.” Accessed . https://docs.haveibeensquatted.com/features/email-intelligence/
- 68.Have I Been Squatted. “Email Intelligence.” Accessed . https://haveibeensquatted.com/platform/email-intelligence
- 69.Have I Been Squatted. “Site Canaries guide.” Accessed . https://docs.haveibeensquatted.com/features/site-canaries/
- 70.PhishFort. “Spamhaus now incorporates our Blocklist (2025-06-05).” Accessed . https://phishfort.com/phishfort-spamhaus-partners/
- 71.PhishFort. “Trezor success case (2026-05-26).” Accessed . https://phishfort.com/success-cases/trezor/
- 72.PhishFort. “Success Cases.” Accessed . https://phishfort.com/resources/success-cases/
- 73.PhishFort. “In-House vs Outsourced Phishing Takedowns (2026-11-02).” Accessed . https://phishfort.com/in-house-vs-outsourced-phishing-domain-takedown/
- 74.PhishFort. “List Users.” Accessed . https://phishfort.github.io/unified-client-api-docs/list-users/
- 75.Recorded Future. “Takedown API.” Accessed . https://docs.recordedfuture.com/reference/takedown-api
- 76.PhishFort. “SOC 2 Type II Attestation Secured (2025-02-14).” Accessed . https://phishfort.com/phishfort-soc-2-type-ii-attestation-soc-compliance/
- 77.Have I Been Squatted. “Security.” Accessed . https://haveibeensquatted.com/about/security
- 78.Have I Been Squatted. “Administration guide.” Accessed . https://docs.haveibeensquatted.com/guides/administration/
- 79.Have I Been Squatted. “Browser Protection.” Accessed . https://docs.haveibeensquatted.com/browser-protection/
- 80.Have I Been Squatted. “Webhooks.” Accessed . https://docs.haveibeensquatted.com/integrations/webhooks/