- Choose CloudSEK XVigil when brand risk spans social pages, rogue apps, credential leaks and the dark web as well as domains, and you want CloudSEK's team to run takedowns beyond domains. 1–7
- Choose Have I Been Squatted to investigate malicious domains down to their redirects, page content and live site, then have a rule block them in Zscaler, Microsoft Defender for Endpoint or Cloudflare Zero Trust. 8–21
- Use both when you need XVigil's wider coverage plus Have I Been Squatted's domain rules and connector actions, with one team owning domain triage and takedown requests. 1–4,10–11,13–14,18–21
At a glance#
| Have I Been Squatted | CloudSEK XVigil | |
|---|---|---|
| Lookalike discovery | ||
| Lookalike discovery | Permutations, certificate transparency, newly registered domains, business context22–23 | |
| Follow-up on known fakes | ||
| Follow-up on known fakes | Scheduled lookups of every monitored domain22 | Fake Domains Observer re-scans on WHOIS, SSL or re-registration25 |
| Evidence to inspect | ||
| Evidence to inspect | Event screenshots and text dumps26 | |
| Mail telemetry | ||
| Mail telemetry | Yes: Microsoft 365 and Google Workspace27–28 | Not found: Not found29 |
| Response in your tools | ||
| Response in your tools | Rules alert, block, annotate and request Takedowns13–17 | API and named SIEM, SOAR and chat integrations29–30 |
| Managed takedowns | ||
| Managed takedowns | Domains, to host and registrar, with escalation31–34 | |
| Beyond domains | ||
| Beyond domains | Not covered: social, apps, dark web, credentials35–36 | Dark web, credentials, social, apps, executive impersonation1–4 |
| How you buy | ||
| How you buy | 12-month contracts on AWS Marketplace2 | |
Coverage beyond lookalike domains#
XVigil suits a team responsible for social impersonation, rogue apps, credential leaks and dark web exposure as well as fake domains. Brand threat monitoring covers fake domains, fake apps, fake customer care numbers and fake social media pages, and deep and dark web monitoring watches forums, marketplaces and paste sites. Data leak monitoring covers leaked credentials, exposed documents and stolen datasets, and buyers can take one module or several. CloudSEK also sells BeVigil for external attack surface management and products for third-party risk, AI attack surface exposure and threat intelligence, and Nexus AI correlates findings across them. 1–3,37–40
Have I Been Squatted concentrates on domains and the threats built on them. Domain Monitoring generates lookalikes and watches certificate transparency and newly registered domains. Email Intelligence connects Microsoft 365 or Google Workspace and matches the sender, recipient and URL domains in your mail to monitored domains, with no MX changes. Site Canaries add a script to your own pages and flag a copy that loads on a hostname you do not recognize. No public documentation of a Microsoft 365 or Google Workspace mailbox integration for XVigil was found. 22–23,27–29,34,41–42
Finding and investigating lookalike domains#
XVigil's Fake Domain Finder uses monitored assets and watchwords to find suspected impersonation domains, and CloudSEK describes an in-house permutation engine for typosquatting. Fake Domains Observer re-scans known fakes after a WHOIS change, an SSL certificate update or a repurchase, so analysts can revisit a dormant domain when its infrastructure changes. Event evidence can include screenshots and text dumps. 3,24–26
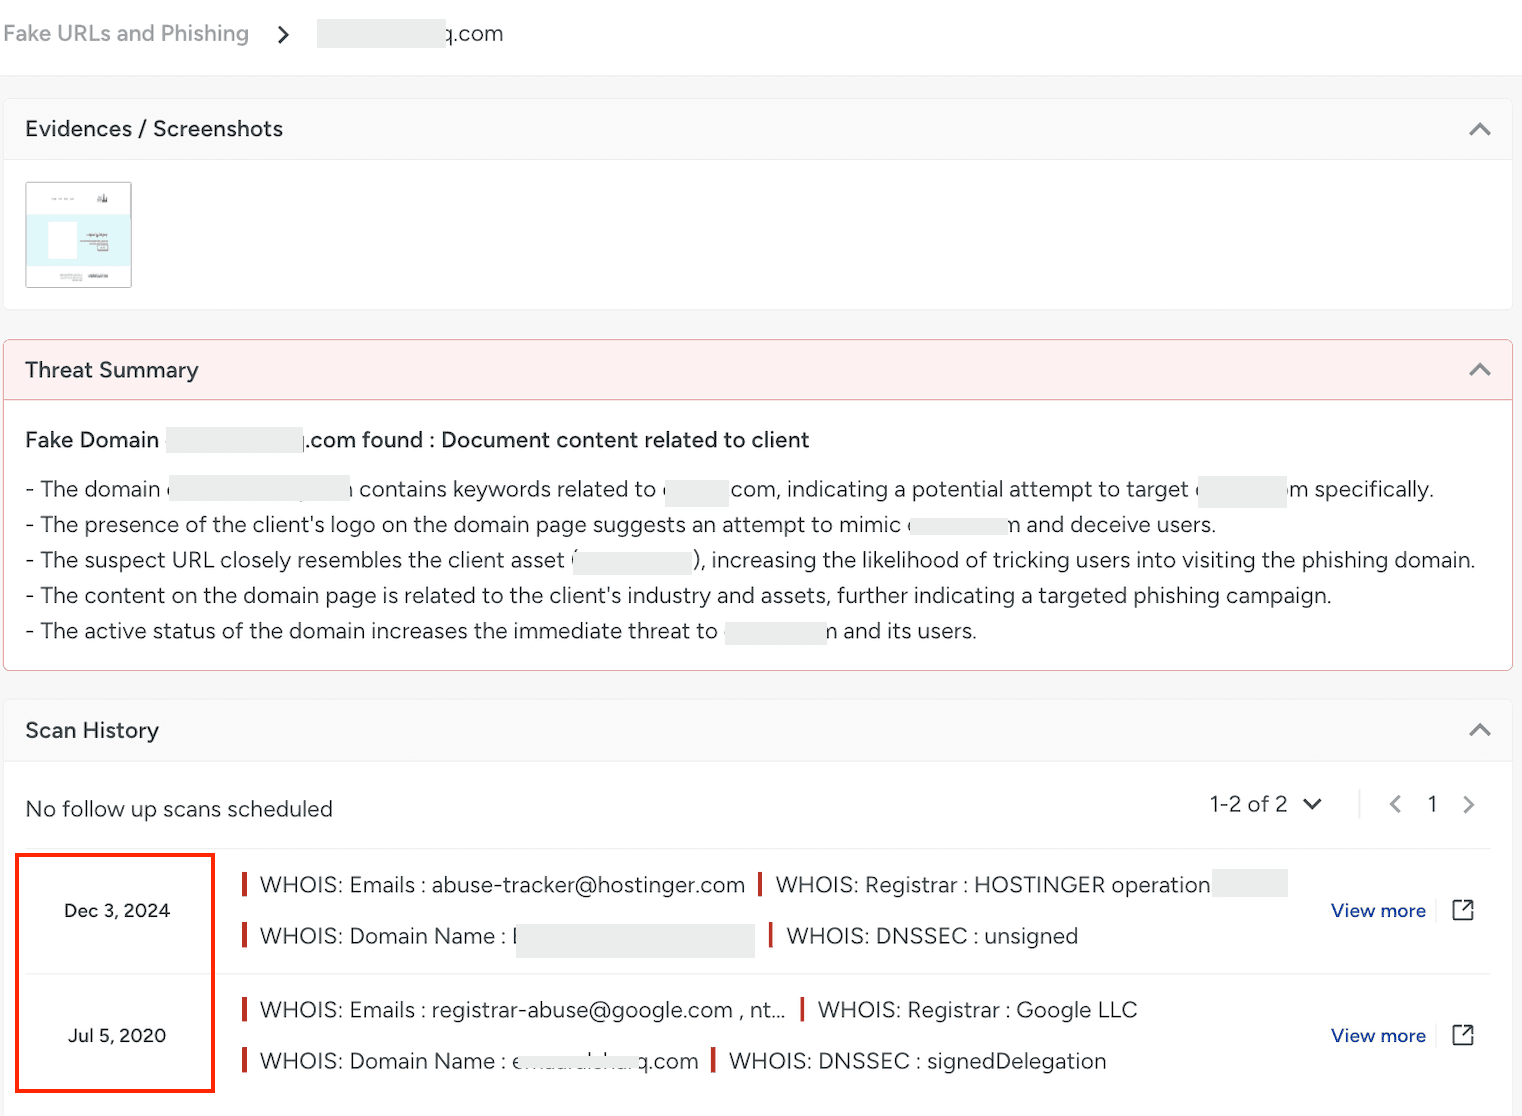
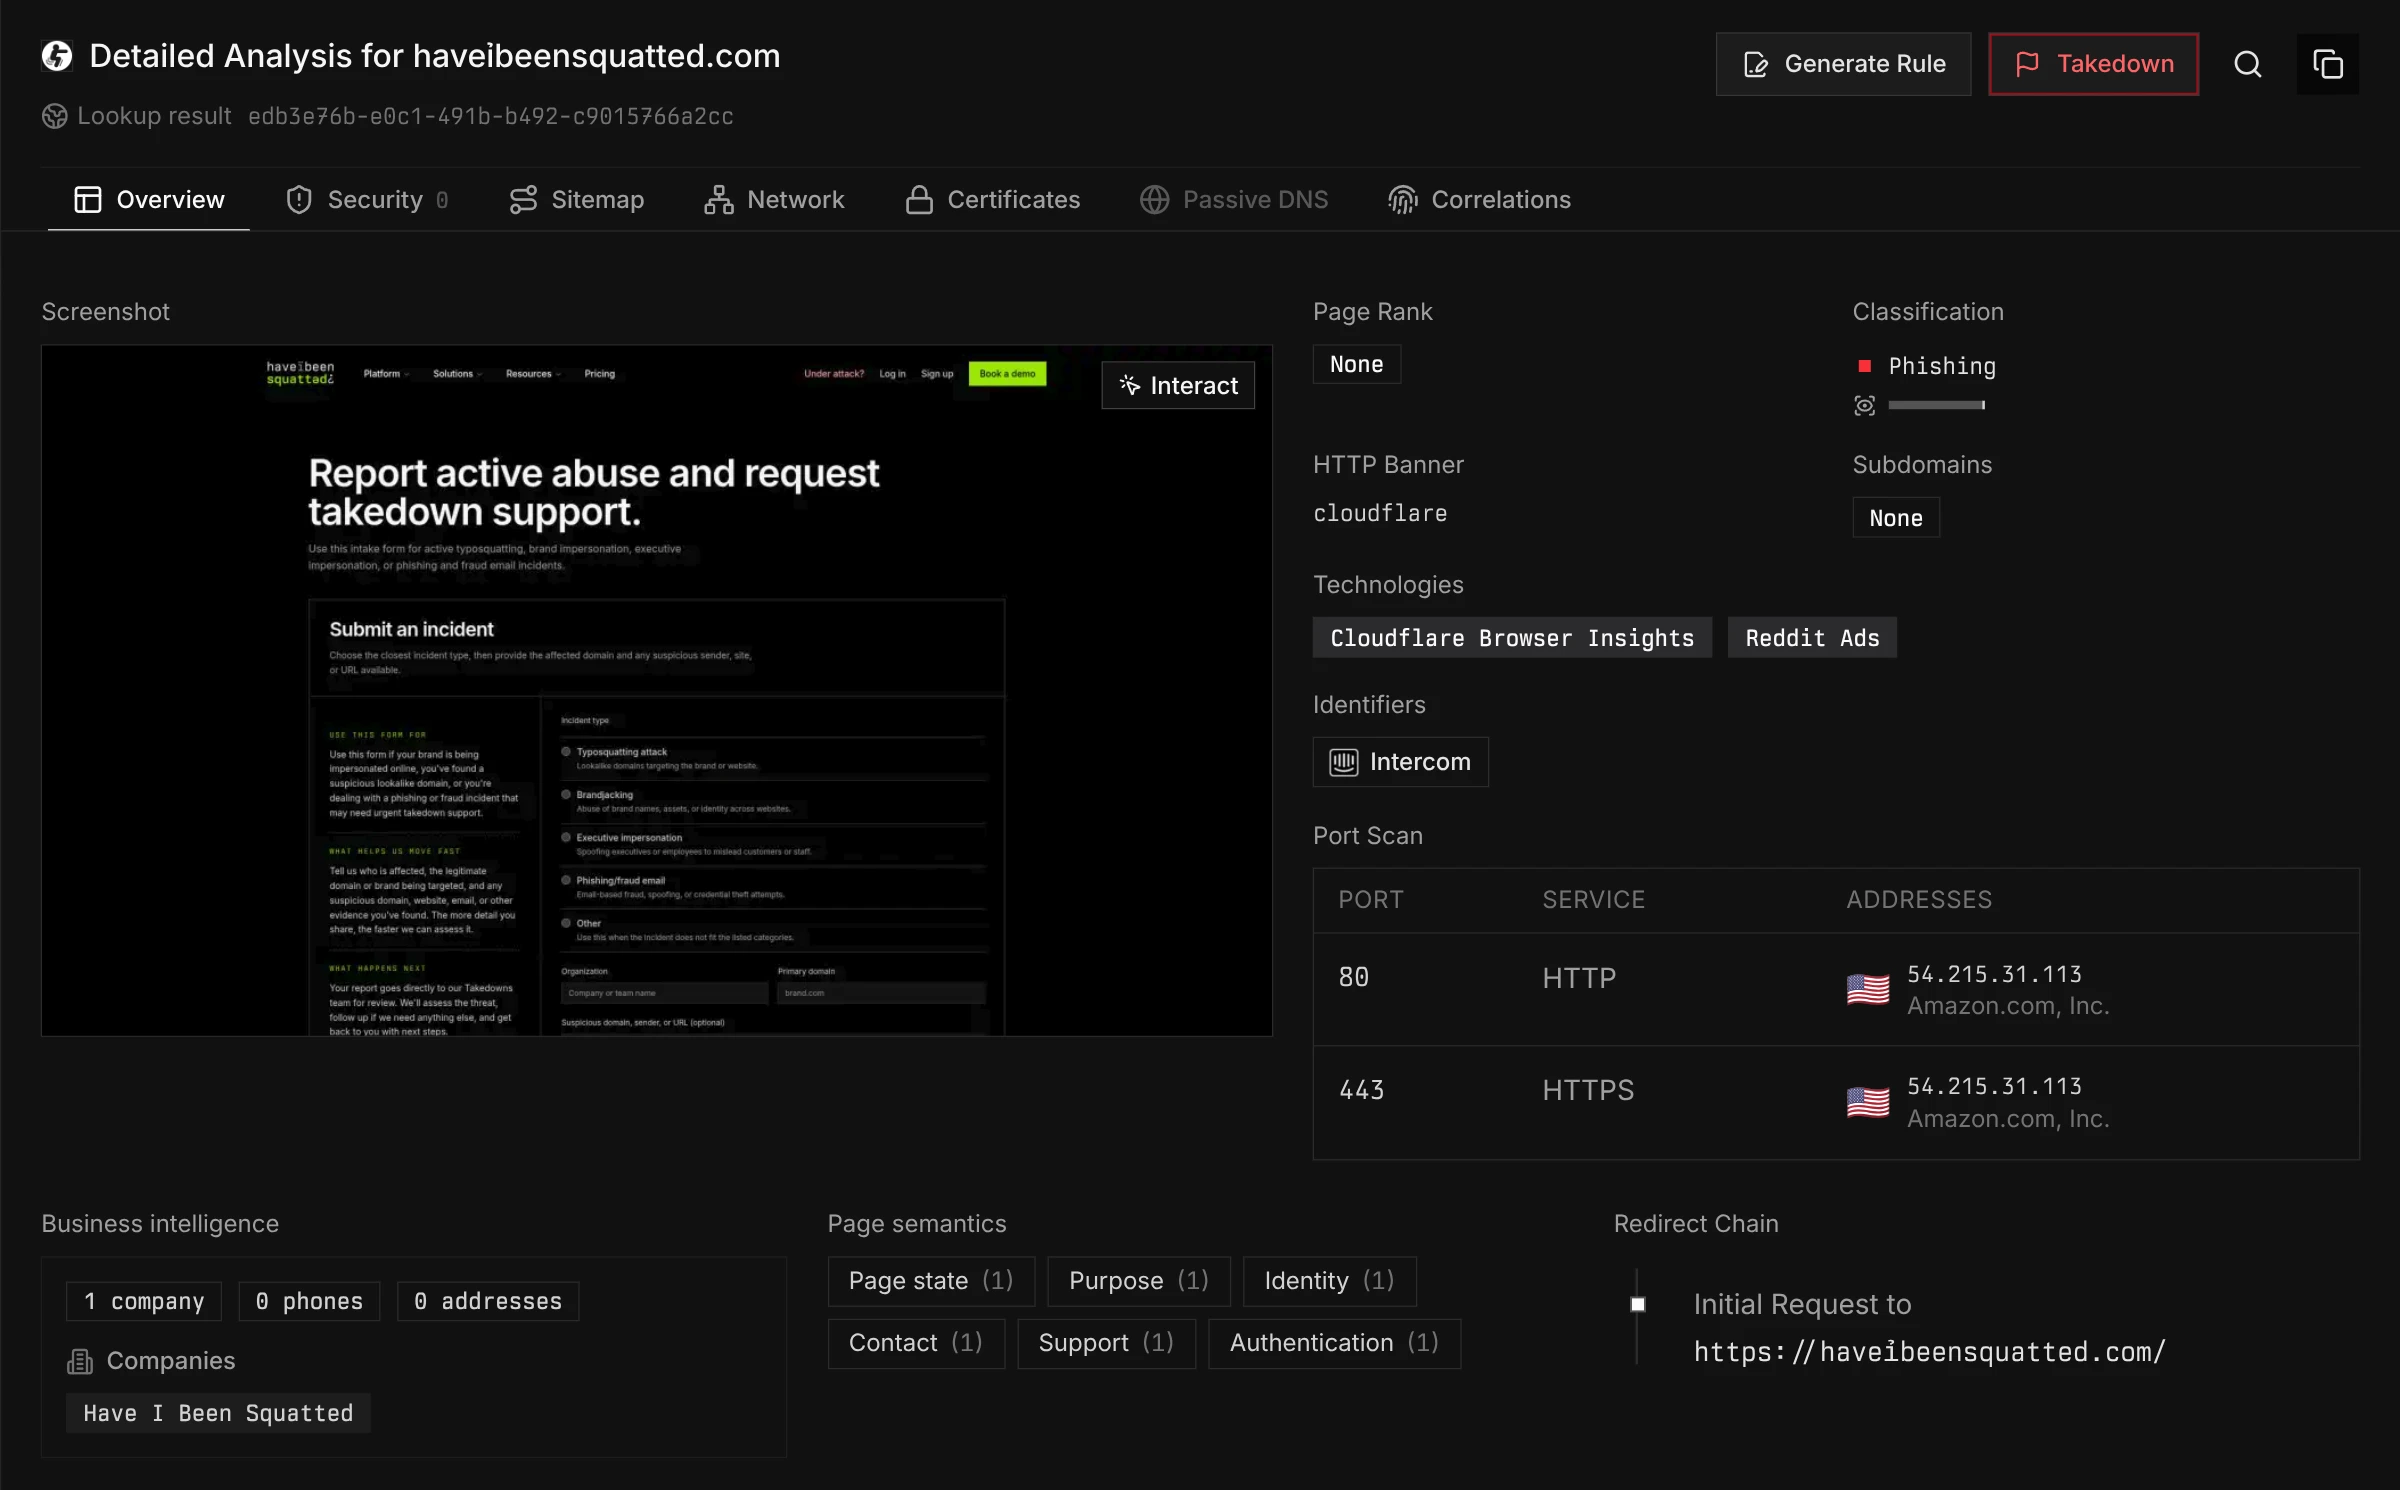
Have I Been Squatted gives your analysts the domain evidence to inspect. Discovery combines generated lookalikes, with named kinds such as homoglyphs, bitsquats and TLD swaps, with certificate transparency and newly registered domains. Have I Been Squatted states that each monitored domain gets a lookup at least once every 24 hours. Each result can include RDAP registration data, hosting details, DNS records, mail readiness, open ports and a website capture, and an analyst can open the site in an isolated browser. 9–12,22–23,34,43–47
The two products suit different investigation habits. XVigil's Observer suits analysts who revisit known fakes after infrastructure changes. Have I Been Squatted suits analysts who check DNS, mail readiness and page evidence before they choose a response. 9–12,22–23,25,34,44–47
To connect threats, CloudSEK's Nexus AI links leaked credentials, lookalike domains and phishing pages into a potential attack path. That view joins findings across CloudSEK's modules, which suits a team that tracks credentials and domains together. 1,39
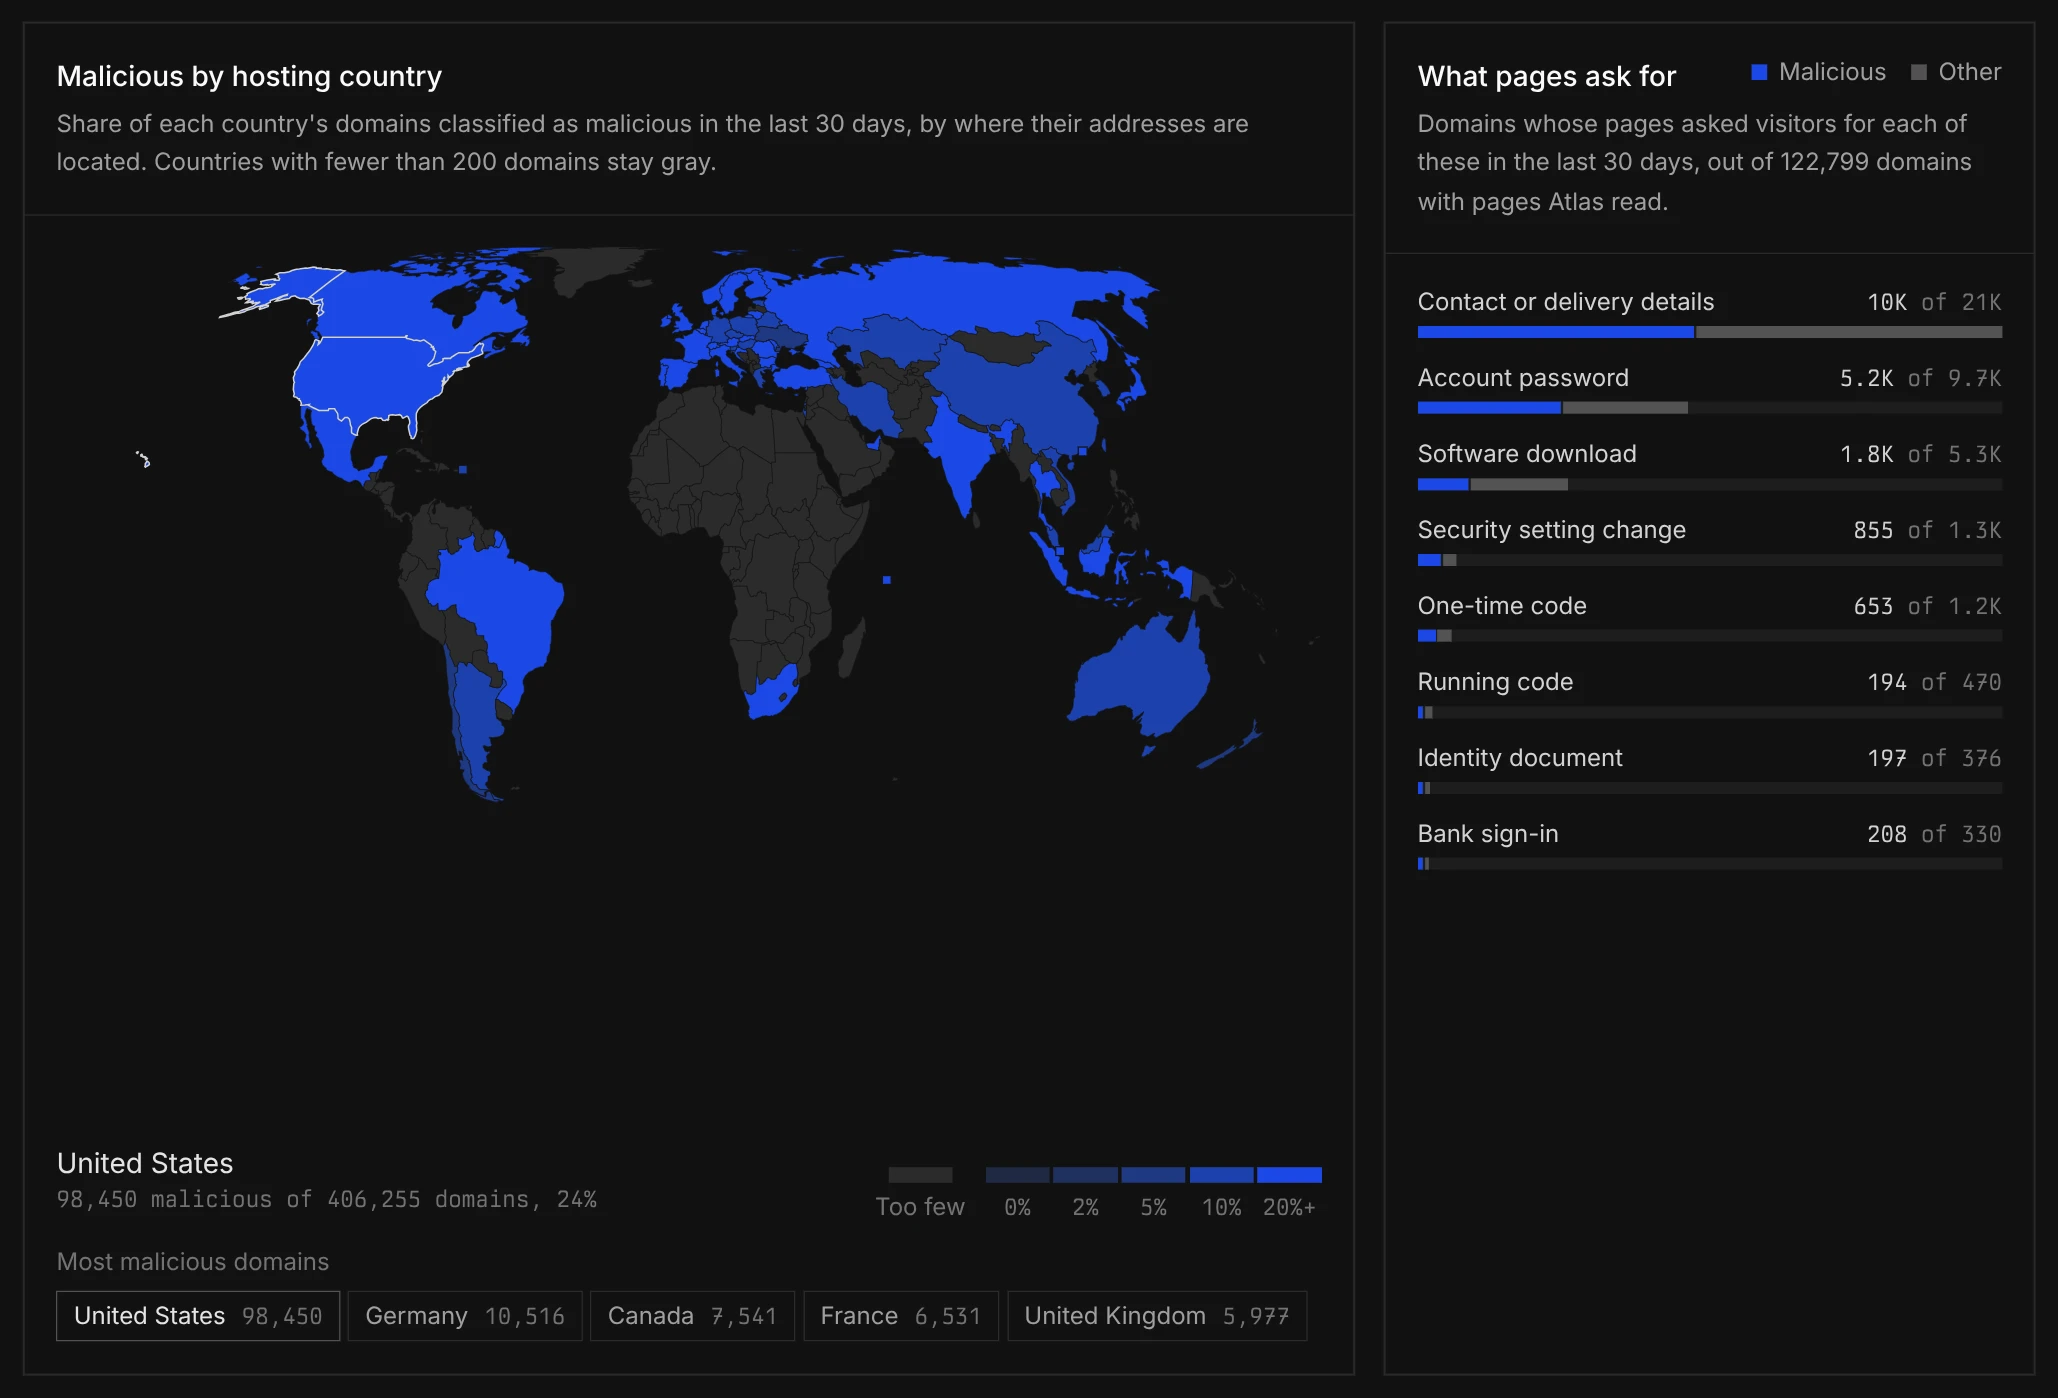
Have I Been Squatted pivots on the infrastructure itself through Atlas investigations, in early access. An investigation begins from a hunt you describe, optionally seeded with up to 25 domains you already suspect, and follows shared infrastructure across Atlas, the store of domain observations. An admin can add indicators such as IP addresses, nameservers or favicon hashes for it to pivot on. It keeps running after the first pass, re-checking its rarest values every six hours, and lays results out in views such as Tree, Table, Clusters and Flows. Findings export as STIX 2.1, CSV or JSON. 32,46–51
Acting on a finding in your own tools#
XVigil connects to the security stack through a two-way Integrations API and named connectors. CloudSEK lists SIEM, SOAR, ticketing and chat apps among more than 50 applications, plus STIX and TAXII feeds. The pull-based API reads alerts and writes status, assignee, comments and remediation back to CloudSEK records. For CloudSEK customers, a hosted Model Context Protocol (MCP) server lets AI clients read alerts and evidence and update incidents and events in bulk, and each analyst connects with their own token. No public documentation was found of a takedown request through the API or MCP server, or of a direct push from XVigil into secure web gateways. 3,5,7,26,29–30,52–56
Have I Been Squatted puts response in rules that run over domain signals. A maintained rules library covers common detections, and your team can add its own. One rule can raise an alert, deliver the finding to a SIEM, push the domain to a block list, annotate the result with a status such as Malicious, or request a Takedown. Network Enforcement sends flagged domains to gateways, endpoints, mail filters and a hosted domain feed. The Have I Been Squatted MCP server covers lookups, monitoring queries, rules, alerts, Takedowns, response dispatch, result annotation and documentation search, and every write needs an organization admin. 10–11,13–21,34,50,57–60
During evaluation, follow one finding into your SIEM and through the response you need, such as a ticket, a block or a Takedown request. With XVigil, the ticket comes through a connector such as ServiceNow, and the takedown starts in the CloudSEK portal. The block runs in your own tools, for example through a SOAR connector or a reader for CloudSEK's STIX or TAXII feeds. With Have I Been Squatted, one rule can deliver the finding, push the block and open the Takedown request. 3,5,7,13–15,26,29–30
Takedowns
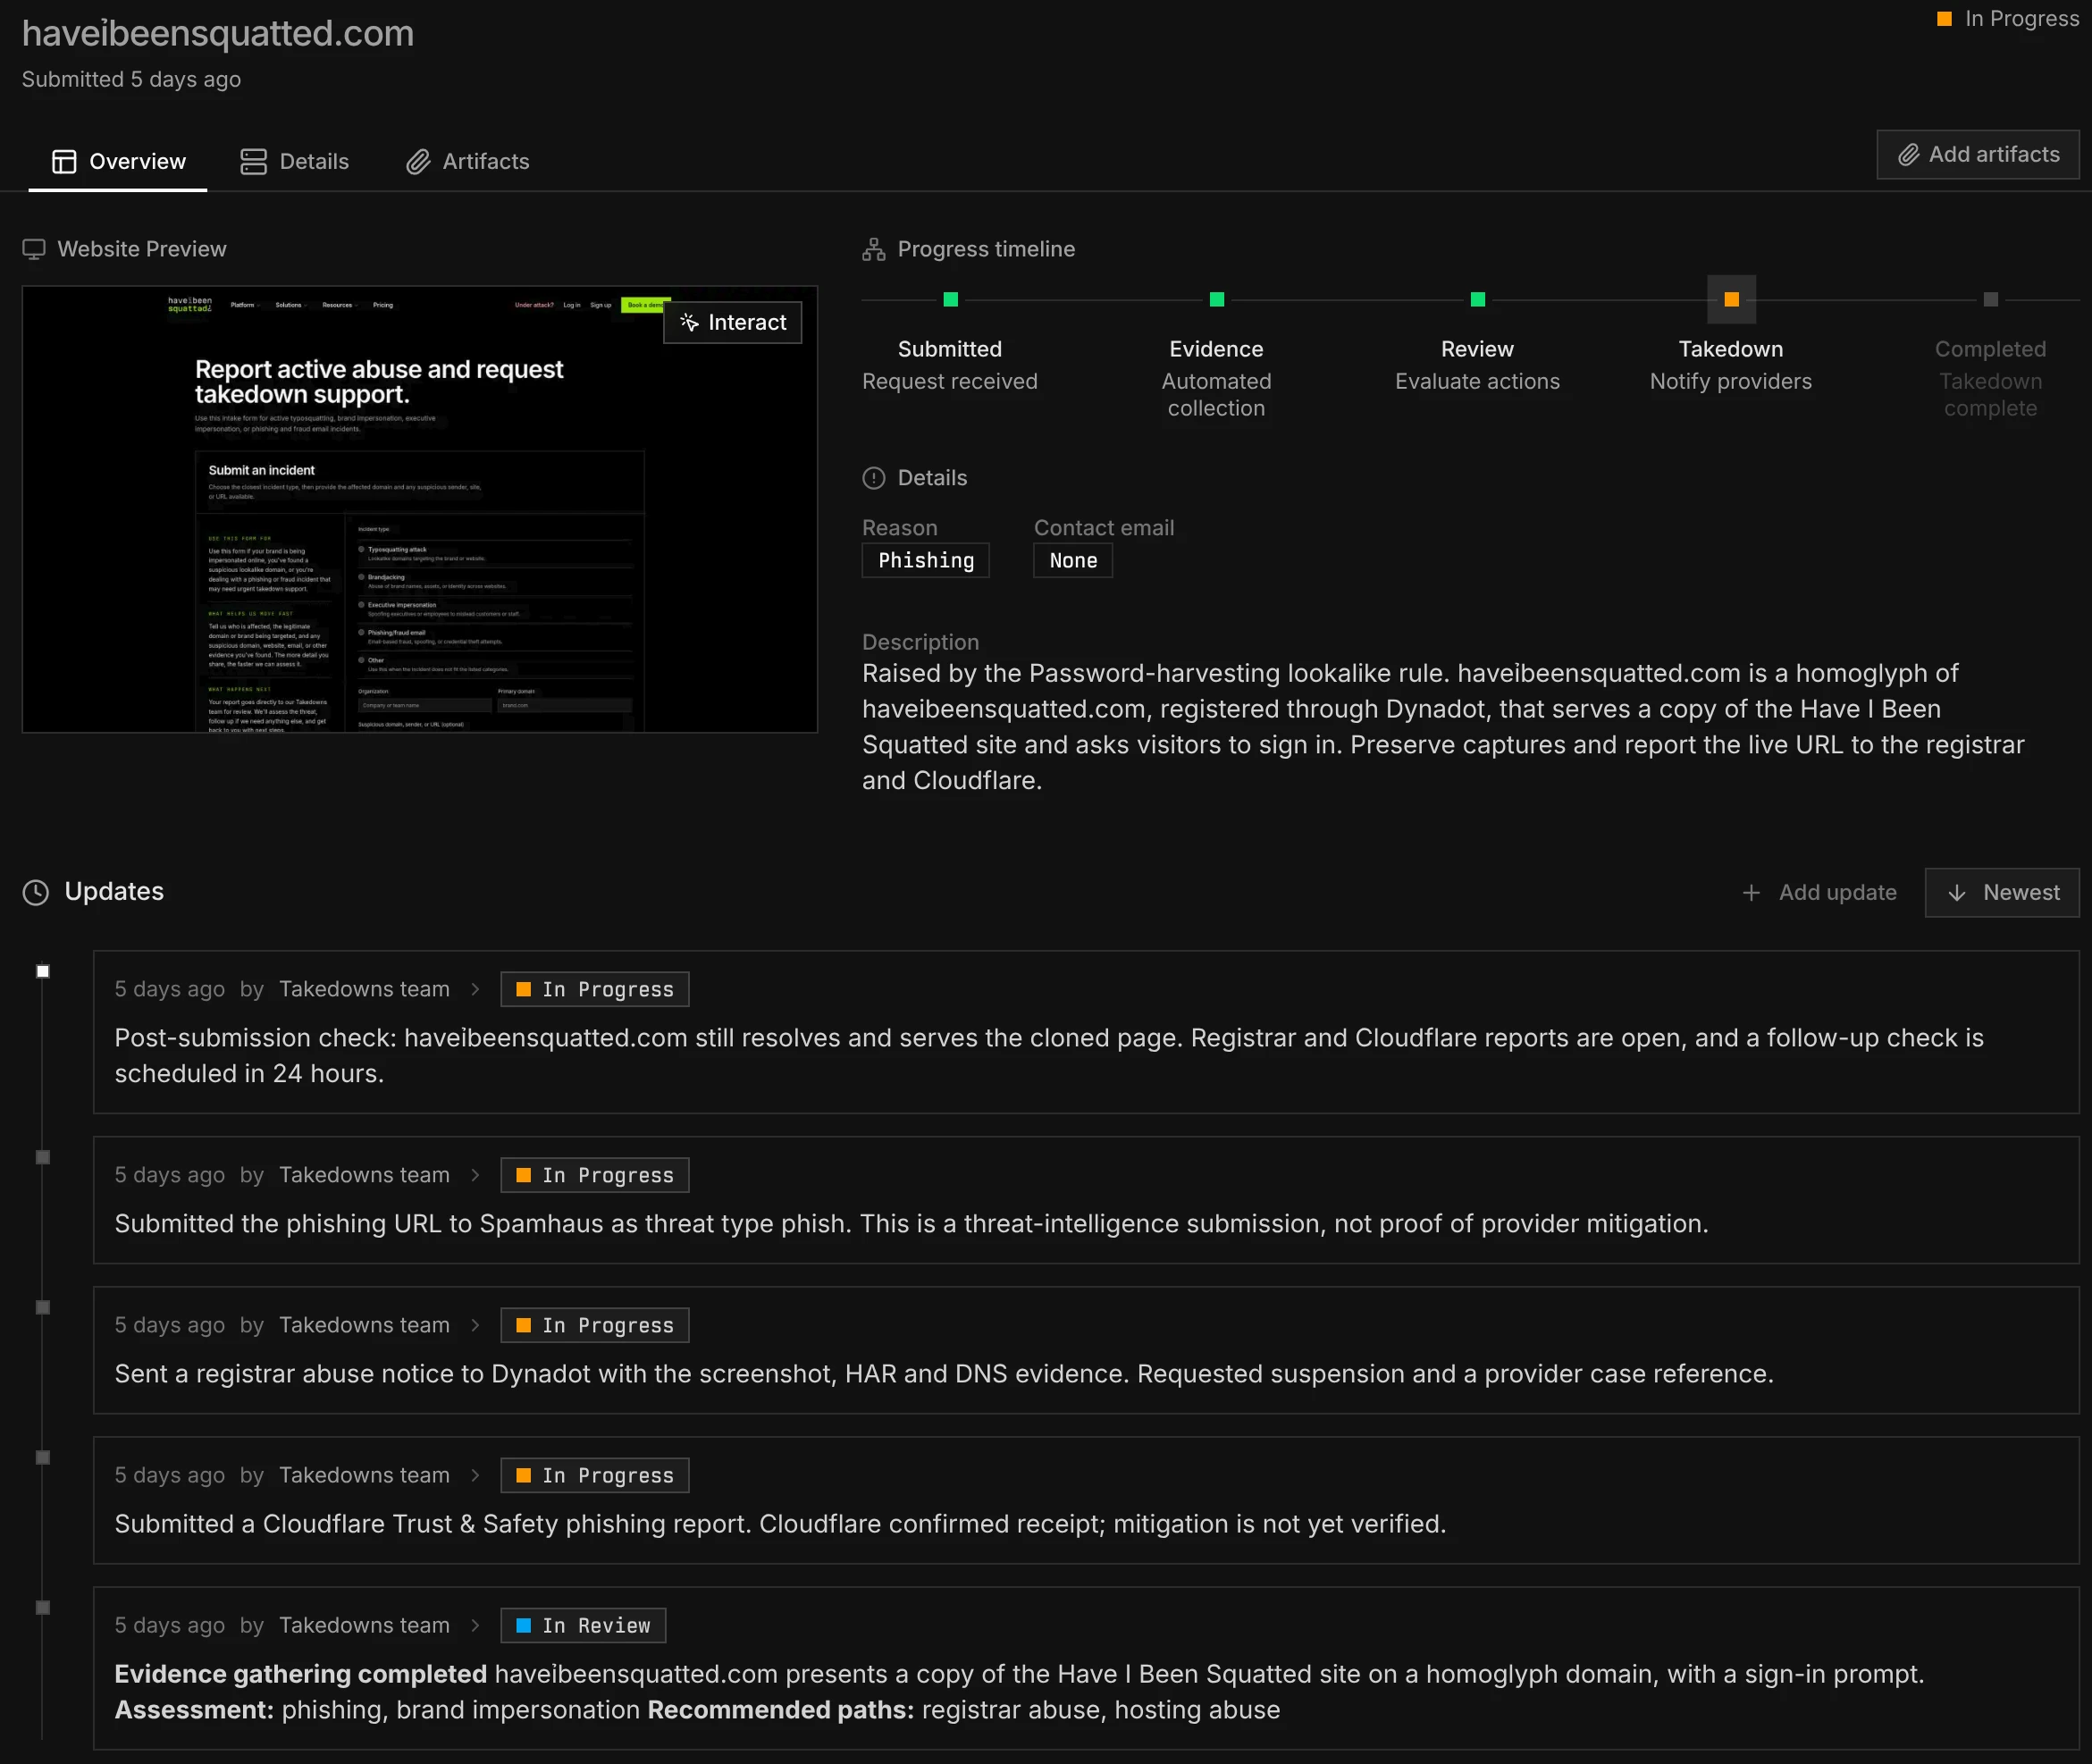
Follow a Takedown from request to outcome.
A demo shows the Takedown case workflow and the Network Enforcement gateways that receive blocks.
Managed takedowns and their targets#
Both products offer managed domain takedowns, and XVigil also takes down fake social accounts, unofficial apps on third-party app stores, fake customer support numbers and DMCA cases. CloudSEK states that its in-house team handles submission, follow-ups and confirmation, and sends the evidence to hosts and registrars. One PeerSpot reviewer describes clicking takedown in the portal and seeing the page removed within three to four working days. 1,3,5–7,26,30
CloudSEK publishes its own takedown results. For the fourth quarter of 2024, it reports more than 2,200 successful takedowns and a 4.1 business day average turnaround. Its 96 percent success rate assumes that pending requests succeed at the same rate. CloudSEK also states that fake social media handles come down in just over two business days. 1,5–7,61
Have I Been Squatted runs managed Takedowns for domains. An analyst reviews every request, and a rule can open a request automatically. The team reports the domain to its host and registrar, then escalates to ICANN and regional CSIRTs where necessary, and it stops short of legal action but can introduce legal partners. Each case shows its status from review through provider notification to completion, with analyst notes. Have I Been Squatted states that, with enough evidence, a registrar or host usually responds within four hours, and that some cases take up to 24 or 72 hours. 31–34,62
Where CloudSEK XVigil is the better choice#
XVigil fits a team whose digital risk reaches well past domains. Nexus AI can link leaked credentials, lookalike domains and phishing pages into a potential attack path. CloudSEK targets mid-market and enterprise organizations in regulated or threat-heavy industries, and PeerSpot users give XVigil an average rating of 8.6 out of 10. 1–2,7,39,63
XVigil also suits buyers who want an in-house team to take down social accounts and apps as well as domains. Its two-way API writes status, comments and remediation back to CloudSEK records. Both products ship an MCP server with write tools, so agent access alone does not separate them. For procurement, CloudSEK lists ISO/IEC 27001, 42001, 22301 and 27017 certifications, and its trust center marks SOC 2 as compliant. Ask CloudSEK for its current SOC 2 report to confirm the report type and scope. CloudSEK sells XVigil by module, singly or combined, and lists 12-month contracts on AWS Marketplace. That listing offers a free trial on terms CloudSEK sets, and CloudSEK also takes requests for free access to XVigil. 1–3,5–7,26,30,50,52–55,57–60,64–66
Where Have I Been Squatted is the better choice#
Pick Have I Been Squatted when your team works malicious domains and the attacker infrastructure behind them, and wants to see what a domain does before acting. Lookalikes of your own domains come from Domain Monitoring, and Analyze inspects any other domain on demand. Results record the redirect chain, the DOM and a HAR capture of network requests, and page semantics flag behavior such as a request for an account password. When the domain serves a site, an analyst can open it in a live, isolated browser session and step through it. 8–12,23,34,57–58,67–68
Two more differences sit at either end of the queue. Domain Monitoring checks your domains continuously, adding certificate transparency and newly registered domains to the lookalikes it generates. Network Enforcement sends rule-flagged domains straight to Zscaler, iboss, Cloudflare Zero Trust and Microsoft Defender for Endpoint. Tools that poll a block list can read a hosted domain feed in seven formats, among them STIX 2.1 and NDJSON, with documented MISP setup. Network Intelligence then shows whether devices on your network connected to a flagged domain. Managed Takedowns cover takedown and disruption of malicious infrastructure, starting with reports to the host and registrar. 14,18–23,31–34,69
A team can sign up and run its first lookups on its own. Monitoring, hunting tools, rules and alerts are self-serve with a free trial, while Takedowns and the email, network, SIEM and canary products are bought through sales. Results leave as a PDF "Domain security overview" or "Compliance readout", or as CSV and JSON exports. Have I Been Squatted has a SOC 2 Type II report, available through its Trust Center, and offers single sign-on with audit logging. 12–13,22,32,34,46,50–51,57–58,69–71
Have I Been Squatted does not monitor social media, app stores, the dark web, ads or leaked credentials. It does not suit a buyer who wants those channels and domain protection from one vendor. XVigil brings those areas into one platform. 1,35–36,39
FAQ#
Have I Been Squatted suits a small team that wants to sign up self-serve for domain monitoring and run domain investigations and rules itself. CloudSEK says it targets mid-market and enterprise organizations, typically with 1,000 or more employees, and sells XVigil on contract, with a trial and free access available on its own terms. Consider XVigil when your remit reaches past domains and you want CloudSEK's team to take down social accounts and apps as well. 1–3,5–7,10–11,13–14,22,34,39
Yes. CloudSEK lists SIEM connectors such as IBM QRadar, can stream alerts to SIEM and SOAR tools through Amazon SQS, and offers a pull-based Integrations API. Have I Been Squatted pushes findings to Splunk, Microsoft Sentinel, Elastic Security, Google SecOps or a webhook when a rule matches. 13–15,29–30,72
Sources and corrections
Each numbered marker on this page links to its sources below. Each source shows the date it was last checked. If a fact is wrong or out of date, send a correction. A correction is checked against the source and the page is updated.
- 1.CloudSEK. “XVigil: Digital Risk Protection Platform.” Accessed . https://www.cloudsek.com/platform/xvigil
- 2.AWS Marketplace (seller: CloudSEK). “CloudSEK XVigil - External Digital Risk Protection.” Accessed . https://aws.amazon.com/marketplace/pp/prodview-hwpvn62c5w7t6
- 3.CloudSEK. “Brand Threat Monitoring.” Accessed . https://www.cloudsek.com/brand-monitor
- 4.CloudSEK. “Fake Pages & Channels Monitoring by CloudSEK's XVigil (10 April 2025).” Accessed . https://www.cloudsek.com/blog/protecting-your-brand-in-the-digital-age-fake-pages-channels-monitoring-by-cloudseks-xvigil
- 5.CloudSEK. “Protect Your Brand with CloudSEK's Expert Takedown Services.” Accessed . https://www.cloudsek.com/platform/takedowns
- 6.IT Voice. “CloudSEK's Takedown Service Neutralizes Thousands of Malicious Online Threats (17 July 2023).” Accessed . https://www.itvoice.in/cloudseks-takedown-service-neutralizes-thousands-of-malicious-online-threats-enhancing-cybersecurity-landscape
- 7.PeerSpot. “CloudSEK XVigil Reviews.” Accessed . https://www.peerspot.com/products/cloudsek-xvigil-reviews
- 8.Have I Been Squatted. “Homepage (footer tagline).” Accessed . https://haveibeensquatted.com/
- 9.Have I Been Squatted. “Platform.” Accessed . https://haveibeensquatted.com/platform
- 10.Have I Been Squatted. “Changelog.” Accessed . https://haveibeensquatted.com/changelog
- 11.Have I Been Squatted. “Domain signals.” Accessed . https://docs.haveibeensquatted.com/reference/signals/domain/
- 12.Have I Been Squatted. “Access control reference.” Accessed . https://docs.haveibeensquatted.com/reference/access-control/
- 13.Have I Been Squatted. “Rules engine guide.” Accessed . https://docs.haveibeensquatted.com/guides/rules-engine/
- 14.Have I Been Squatted. “Network Intelligence guide.” Accessed . https://docs.haveibeensquatted.com/features/network-intelligence/
- 15.Have I Been Squatted. “Integrations.” Accessed . https://haveibeensquatted.com/platform/integrations
- 16.Have I Been Squatted. “Alert digest guide.” Accessed . https://docs.haveibeensquatted.com/guides/digest/
- 17.Have I Been Squatted. “Connectors.” Accessed . https://docs.haveibeensquatted.com/integrations/
- 18.Have I Been Squatted. “Network Enforcement.” Accessed . https://haveibeensquatted.com/platform/network-enforcement
- 19.Have I Been Squatted. “Domain feed integration.” Accessed . https://docs.haveibeensquatted.com/integrations/domain-feed/
- 20.Have I Been Squatted. “CrowdStrike Falcon integration.” Accessed . https://docs.haveibeensquatted.com/integrations/crowdstrike-falcon/
- 21.Have I Been Squatted. “Microsoft Defender for Endpoint integration.” Accessed . https://docs.haveibeensquatted.com/integrations/microsoft-defender-endpoint/
- 22.Have I Been Squatted. “Domain Monitoring.” Accessed . https://haveibeensquatted.com/platform/monitoring
- 23.Have I Been Squatted. “Domain monitoring guide.” Accessed . https://docs.haveibeensquatted.com/features/domain-monitoring/
- 24.CloudSEK. “XVigil's Fake Domain Finder: A Deep-dive on the Acquisition Component and Crawlers (9 July 2021).” Accessed . https://www.cloudsek.com/blog/xvigils-fake-domain-finder-a-deep-dive-on-the-acquisition-component-and-crawlers
- 25.CloudSEK. “Cybercriminals Hate This! CloudSEK's Fake Domains Observer is Changing the Game (11 February 2025).” Accessed . https://www.cloudsek.com/blog/cybercriminals-hate-this-cloudseks-fake-domains-observer-is-changing-the-game
- 26.CloudSEK. “Available tools.” Accessed . https://api.cloudsek.com/docs/mcp/available-tools
- 27.Have I Been Squatted. “Email Intelligence guide.” Accessed . https://docs.haveibeensquatted.com/features/email-intelligence/
- 28.Have I Been Squatted. “Email Intelligence.” Accessed . https://haveibeensquatted.com/platform/email-intelligence
- 29.CloudSEK. “Integrations.” Accessed . https://www.cloudsek.com/integrations
- 30.CloudSEK. “CloudSEK Platform: Public API Documentation.” Accessed . https://api.cloudsek.com/
- 31.Have I Been Squatted. “Takedowns.” Accessed . https://haveibeensquatted.com/platform/takedowns
- 32.Have I Been Squatted. “Takedowns guide.” Accessed . https://docs.haveibeensquatted.com/features/takedowns/
- 33.Have I Been Squatted. “FAQ (stalled takedowns).” Accessed . https://haveibeensquatted.com/faq#takedowns-stall
- 34.Have I Been Squatted. “Pricing FAQ (takedowns).” Accessed . https://haveibeensquatted.com/pricing
- 35.Have I Been Squatted. “Solutions.” Accessed . https://haveibeensquatted.com/solutions
- 36.Have I Been Squatted. “Brand protection.” Accessed . https://haveibeensquatted.com/solutions/brand-protection
- 37.CloudSEK. “Deep and Dark Web Monitoring.” Accessed . https://www.cloudsek.com/cyber-threats/dark-web-monitoring
- 38.CloudSEK. “BeVigil.” Accessed . https://www.cloudsek.com/platform/bevigil
- 39.CloudSEK. “Official Information About CloudSEK (BeVigil).” Accessed . https://www.cloudsek.com/llm-info
- 40.CloudSEK. “Threat Intelligence, CloudSEK CTI Module.” Accessed . https://www.cloudsek.com/platform/threat-intelligence
- 41.Have I Been Squatted. “Site Canaries.” Accessed . https://haveibeensquatted.com/platform/site-canaries
- 42.Have I Been Squatted. “Site Canaries guide.” Accessed . https://docs.haveibeensquatted.com/features/site-canaries/
- 43.Have I Been Squatted. “Atlas observations: registration data by TLD.” Accessed . https://mcp.haveibeensquatted.com/mcp
- 44.Have I Been Squatted. “Passive DNS guide.” Accessed . https://docs.haveibeensquatted.com/features/passive-dns/
- 45.Spamhaus. “Spamhaus passive DNS endpoint, unauthenticated probe.” Accessed . https://beta-pdns.spamhaus.com/api/v3/login
- 46.Have I Been Squatted. “Atlas investigations.” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/
- 47.Have I Been Squatted. “Atlas investigations (add domains and indicators).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#steer-an-investigation
- 48.Have I Been Squatted. “Atlas investigations (shareable view links).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#read-the-map
- 49.Have I Been Squatted. “Atlas investigations (New investigation flow).” Accessed . https://docs.haveibeensquatted.com/features/atlas-investigations/#start-an-investigation
- 50.Have I Been Squatted. “Reports guide.” Accessed . https://docs.haveibeensquatted.com/features/reports/
- 51.Have I Been Squatted. “Explore guide.” Accessed . https://docs.haveibeensquatted.com/features/explore/
- 52.CloudSEK. “Getting Started.” Accessed . https://api.cloudsek.com/docs/intro
- 53.CloudSEK. “Get live incident alerts.” Accessed . https://api.cloudsek.com/docs/api/get-alerts
- 54.CloudSEK. “CloudSEK Alerts, Incidents and Events APIs, including the Bi-Directional (Two-Way) Suite.” Accessed . https://api.cloudsek.com/docs/api/cloudsek-alerts-incidents-and-events-apis-including-the-bi-directional-two-way-suite/
- 55.CloudSEK. “CloudSEK MCP Server.” Accessed . https://www.cloudsek.com/mcp
- 56.CloudSEK. “CloudSEK MCP setup guide.” Accessed . https://api.cloudsek.com/docs/mcp/
- 57.Have I Been Squatted. “Agents.” Accessed . https://haveibeensquatted.com/platform/agents
- 58.Have I Been Squatted. “MCP server.” Accessed . https://docs.haveibeensquatted.com/ai/mcp/
- 59.Have I Been Squatted. “Slack app.” Accessed . https://docs.haveibeensquatted.com/ai/slack/
- 60.Have I Been Squatted. “MCP server (OAuth scopes).” Accessed . https://docs.haveibeensquatted.com/ai/mcp/#oauth-scopes
- 61.CloudSEK. “Your Brand Guardians: A Deep Dive into CloudSEK's Takedown Services (dated 29 May 2024, cites Q4 2024).” Accessed . https://www.cloudsek.com/blog/your-brand-guardians-a-deep-dive-into-cloudseks-takedown-services
- 62.Have I Been Squatted. “BBI Logistics customer story.” Accessed . https://haveibeensquatted.com/customers/bbi-logistics
- 63.CloudSEK. “CloudSEK Raises $19 Million in Series B1 Funding (20 May 2025).” Accessed . https://www.cloudsek.com/blog/cloudsek-raises-19-million-in-series-b1-funding-to-scale-predictive-cybersecurity-platform
- 64.CloudSEK. “CloudSEK's Trust Center.” Accessed . https://trust.cloudsek.com/
- 65.CloudSEK. “Commitment to Compliance.” Accessed . https://www.cloudsek.com/compliance
- 66.CloudSEK. “Privacy Policy.” Accessed . https://www.cloudsek.com/privacy-policy
- 67.Have I Been Squatted. “API: Analyze a URL.” Accessed . https://docs.haveibeensquatted.com/guides/api/analyze/#analyze-a-url
- 68.Have I Been Squatted. “Tools: Analyze (URL analysis note, served without sign-in).” Accessed . https://haveibeensquatted.com/app/tools?mode=analyze
- 69.Have I Been Squatted. “Network Intelligence.” Accessed . https://haveibeensquatted.com/platform/network-intelligence
- 70.Have I Been Squatted. “Security.” Accessed . https://haveibeensquatted.com/about/security
- 71.Have I Been Squatted. “Administration guide.” Accessed . https://docs.haveibeensquatted.com/guides/administration/
- 72.Have I Been Squatted. “Webhooks.” Accessed . https://docs.haveibeensquatted.com/integrations/webhooks/